
IKEv2 to an Azure VPN gateway starts and the IPsec SA never forms. The router offers a Diffie-Hellman group the gateway is not configured to accept. The pre-shared key matches. What must change?
Select an answer to reveal the explanation.
Short Explanation
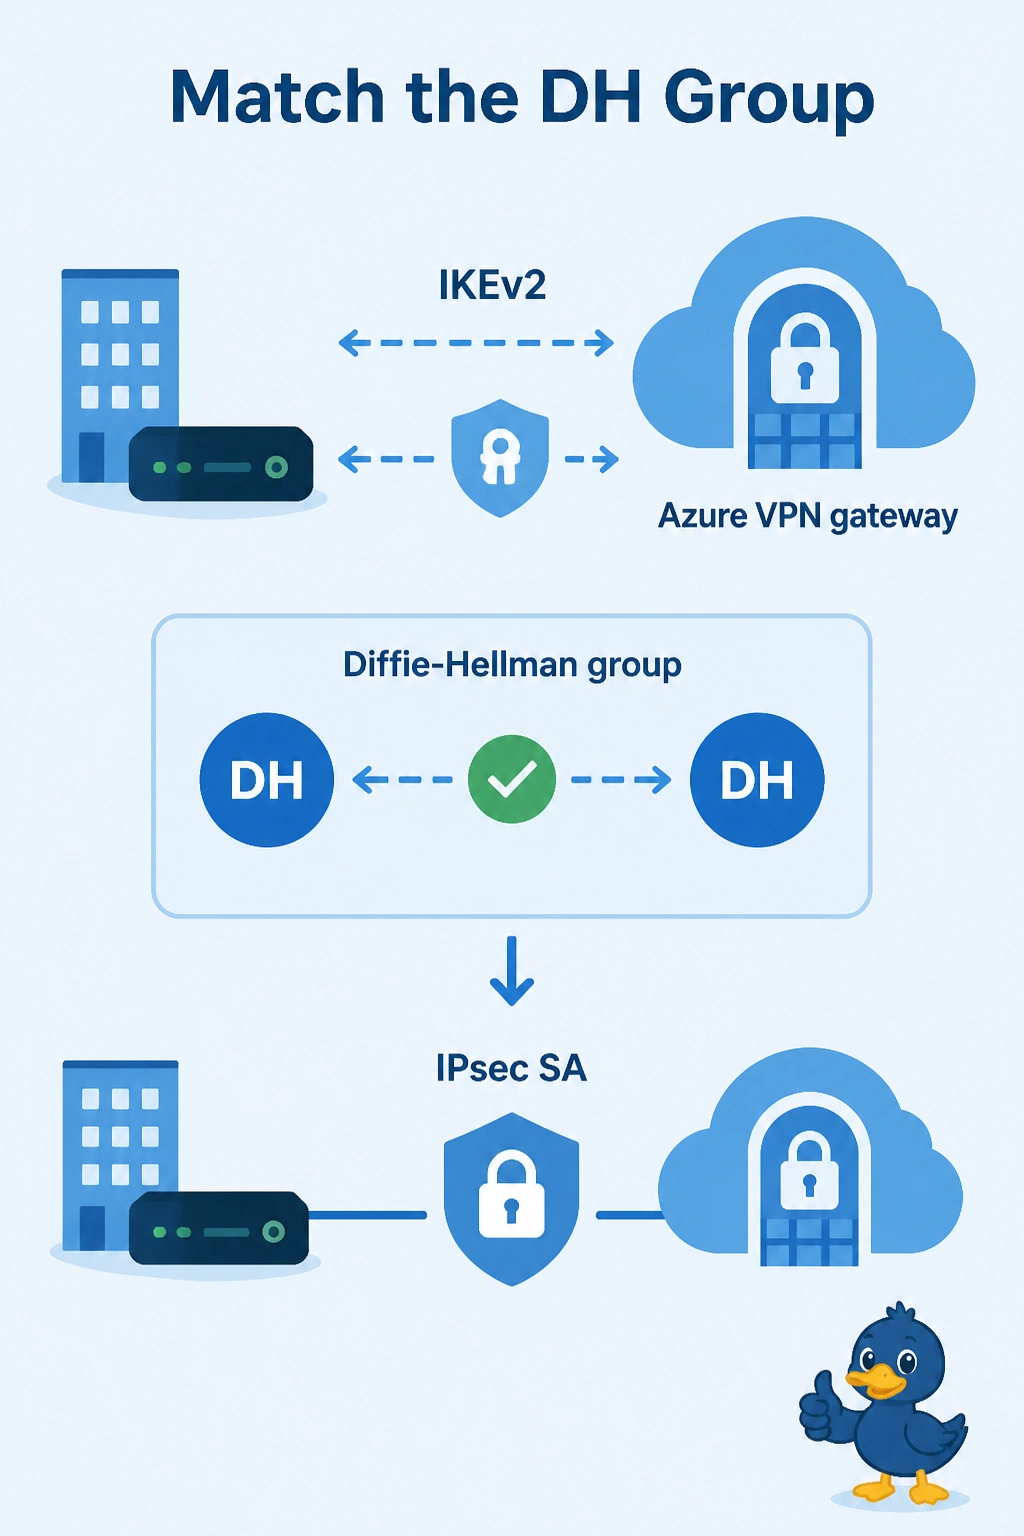
The password is right and the handshake you offered is one Azure will not finish. You change the Diffie-Hellman group to one the gateway accepts. The key already matches, so this is the proposal, not the password.
Full Explanation
The IPsec SA is negotiated from the groups and ciphers both ends accept. This router offers a Diffie-Hellman group the Azure connection is not configured to use, so IKE can start and the IPsec SA still never forms. Offer a group the gateway accepts, or add that group on the Azure side if the connection allows it. One of the two proposals has to include a shared group. The BGP ASN is not copied into the Diffie-Hellman group. The OSPF dead interval is unrelated, and Azure VPN Gateway is not an OSPF peer. Anti-replay does not select the group. It only matters after an SA exists. Exam caveat: a matching group with a cipher the gateway also rejects will still fail. Compare the whole proposal, not only the group, if the SA stays down after this change. Operational check: the router's proposal and the Azure connection should list a common group, and show crypto ipsec sa should show an SA.