
Small pings across a cloud IOS XE tunnel work. Large TCP transfers hang. TCP MSS adjustment is configured on the physical internet interface and not on the tunnel. Where should it be applied?
Select an answer to reveal the explanation.
Short Explanation
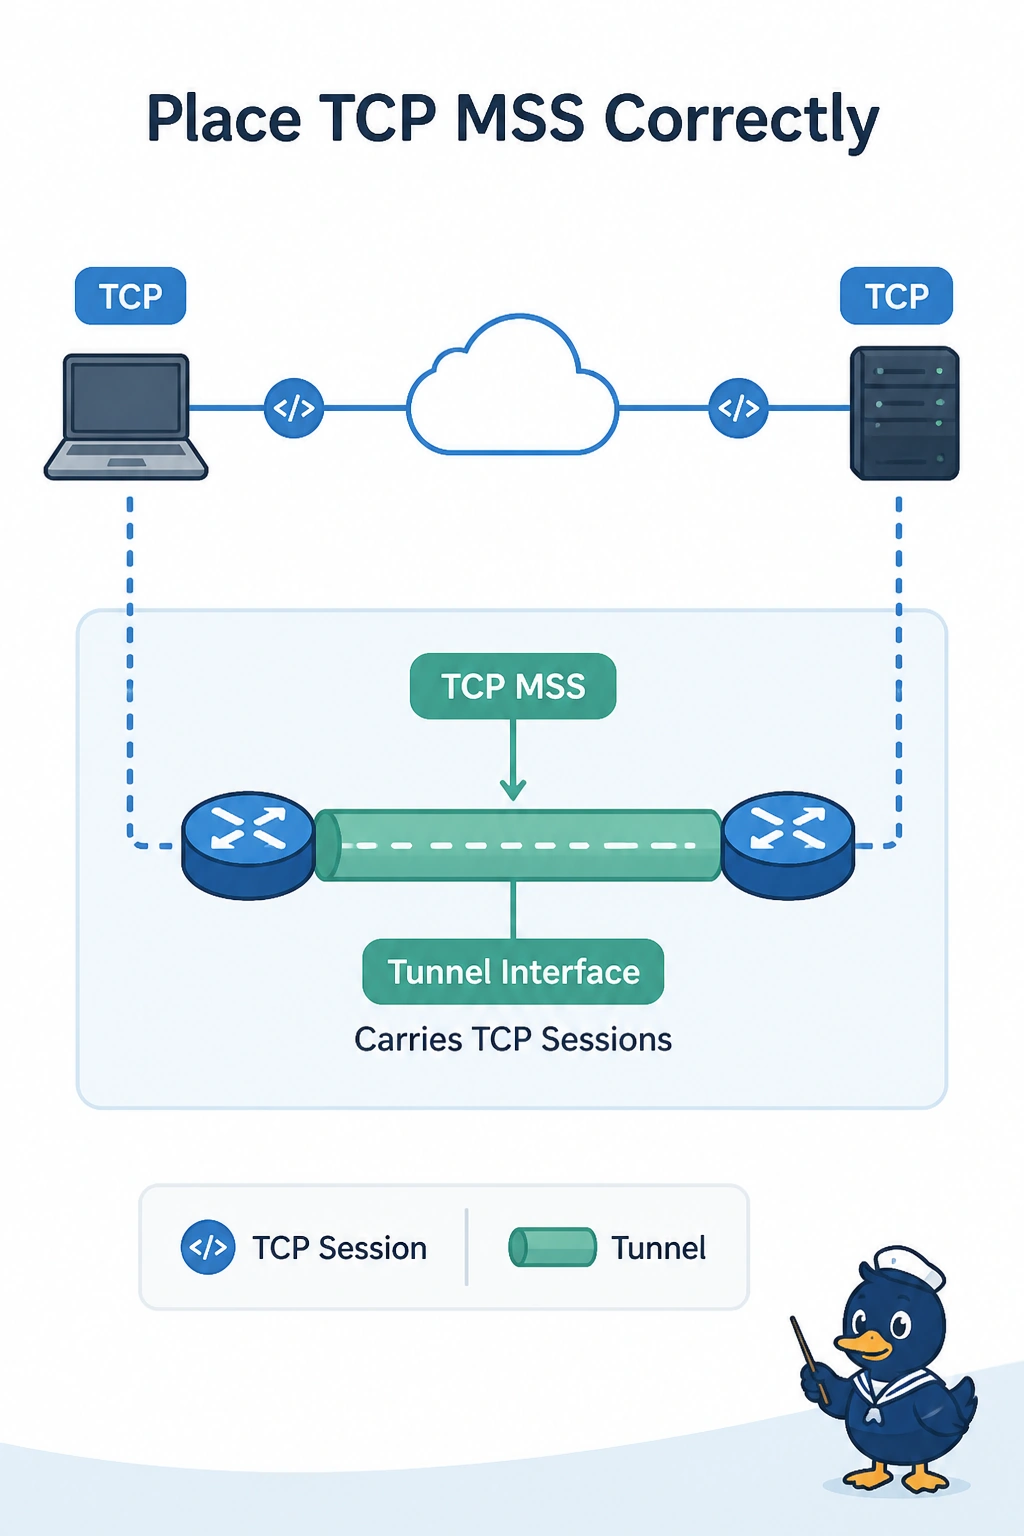
You clamped the door the users are not walking through. You apply TCP MSS adjustment on the tunnel that actually carries the sessions. The physical interface can look correct and still never see the TCP handshake inside the tunnel.
Full Explanation
TCP MSS adjustment changes the handshake so the session fits the tunnel. It has to sit on the interface the TCP session crosses. This router clamps the physical internet interface, while the sessions are encapsulated on the tunnel and never hit that clamp, so small pings work and large TCP hangs. Move the adjustment onto the tunnel interface. A loopback that the sessions do not cross does nothing. A virtual private gateway is not in this router-to-router path and does not clamp MSS for it. VPN 512 is an SD-WAN management VPN and is not where this IOS XE tunnel's MSS is set. Exam caveat: clamp both ends if both can originate the handshake. One side can be enough only if every session is seen on that tunnel interface. Operational check: the tunnel interface should show the MSS adjustment, and a large transfer should complete without hanging.