
Campus IKE to a cloud-hosted Cisco IOS XE router never arrives on the tunnel. The cloud firewall allows UDP 500 and UDP 4500. An ACL on the router's internet-facing interface denies those ports. What must change?
Select an answer to reveal the explanation.
Short Explanation
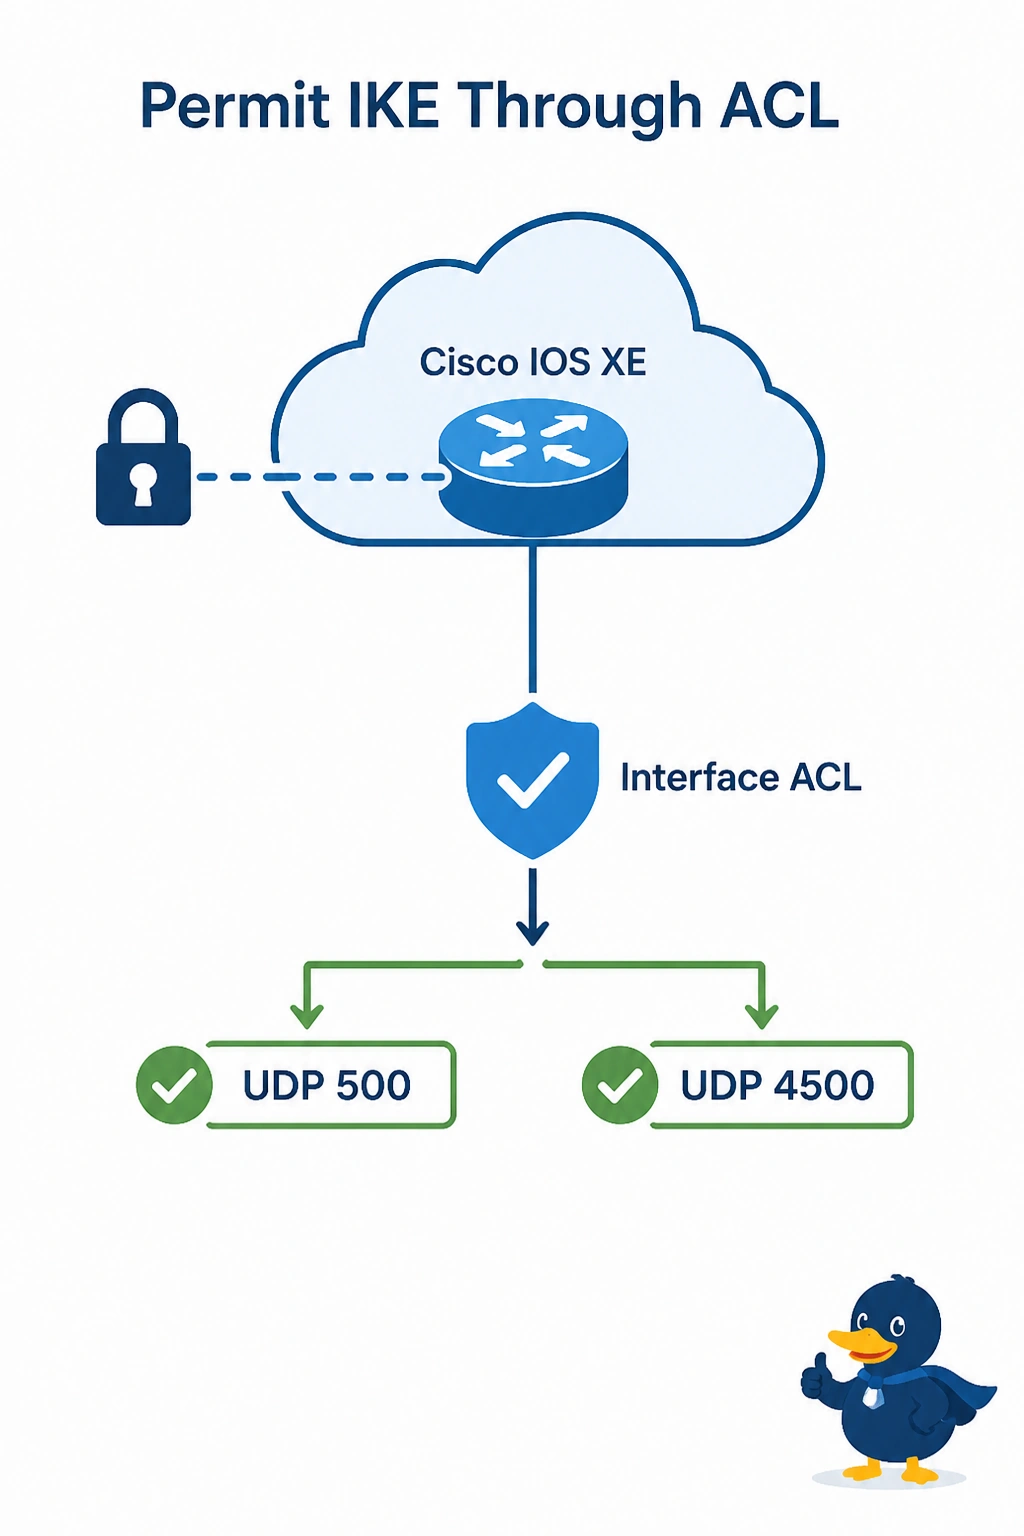
You’ve opened the building door, but the office door is still locked. The cloud firewall already allows UDP 500 and UDP 4500, while the router’s interface ACL denies them, so you need to permit those ports there. The OSPF hello timer and BGP ASN do not stand in front of IKE.
Full Explanation
Packets that pass the cloud firewall still have to pass the Cisco IOS XE router’s interface ACL. The ACL denies UDP 500 and UDP 4500 on the internet-facing interface, so IKE never reaches the tunnel process; permit those ports from the campus on that ACL. Changing the cloud firewall does not help because it already allows the traffic, and the drop happens later, at the router. The OSPF hello timer is not a gate for IKE: IKE does not wait for OSPF adjacency before arriving at the router. The BGP ASN is not evaluated on UDP 500, and BGP cannot start until the tunnel exists. Exam caveat: an outbound ACL can also drop the router’s IKE replies, even after the inbound rule is fixed. Check both directions on the interface. As a practical check, confirm the ACL shows permits for UDP 500 and UDP 4500, then capture traffic on the interface to verify that the campus exchange reaches the router.