
Instances in a VPC send return traffic for the campus prefix to the internet gateway. The cloud IOS XE router has the campus route, and the subnet route table has no entry for the campus prefix. What should the route table use as the target?
Select an answer to reveal the explanation.
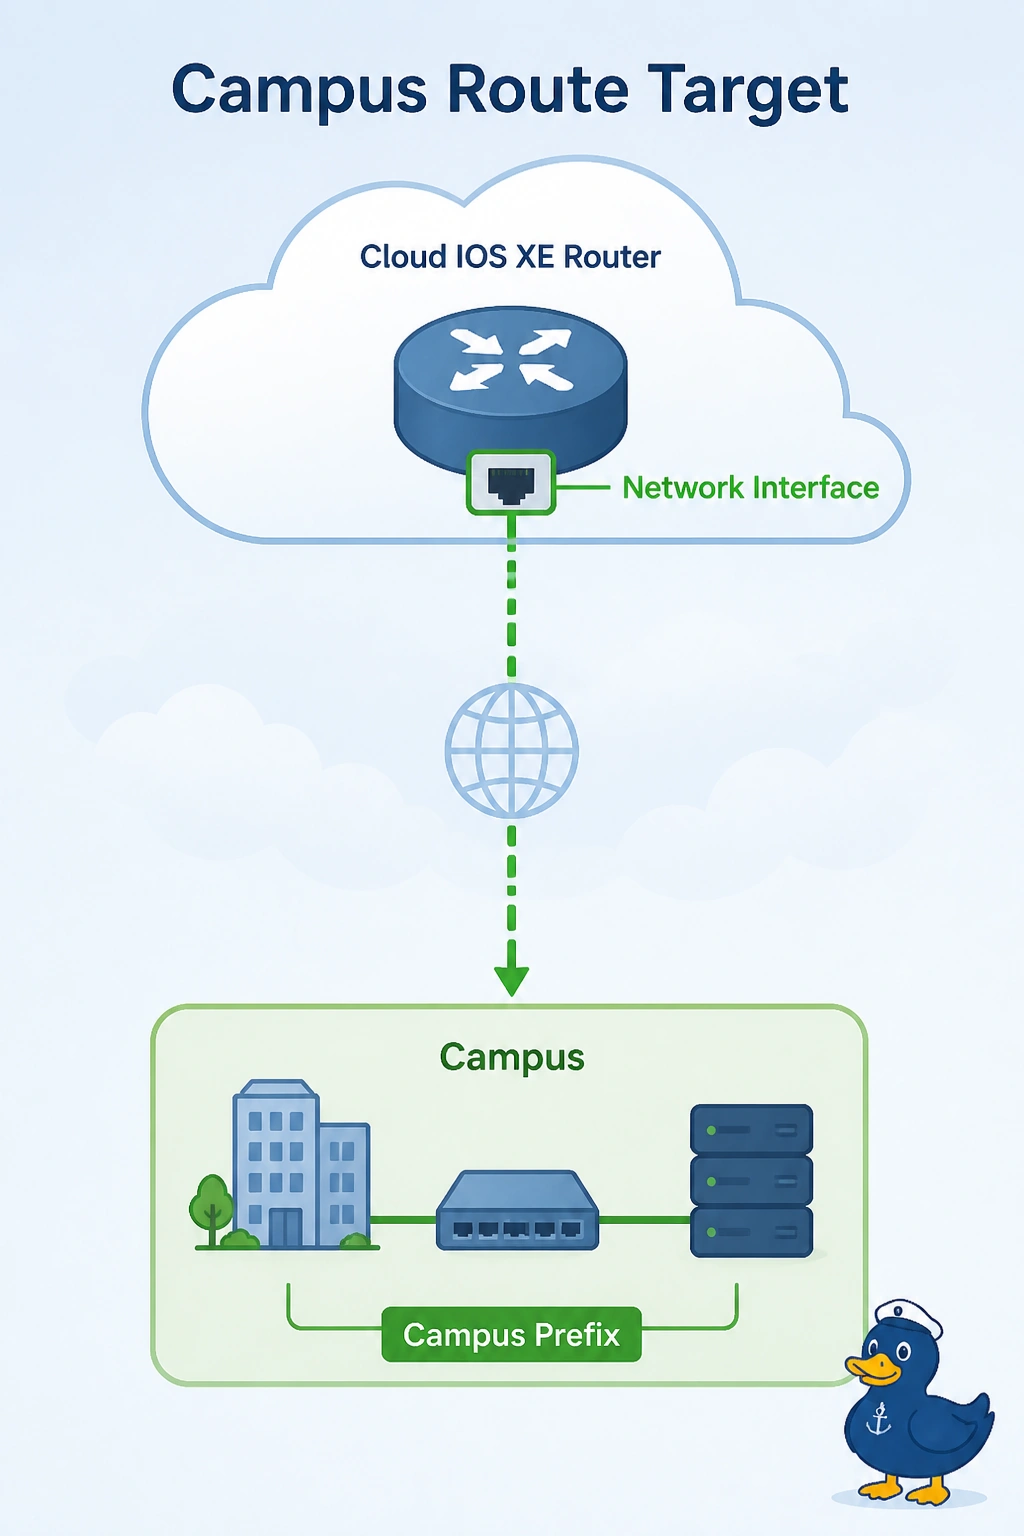
Short Explanation
The instances follow the subnet map, and that map never mentions the campus. You point the campus prefix at the cloud router's network interface. Sending the return to the internet gateway walks it out the wrong door, and this tunnel does not terminate on the native gateway.
Full Explanation
VPC instances forward by the subnet route table, not by the routing table inside the Cisco IOS XE router. If the campus prefix is missing, the default route sends the return to the internet gateway and the session fails even though the cloud router itself knows the campus route. Add a route for the campus prefix with the cloud router's network interface as the target. Targeting the internet gateway is the failure. It does not inspect traffic into the tunnel. A public virtual interface is a Direct Connect object for public AWS services. It is not the next hop for these instances. The native virtual private gateway is not the tunnel endpoint in this design. The IOS XE router is, so the route table must target that router. Exam caveat: the more specific campus route must beat any default to the internet gateway. A summary that does not cover the campus prefix leaves the default in charge. Operational check: the subnet route table should show the campus prefix toward the virtual router's interface, and an instance trace should hit that interface before it enters the tunnel.