
A campus VPN was moved from an AWS virtual private gateway to a transit gateway. The IOS XE router still targets the old gateway's outside address and BGP neighbor. Tunnels to the new gateway stay down. What must be retargeted?
Select an answer to reveal the explanation.
Short Explanation
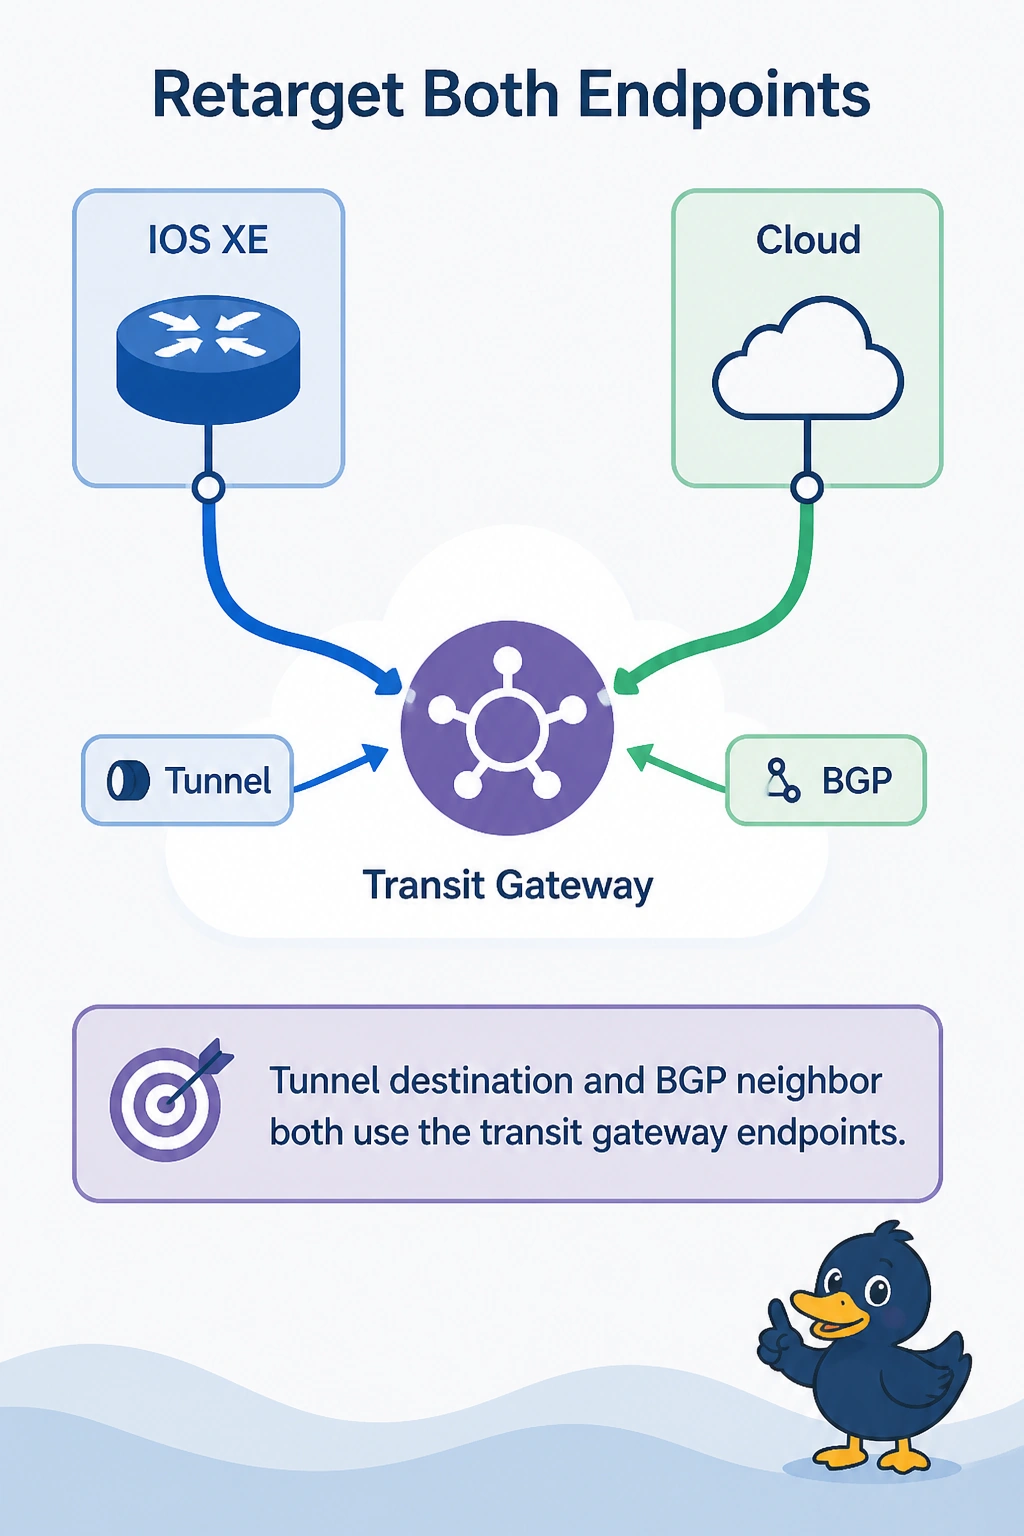
You moved the building and left the truck driving to the old address. You retarget the tunnel destination and the BGP neighbor to the transit gateway endpoints. Changing an OSPF process ID does not select a gateway AWS does not run OSPF on.
Full Explanation
A transit gateway VPN has its own outside tunnel addresses and its own BGP peer addresses. The virtual private gateway endpoints do not answer for that new connection. The router has to change the tunnel destination and the BGP neighbor to the values on the transit gateway VPN. Leaving either one on the old gateway keeps the new tunnel down or the new session idle. An OSPF process ID is local and is not how AWS chooses a transit gateway. The virtual private gateway and the transit gateway do not run OSPF with the campus. An IKE identity hostname does not rewrite the outside IP the router is trying to reach. This is a standalone IOS XE router. An SD-WAN site ID is not part of the transit gateway handshake. Exam caveat: transit gateway VPN connections still come in pairs of tunnels. Retarget both, not only the first outside address in the old notes. Operational check: the router peer addresses should match the transit gateway VPN's outside and inside addresses, and show crypto ipsec sa plus show ip bgp summary should both recover.