
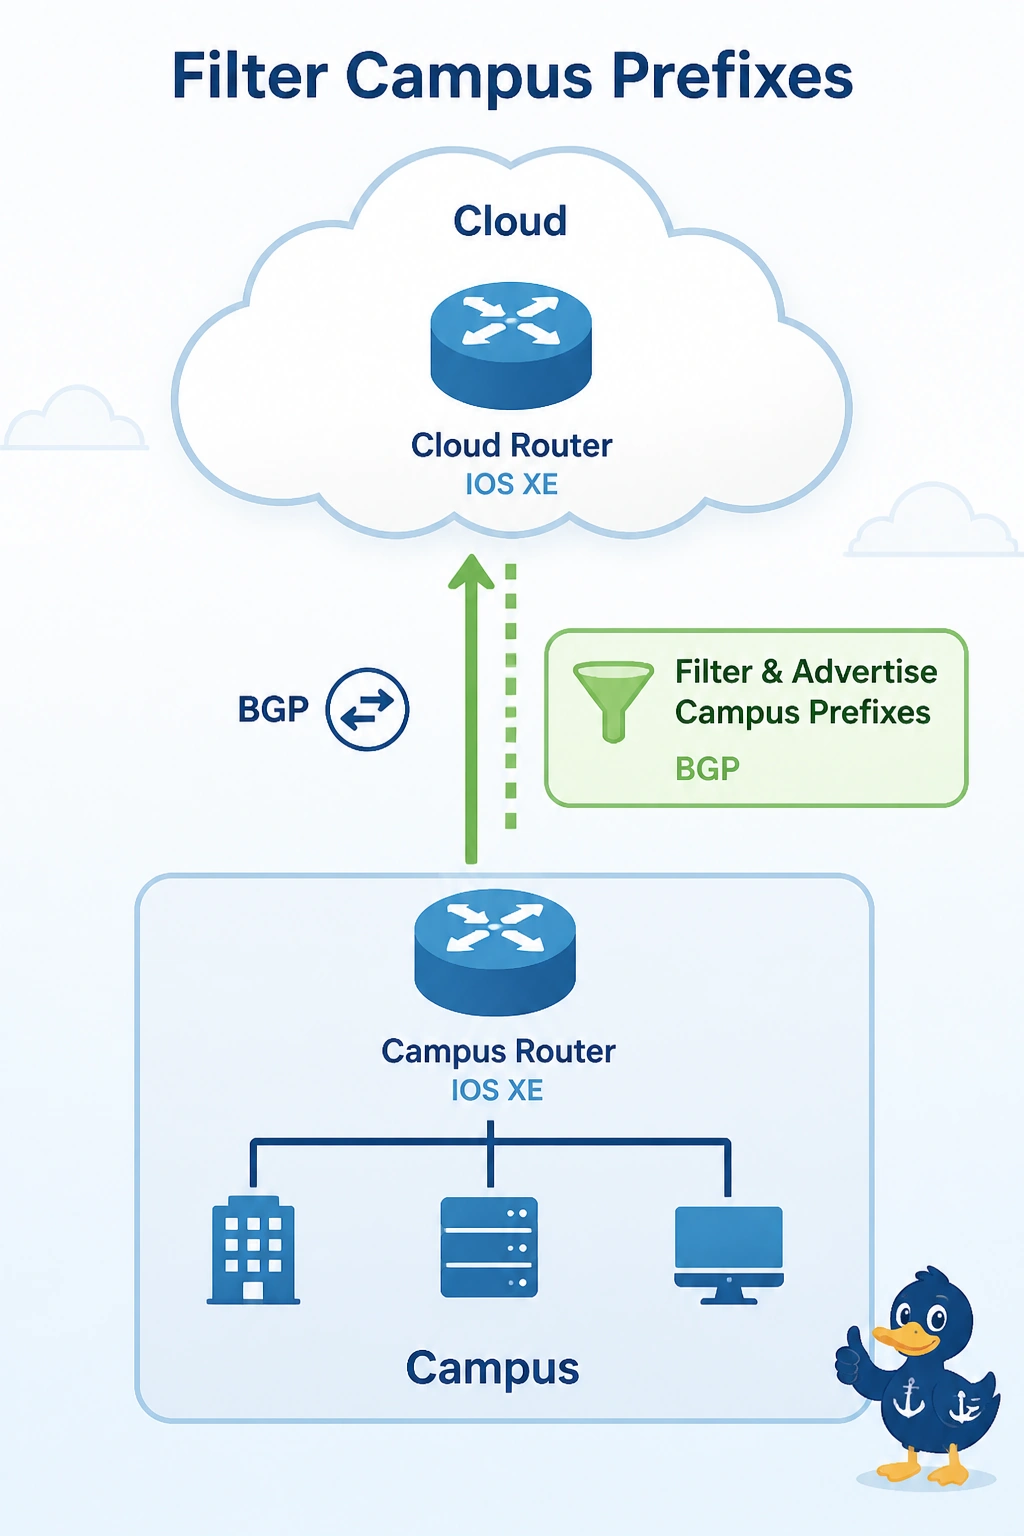
A cloud IOS XE router learns campus prefixes by BGP and redistributes them into a second BGP session that also faces the campus. The campus starts preferring the path that points back at the cloud router. No outbound filter exists. What should be filtered?
Select an answer to reveal the explanation.
Short Explanation
The cloud router learned your prefixes and then offered them back to you as if they were its own. You filter those campus prefixes on the way back out. Otherwise the campus prefers a path that points at the cloud router and walks in a circle.
Full Explanation
Redistribution without an outbound filter lets the cloud router advertise a campus prefix it just learned back toward the campus. The campus can then prefer that advertisement and send the traffic to the cloud router, which sends it toward the campus again. Deny the campus prefixes on the advertisement from the cloud router toward the campus, and keep advertising the VPC prefixes the campus actually needs. Filtering all VPC prefixes removes the routes the tunnel is for and leaves the loop as the remaining path. The IKE identity is not a BGP prefix. A routing loop does not mean a certificate was re-advertised, and the tunnel can stay up the entire time. The virtual private gateway is not the speaker that redistributed these routes. The cloud IOS XE router is. Exam caveat: a route tag is the usual way to do this filter so you do not have to name every campus prefix by hand. Tag on the way in, and deny the tag on the way back out. Operational check: show ip bgp on the campus router should no longer list the cloud router as the best path for a campus prefix.