
A manufacturer's Cisco IOS XE router in an AWS VPC has an up IPsec tunnel to the plant. The VPC route table already points the plant prefix at that router. The plant's routing table has no VPC prefix. The cloud router never advertises its connected VPC subnet. What should be added?
Select an answer to reveal the explanation.
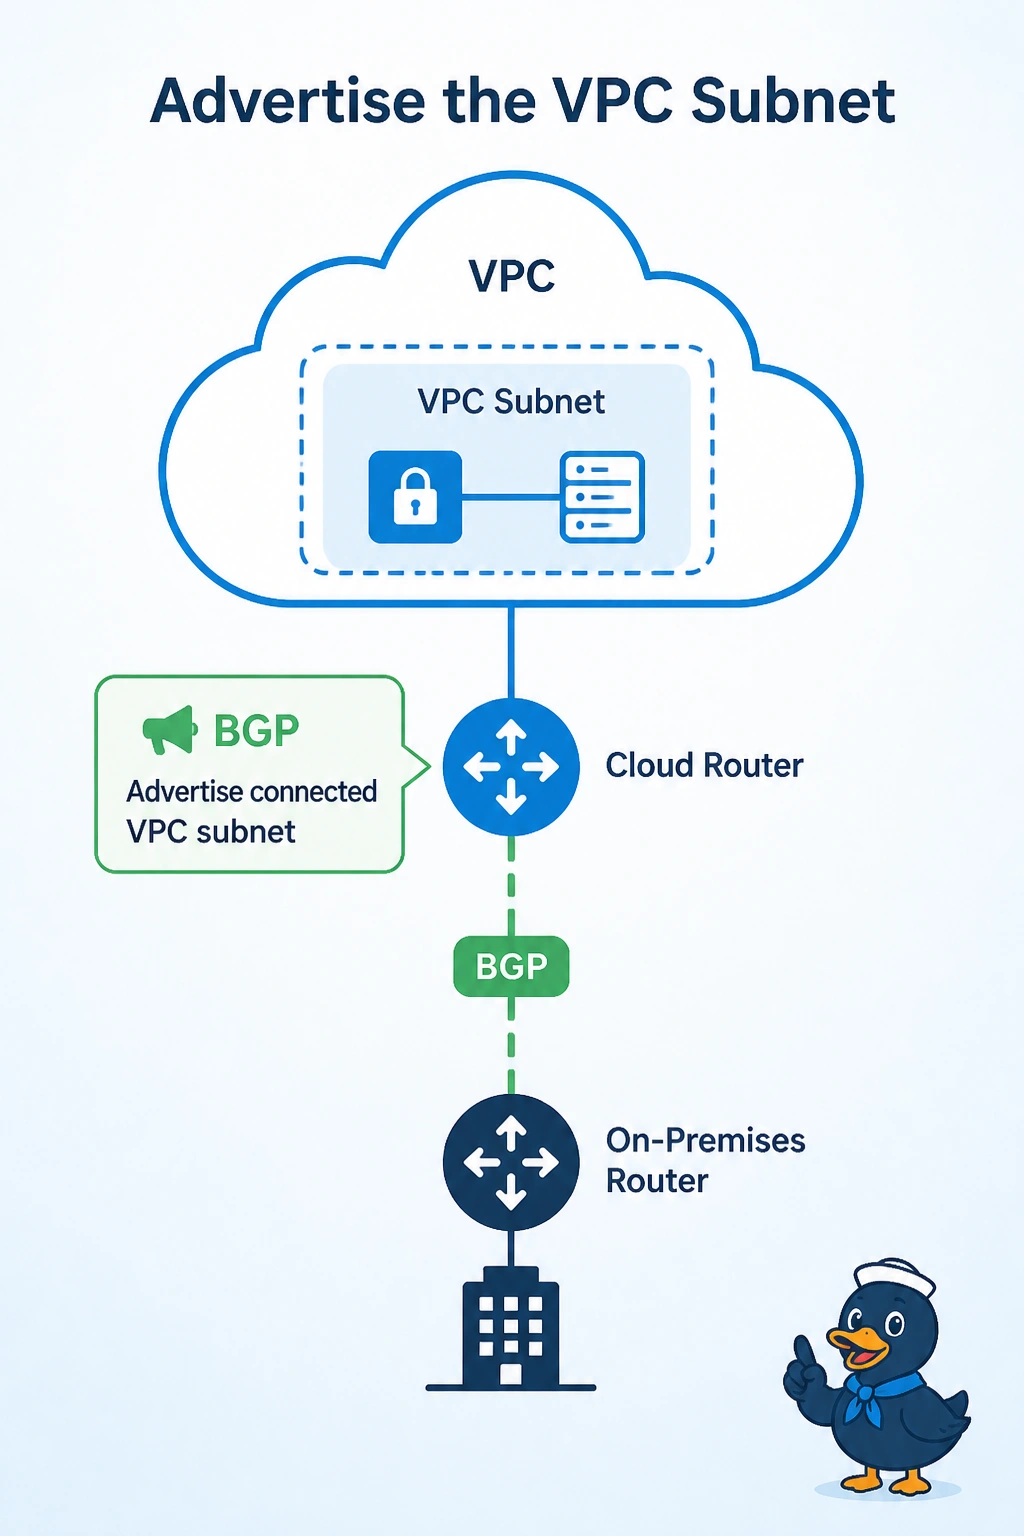
Short Explanation
The return address is written on the envelope, and nobody mailed the letter. You advertise the connected VPC subnet from the cloud IOS XE router toward the plant. The tunnel is up and the VPC route table is already aimed the right way, so another IKE proposal will not create the missing advertisement.
Full Explanation
The cloud-hosted IOS XE router is the speaker that must tell the plant about the VPC subnet. A BGP network statement that matches the connected prefix, or a controlled redistribution of connected routes, puts that subnet into the update toward the plant. Until then the plant has no route, even though IPsec is up and the VPC route table already sends plant traffic to the cloud router's NIC. The virtual private gateway does not own this advertisement and does not run OSPF. A second IKE proposal does not install routes. The SA is up, so the proposal already succeeded. A public virtual interface is a Direct Connect object for public AWS services. It is not how a virtual router advertises its connected subnet. Exam caveat: redistribute connected without a filter can also advertise tunnel and management addresses. Match the VPC subnet on purpose. Operational check: show ip bgp neighbors advertised-routes on the cloud router should list the VPC subnet, and the plant routing table should install it toward the tunnel.