
A partner must reach one published application in a VPC and must not reach the rest of the VPC. A full site-to-site VPN from the partner is proposed. What fits?
Select an answer to reveal the explanation.
Short Explanation
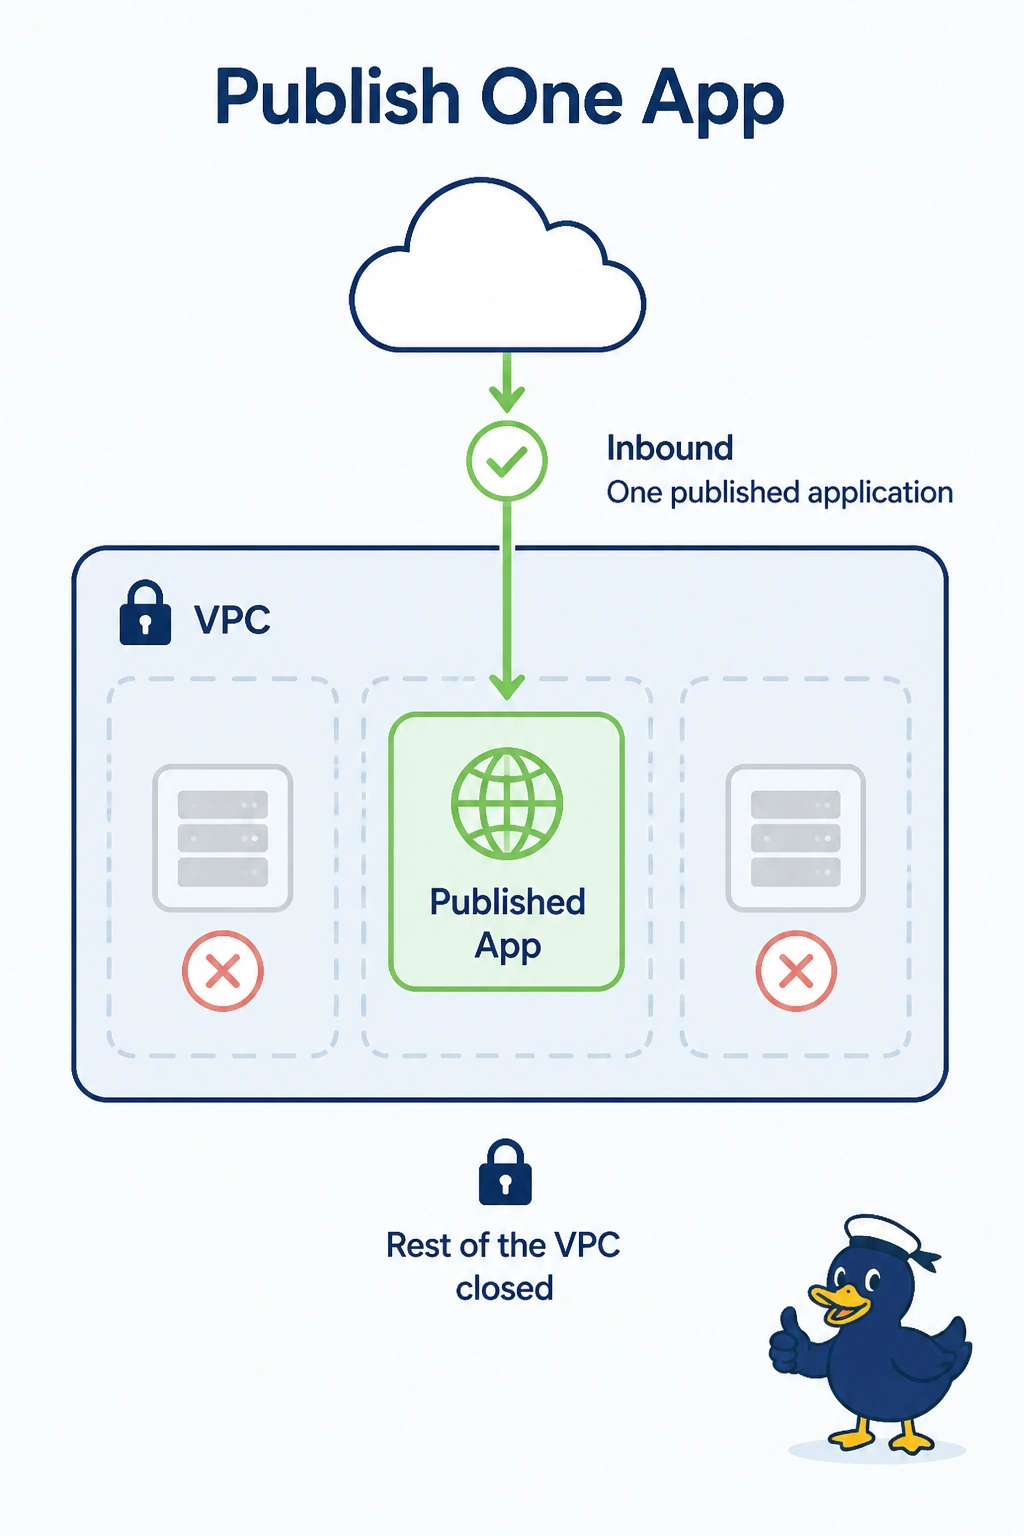
The partner needs one window, not a key to the building. You publish that application and leave the rest of the VPC closed. A full site-to-site VPN hands the partner a route to everything the proposal said they must not reach.
Full Explanation
Inbound publication exposes the one application, through a public endpoint or an inbound rule that stops at that application. A full site-to-site VPN routes the partner into the VPC and fails the limit. An east-west deny between subnets the partner never touches does not publish the application and does not describe the partner's path. A longer IKE lifetime on the campus VPN does not create an inbound publish. Exam caveat: lock the return path to the same public endpoint. If the reply is forced back through the campus, the partner session breaks even though the inbound rule is right. Operational check: the partner should reach only the published address, and a probe to another VPC address from the partner should fail.