
A campus must keep independent native VPNs to AWS and to Azure. Prefixes on each side change often. What fits?
Select an answer to reveal the explanation.
Short Explanation
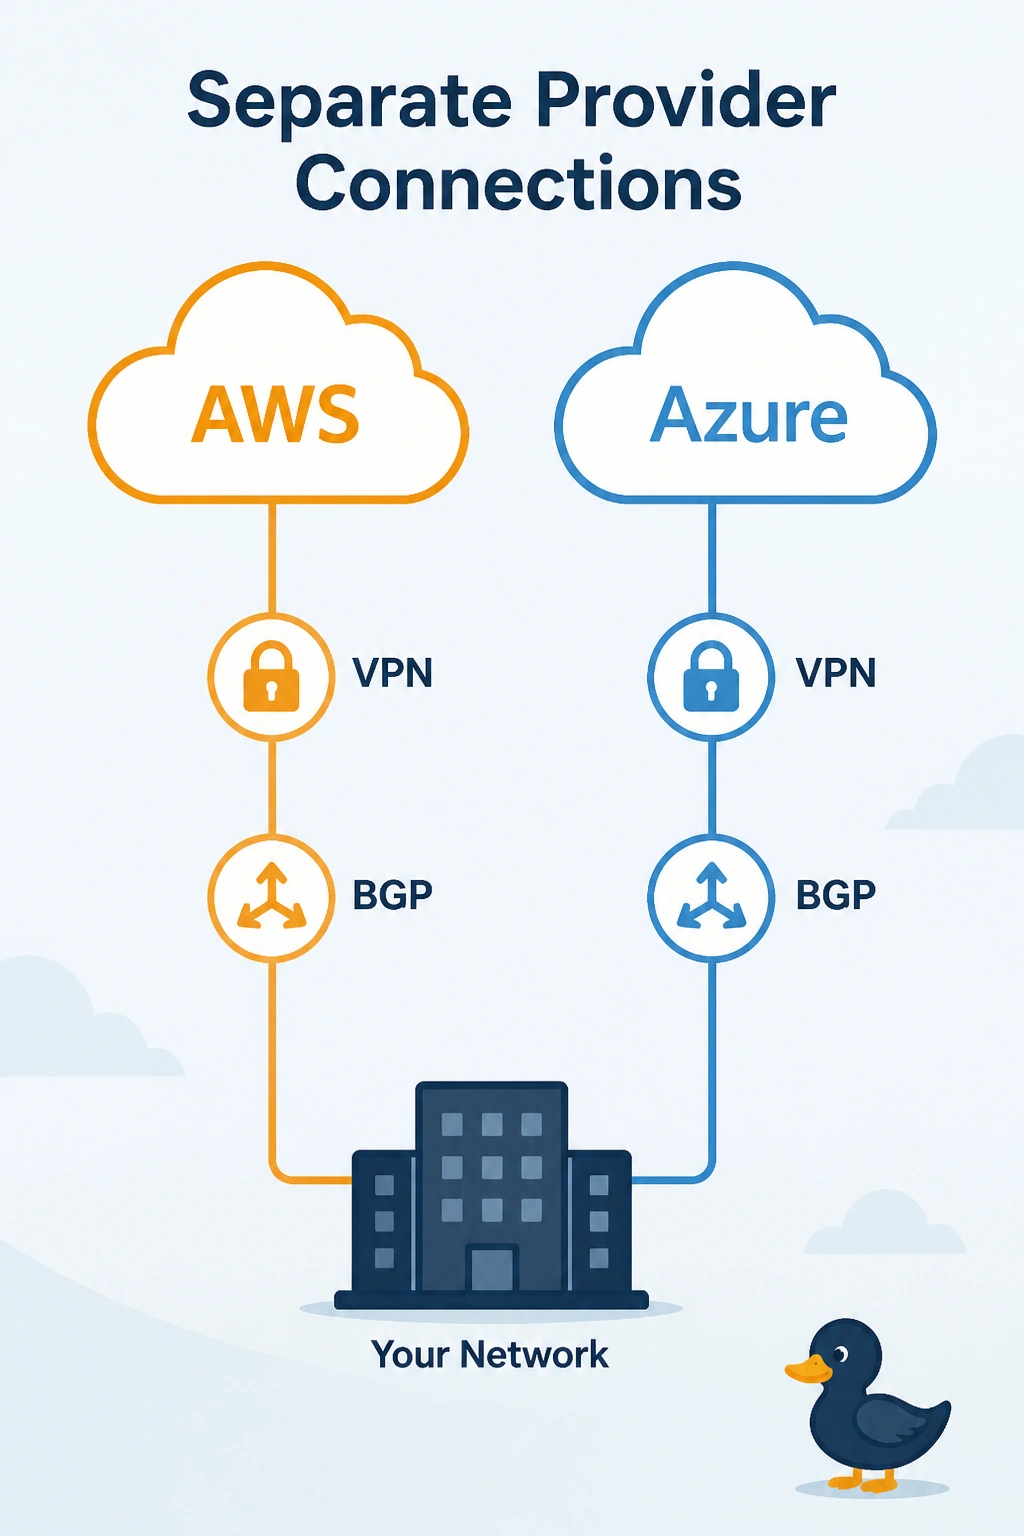
Two providers are two front doors, and one tunnel cannot knock on both. You build a separate VPN and a BGP session to each, because the prefixes change often. A single static default will not track those changes on both sides.
Full Explanation
AWS and Azure each have their own VPN endpoint. Independent native VPNs mean one connection and one BGP session per provider, so a failure or a prefix change on one side does not depend on the other. One IPsec tunnel cannot terminate on both gateways at once. Neither native gateway runs OSPF with the campus. A single static default cannot describe prefixes that change often on two providers. It also hides which provider a prefix belongs to. Exam caveat: each AWS connection still has its own pair of tunnels. A BGP session per provider is the routing fit. It does not replace those tunnels. Operational check: show ip bgp summary should list one neighbor for AWS and one for Azure, and shutting the AWS neighbor should leave the Azure prefixes installed.