
A clinic has one Google Cloud HA VPN gateway. BGP is up on only one of the two interfaces. That tunnel fails and the VPC prefix disappears. What should also be up?
Select an answer to reveal the explanation.
Short Explanation
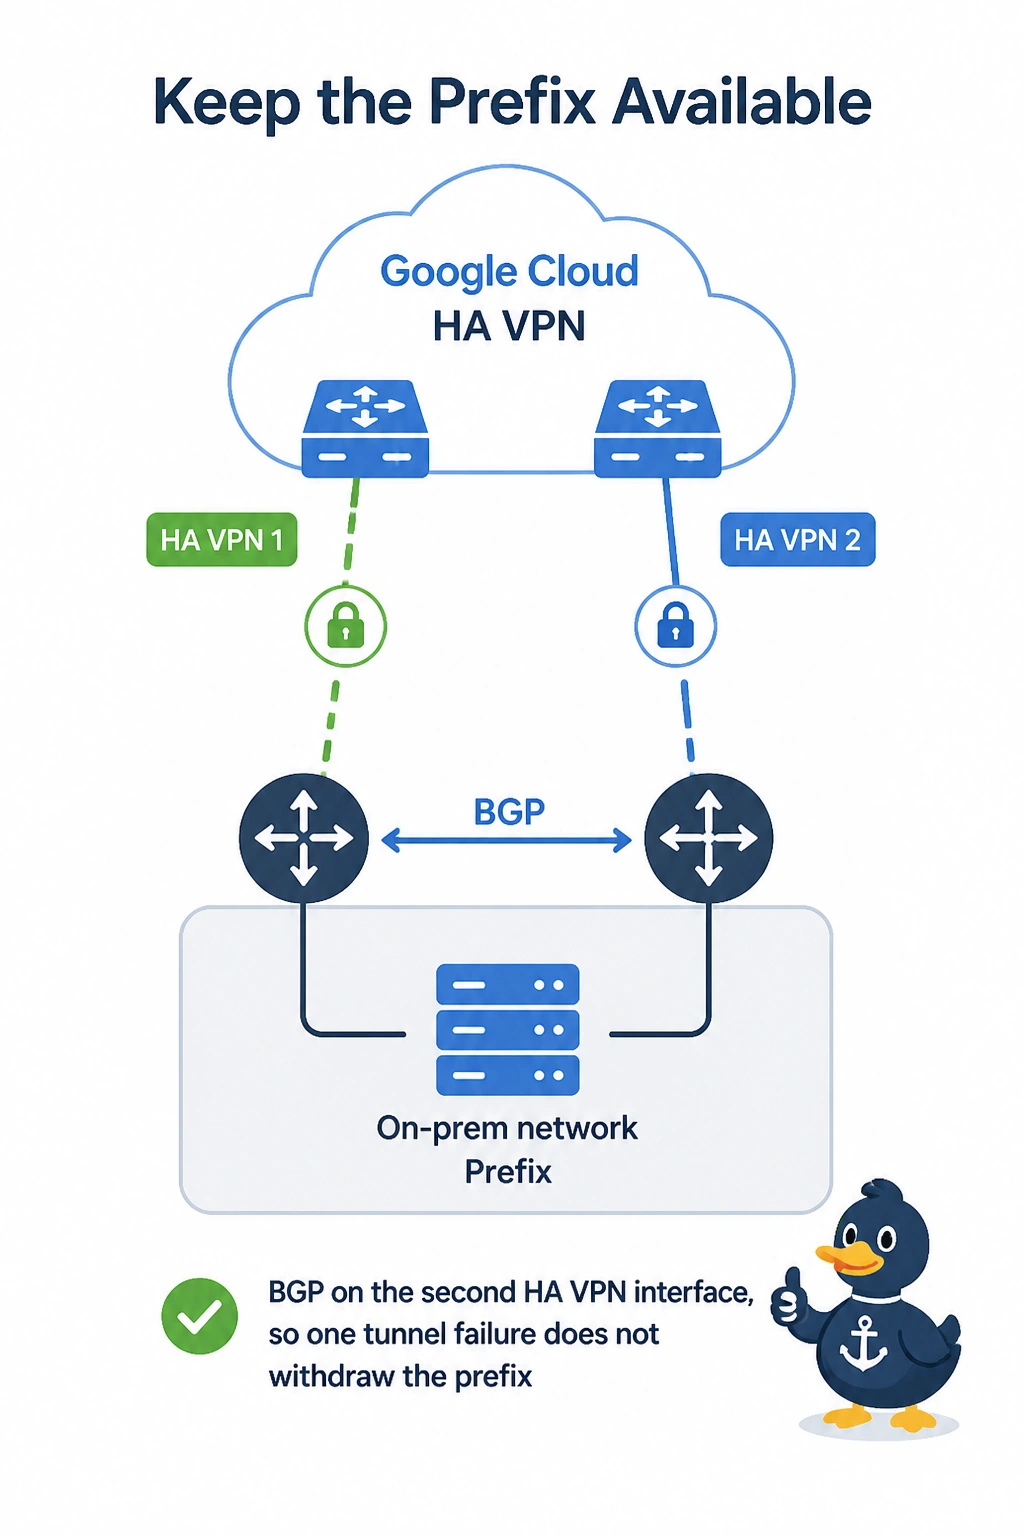
One of the two doors was never given a routing session, so a single failure took the prefix with it. You bring up BGP on the second HA VPN interface. A static route on the dead interface does not keep that prefix available.
Full Explanation
HA VPN keeps a VPC prefix available through a tunnel failure only when Cloud Router has a BGP session on the surviving interface as well. This clinic built the gateway and left the second interface with no BGP, so the only session dies with the first tunnel and the prefix is withdrawn. Add the tunnel and the BGP session on the second interface. A static route on the failed interface cannot stay up, and it is not how HA VPN is supposed to advertise into Cloud Router. OSPF is not the protocol Cloud Router uses with HA VPN. A longer IKE lifetime does not keep a withdrawn BGP prefix installed after the only session is gone. Exam caveat: both sessions need the VPC prefixes and a return path. A second session that advertises nothing still leaves the clinic with an empty table when the first one drops. Operational check: Cloud Router should show two BGP sessions, and shutting one tunnel should leave the VPC prefix installed through the other.