
A bank must encrypt the Direct Connect link itself with MACsec. A hosted connection is what they have today. Which change fits that requirement?
Select an answer to reveal the explanation.
Short Explanation
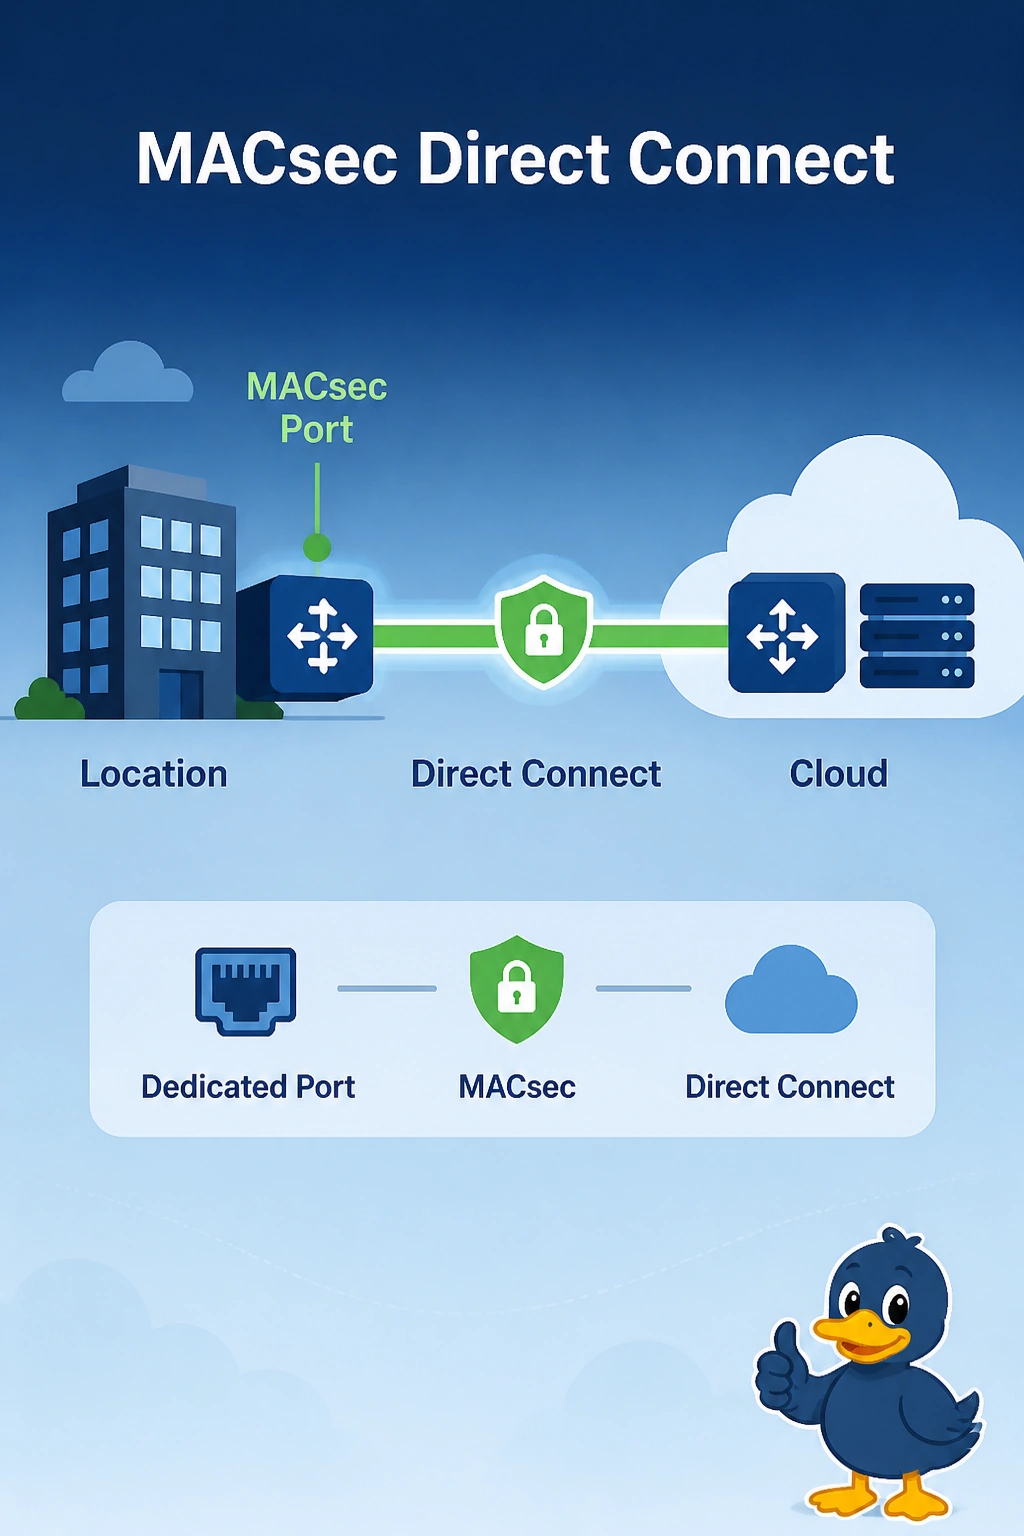
You need encryption on the Direct Connect link itself, and a hosted slice is not the port that provides it. Choose a dedicated port at a location that offers MACsec; availability is not guaranteed at every location or on every port. A hosted connection does not include MACsec just because you need it.
Full Explanation
MACsec protects the Direct Connect link itself. AWS offers it on dedicated connections at certain locations, not as a feature of every hosted partner connection, and not on every dedicated port. Since you have a hosted connection, the fit is a dedicated port at a location that offers MACsec; confirm availability before ordering. Any hosted connection does not gain MACsec merely because the requirement names it, so a hosted partner slice does not meet the link-encryption requirement. A longer IKE lifetime changes an IPsec timer; it does not create a MACsec session on the private port. A public virtual interface selects public service prefixes; MACsec is not configured only on public VLANs, so choosing one does not turn on link encryption. Exam caveat: if the desired location does not offer MACsec, IPsec over the private VIF is encryption you can add without treating the port as though it has link encryption. Practical check: verify that MACsec is available and up on the dedicated port, and that the hosted connection is no longer carrying the bank’s prefixes.