
A clinic advertises one campus prefix into an AWS VPN, and that prefix has not changed in years. There is no plan to add prefixes. Which routing is sufficient?
Select an answer to reveal the explanation.
Short Explanation
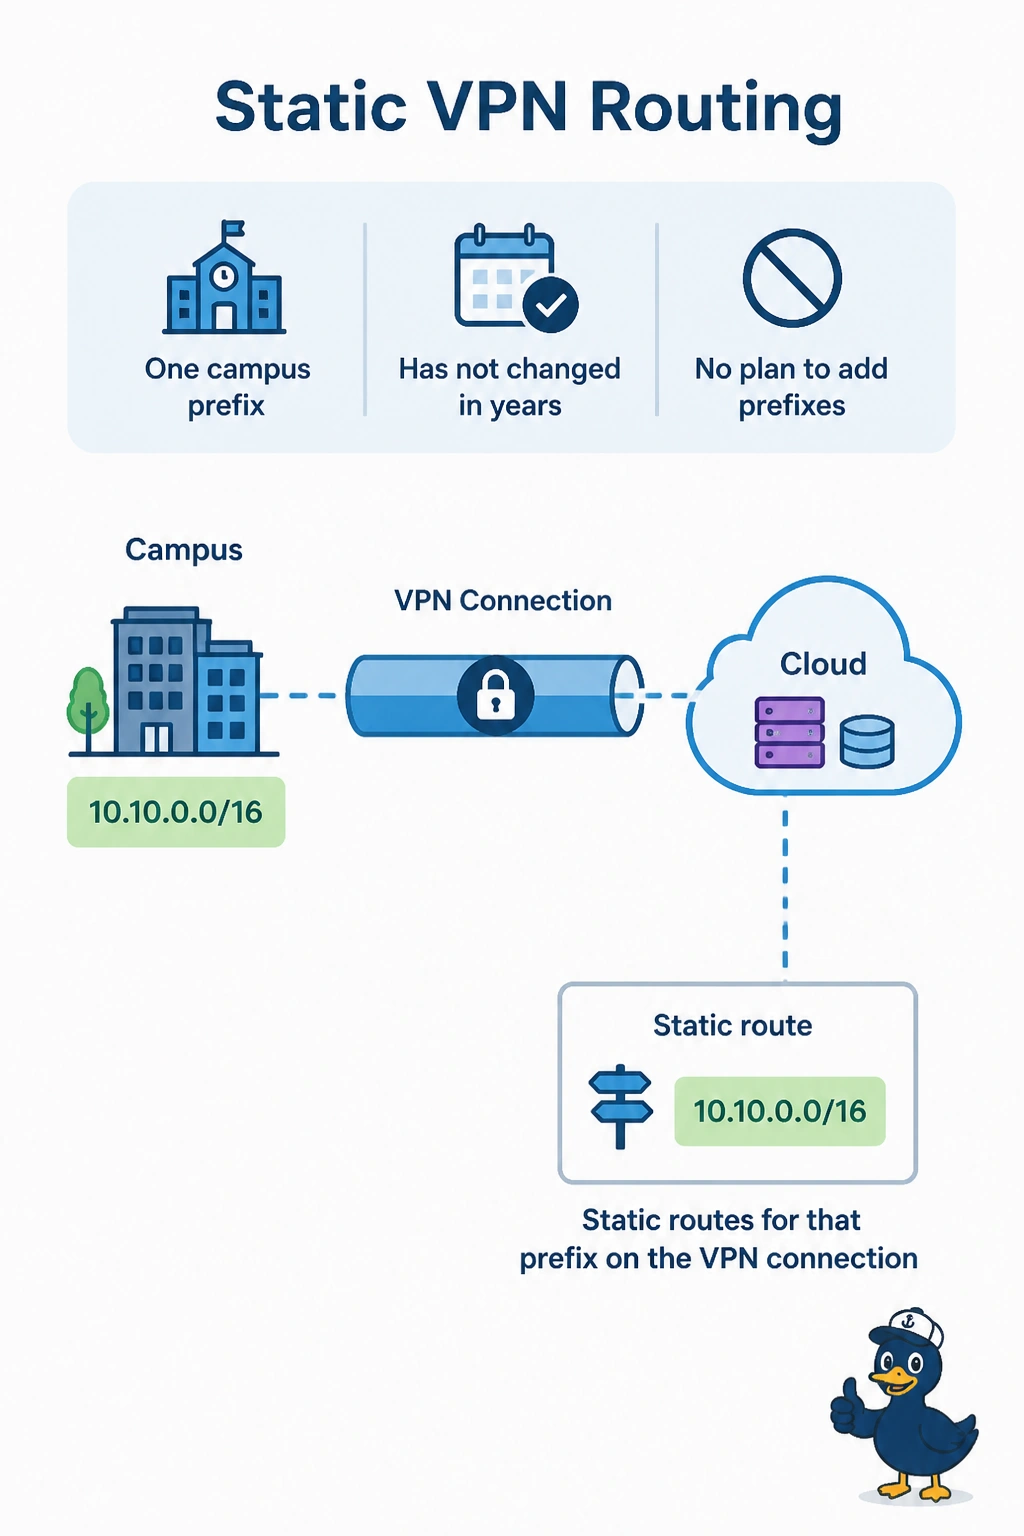
One prefix that never moves does not need a routing conversation. You put a static route for it on the VPN connection, and AWS can use that when BGP is not running. A stable prefix does not make the virtual private gateway start OSPF.
Full Explanation
AWS Site-to-Site VPN can learn the campus side from static routes configured on the connection, or from BGP. A single prefix that does not change is a fit for those static routes. BGP is available and is not mandatory for this case. AWS does not reject static routes on a connection that is set to use them. The virtual private gateway does not run OSPF, so a stable prefix cannot be a reason to demand it. The two tunnels of the connection are not an iBGP pair the customer configures between AWS devices, and static routes can be associated with the connection that has both tunnels. Exam caveat: the static route has to match the prefix the campus actually uses. A new subnet later will not appear until someone adds it, which is the trade for skipping BGP. Operational check: the VPN connection should list the campus prefix as a static route, and an instance in the VPC should reach a host in that prefix.