
A defense contractor's adopted NIST-based control says the regulated dataset must not traverse the public internet. The workload already sits in the approved cloud environment. Which connectivity recommendation fits?
Select an answer to reveal the explanation.
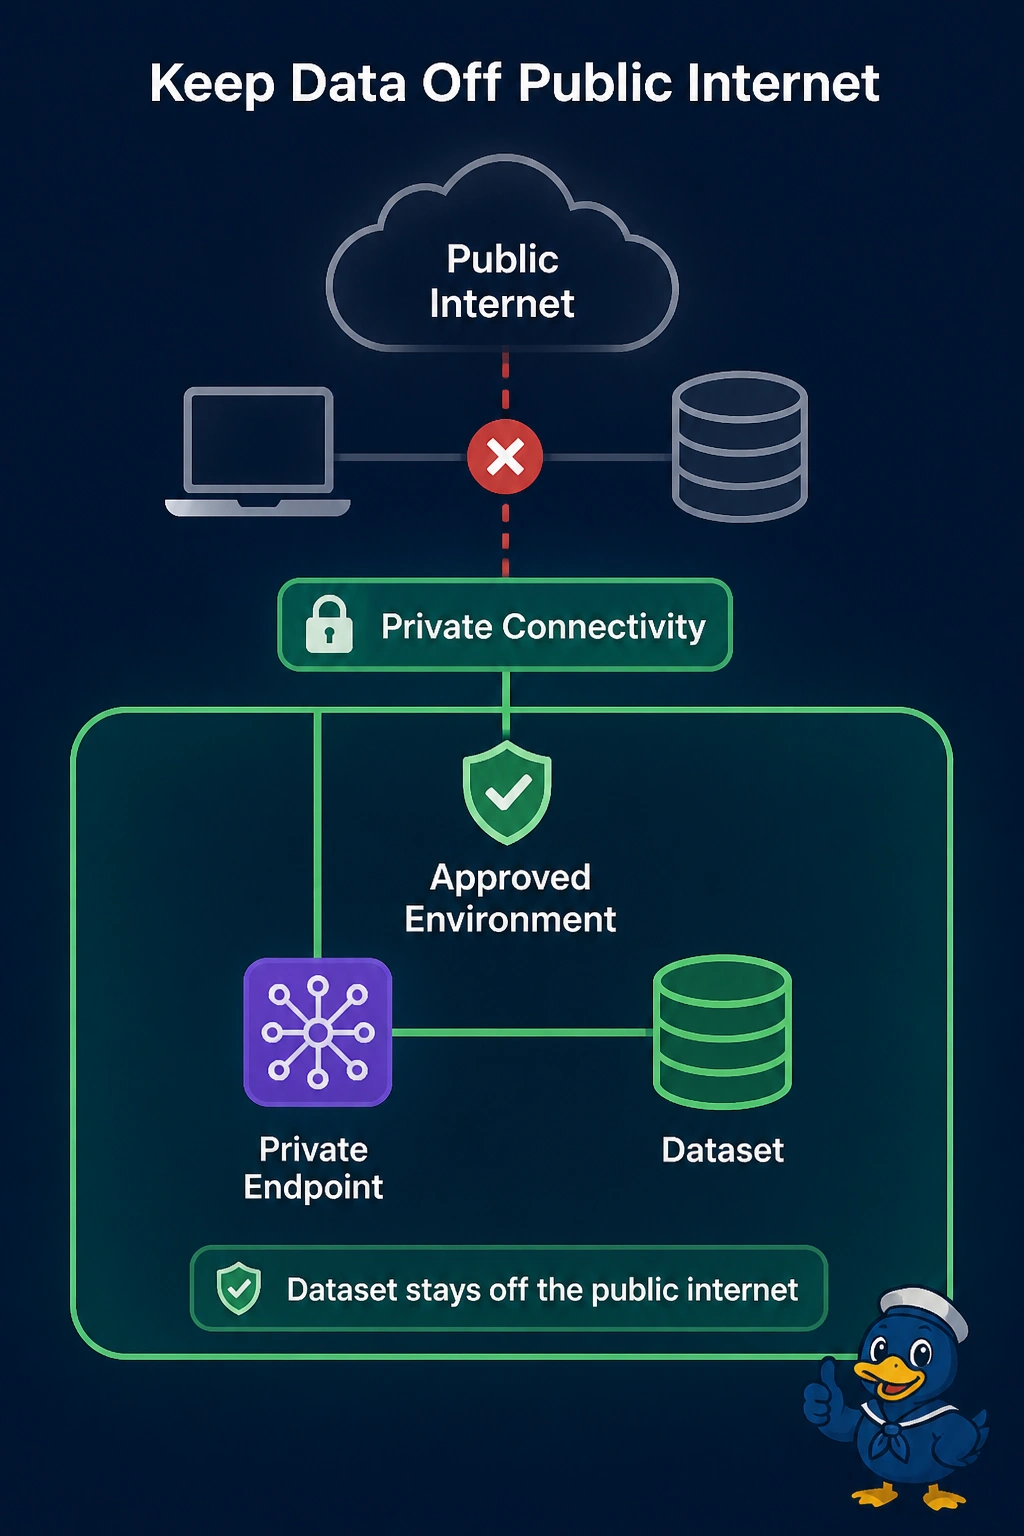
Short Explanation
A bigger lock on a public road still leaves the dataset on that road. You recommend private connectivity into the environment they already approved, because the control they adopted forbids the public internet. A larger key and a tidy log do not change the underlay, and this is a design fit rather than a legal opinion.
Full Explanation
The workload is already in the approved environment. The open constraint is the path. A NIST-based control the contractor adopted says the dataset must not traverse the public internet, so the matching recommendation is private connectivity into that environment. Internet IPsec with a larger key still crosses the public internet. Key length is not the control they stated. Direct internet access puts the dataset on the public internet and a local log only records that fact. A centralized internet gateway is still a public exit. One public door is not a private path. Exam caveat: choosing the private circuit does not by itself satisfy NIST. It satisfies the path constraint in the question. The system authorization is a separate decision, and this item is not legal advice. Operational check: the dataset's route should use the private interconnect, and the internet firewall should show no session for that prefix.