
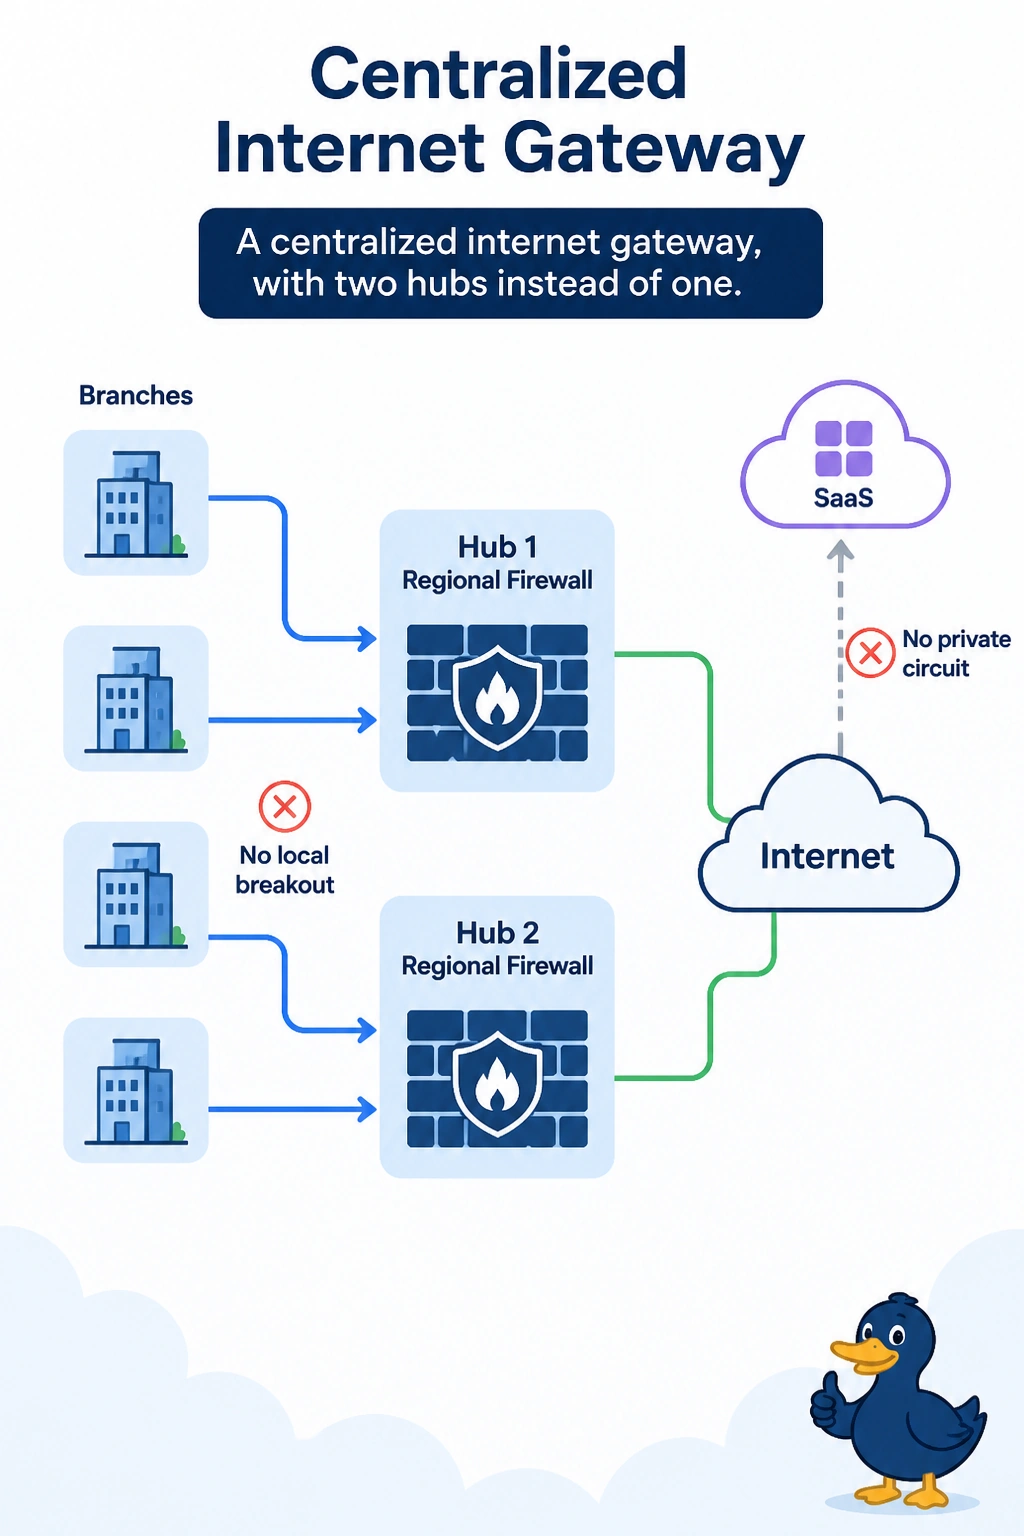
Every branch sends SaaS to one of two regional hub firewalls, and no branch breaks out locally. There is no private circuit to the SaaS provider. Which model is this?
Select an answer to reveal the explanation.
Short Explanation
Two regional hub firewalls are still a centralized internet gateway—you have two shared exits, not local breakout at each branch. Since no branch exits locally and there is no private provider circuit, this is neither direct internet access nor dedicated SaaS connectivity.
Full Explanation
A centralized internet gateway sends branch SaaS traffic to a shared internet exit before it reaches the provider. Here, each branch sends its traffic to one of two regional hub firewalls, so using two hubs rather than one headquarters firewall does not make the design local breakout. Direct internet access would mean a branch uses its own internet path to reach SaaS; the branches do not do that. Dedicated SaaS connectivity requires a private or peering path offered for reaching the SaaS provider, but the scenario specifies that there is no private circuit. An MPLS handoff into the SaaS provider’s private network would likewise be a private-path model, and no such handoff is described. The described model is therefore a centralized internet gateway with two hubs. Exam caveat: if a branch later gets its own inspected internet exit, that site’s traffic would use direct internet access, while the other branches could continue through the hubs. Practical check: trace a branch’s flow and confirm it reaches one of the two hub firewalls before the SaaS provider; the branch edge should not show a local internet session for that flow.