
Every branch is already a Catalyst SD-WAN edge. A new private VPC must be reached with the same centralized policy as the rest of the overlay, over the internet. Which attachment should they add?
Select an answer to reveal the explanation.
Short Explanation
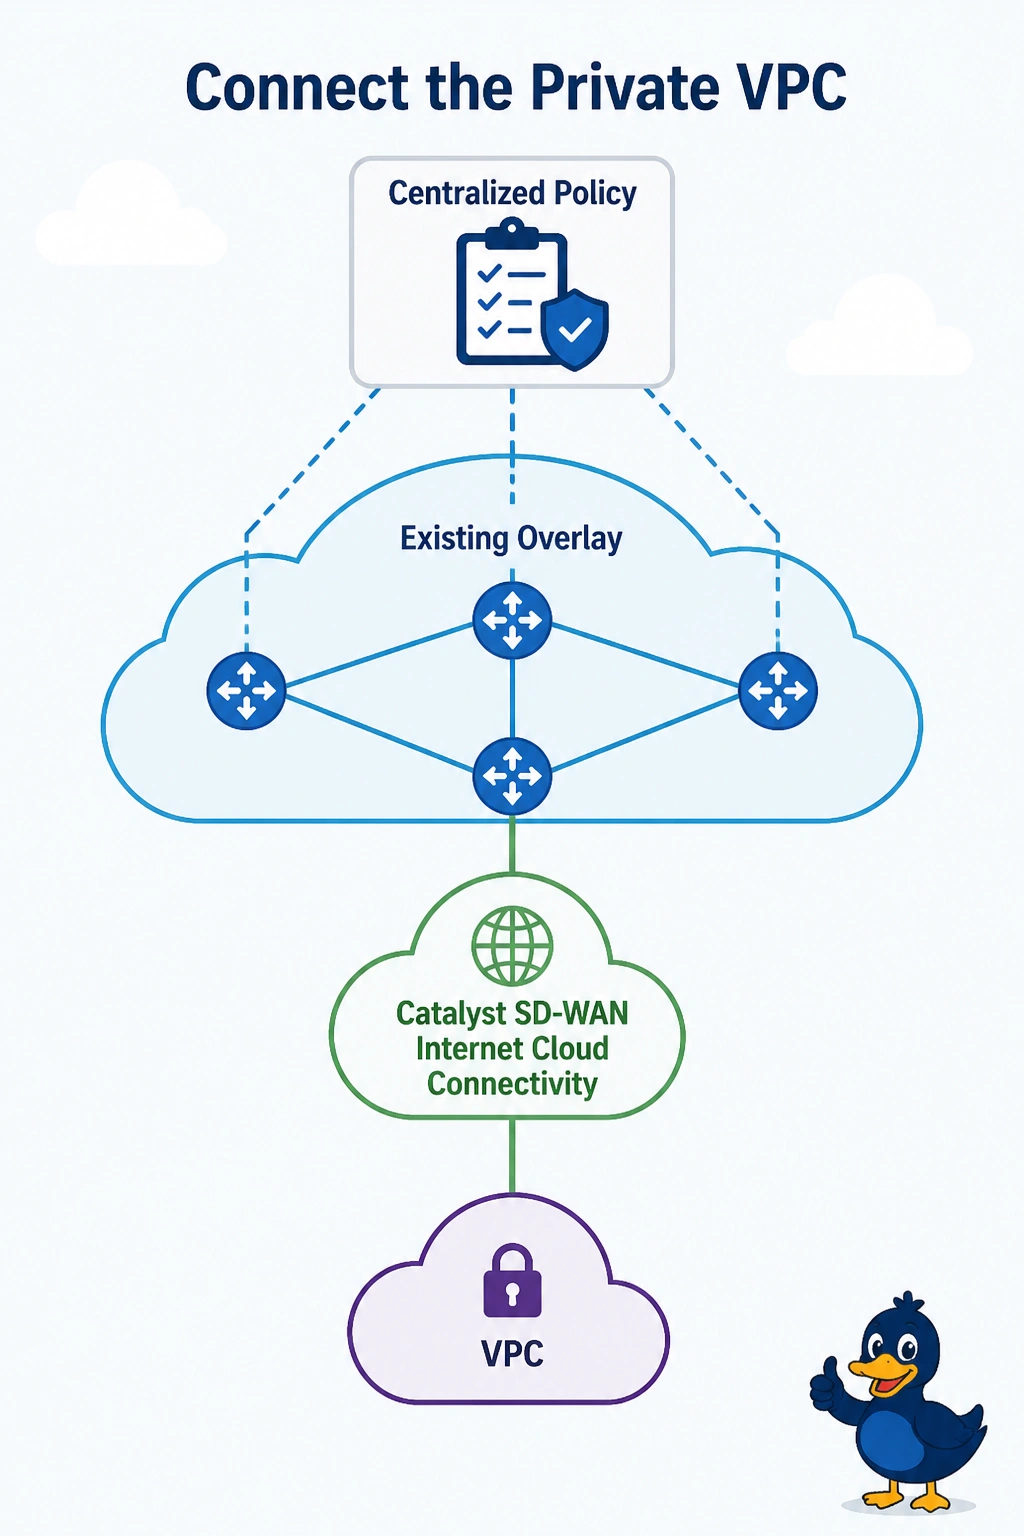
The branches are already in one overlay. You extend that overlay to the new VPC instead of building a second, unmanaged IPsec mesh beside it. Private addresses are not something a laptop can reach by walking onto the public internet.
Full Explanation
When the branches are already Catalyst SD-WAN edges and the new VPC must follow the same centralized policy, the attachment is SD-WAN internet cloud connectivity inside that overlay. Cloud OnRamp or the equivalent cloud gateway keeps the path in OMP. A standalone native IPsec tunnel from each branch to a virtual private gateway would move packets and would sit outside the controllers and the policy the requirement names. A colocation cross-connect needs equipment in the interconnect building. The branches do not have that. Direct internet access from laptops cannot reach private VPC addresses. Those addresses are not on the public internet. Exam caveat: a branch that is not yet an SD-WAN edge cannot use this attachment until it joins the overlay. Do not describe a legacy router as if the centralized policy already covers it. Operational check: the new VPC prefix should appear as an OMP route via the cloud TLOC on a branch, under the same policy the other overlay routes use.