
A financial campus has open lobby ports, a strict core-as-root STP hierarchy, contractors plugging unmanaged switches, and a need to contain lateral traffic between departments. Which Layer 2 security control set best enforces this switched-access protection goal?
Select an answer to reveal the explanation.
Short Explanation
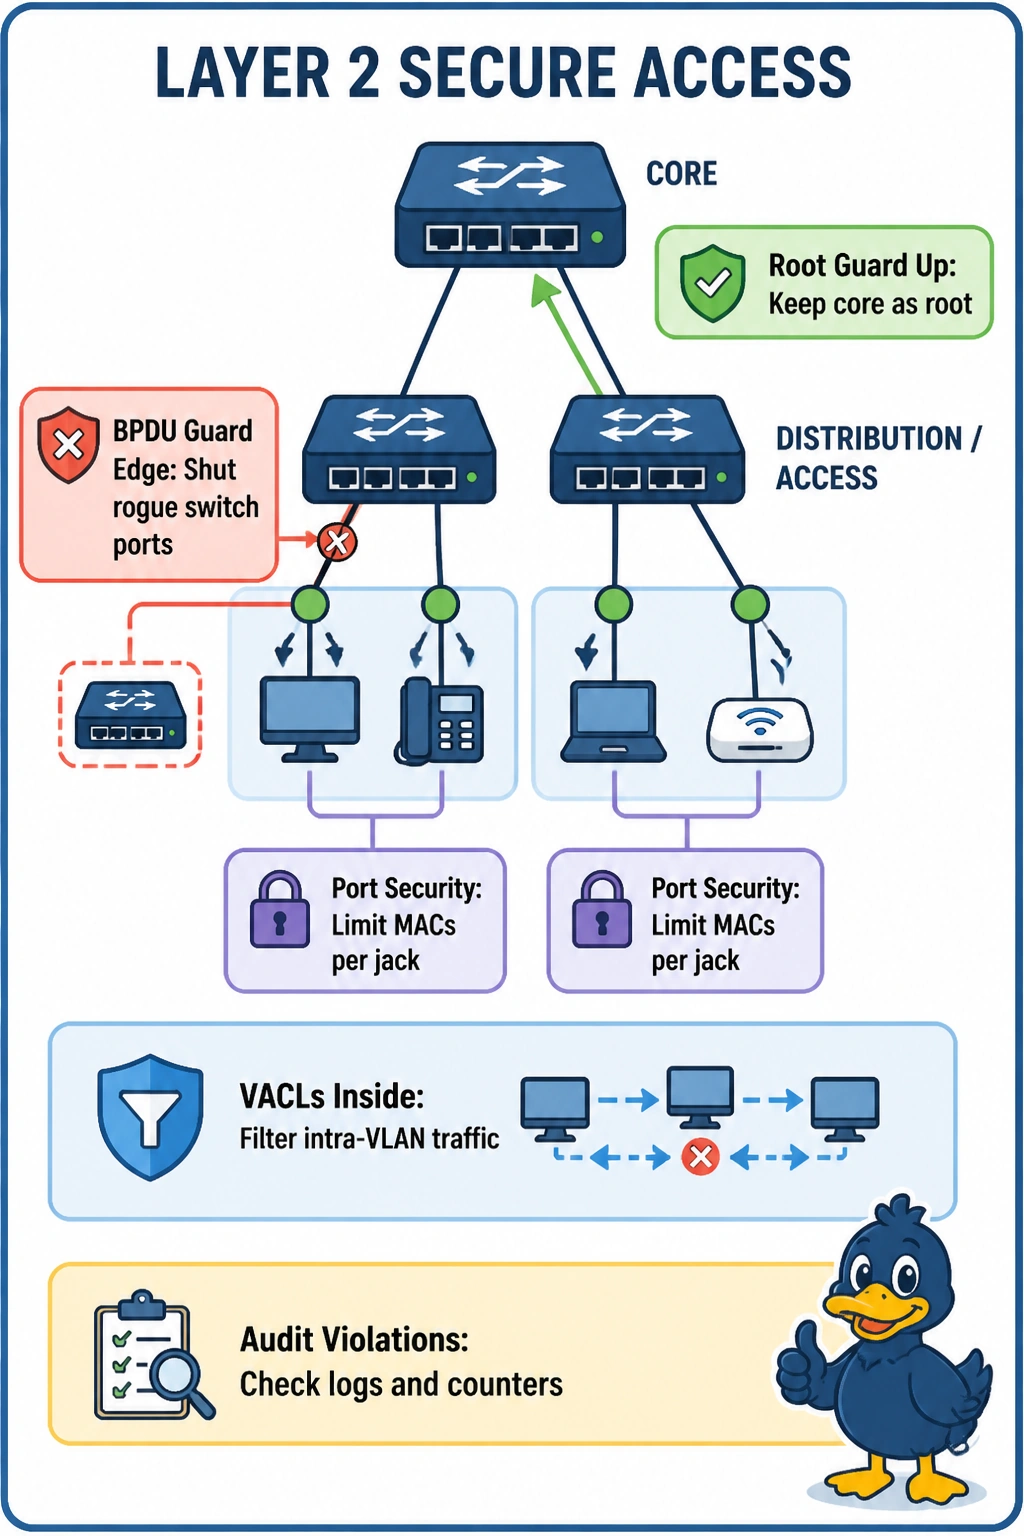
You're defending lobby jacks while keeping the core firmly in charge. Layered controls shut rogue BPDUs at the edge, lock root placement, and filter east-west right in the VLAN.
Full Explanation
The correct set maps each mechanism to a stated risk: BPDU guard on lobby access ports error-disables on any received BPDU to stop contractor unmanaged switches from influencing STP, root guard on the core and distribution ports that face downstream switches blocks superior BPDUs from below to preserve the strict core-as-root hierarchy (it is never enabled on a switch's own root port toward the core), port security limits MACs per open port to blunt flooding and hub expansion, and VACLs filter traffic inside the VLAN to contain department-to-department lateral movement that never hits a router. The RACL variant remains a sound north-south control but fails this goal conceptually because RACLs operate on SVIs and routed paths for inter-VLAN traffic, so same-VLAN lateral frames bypass them entirely where a VACL would inspect every frame. The UDLD aggressive variant is standard for detecting unidirectional fiber faults and keeps edge and lateral controls intact, but fails hierarchically because UDLD monitors hello loss on a link and has no concept of bridge priority, so it cannot prevent a downstream switch from winning root election. The BPDU filter variant is valid on carrier-managed handoffs to suppress STP chatter, but fails containment here because it silently discards BPDUs and leaves the rogue port forwarding, permitting loops and unauthorized extension where guard would place the port in errdisable for review. As an exam caveat, match STP tools to intent: guard stops rogue edge, root guard protects designated root placement, loop guard and UDLD handle different failures, and filter rarely satisfies an open-access threat. Practically confirm with show spanning-tree inconsistentports, show interfaces status errdisabled, show port-security, and an intra-VLAN test between departments to verify VACL denies and logs.