
A bank WAN Edge behind a branch firewall must build DTLS control to a cloud-hosted Controller and Validator, outbound HTTPS is open, but control never forms while data traffic works. Which firewall and NAT port requirement should the engineer verify to restore DTLS/TLS control connections?
Select an answer to reveal the explanation.
Short Explanation
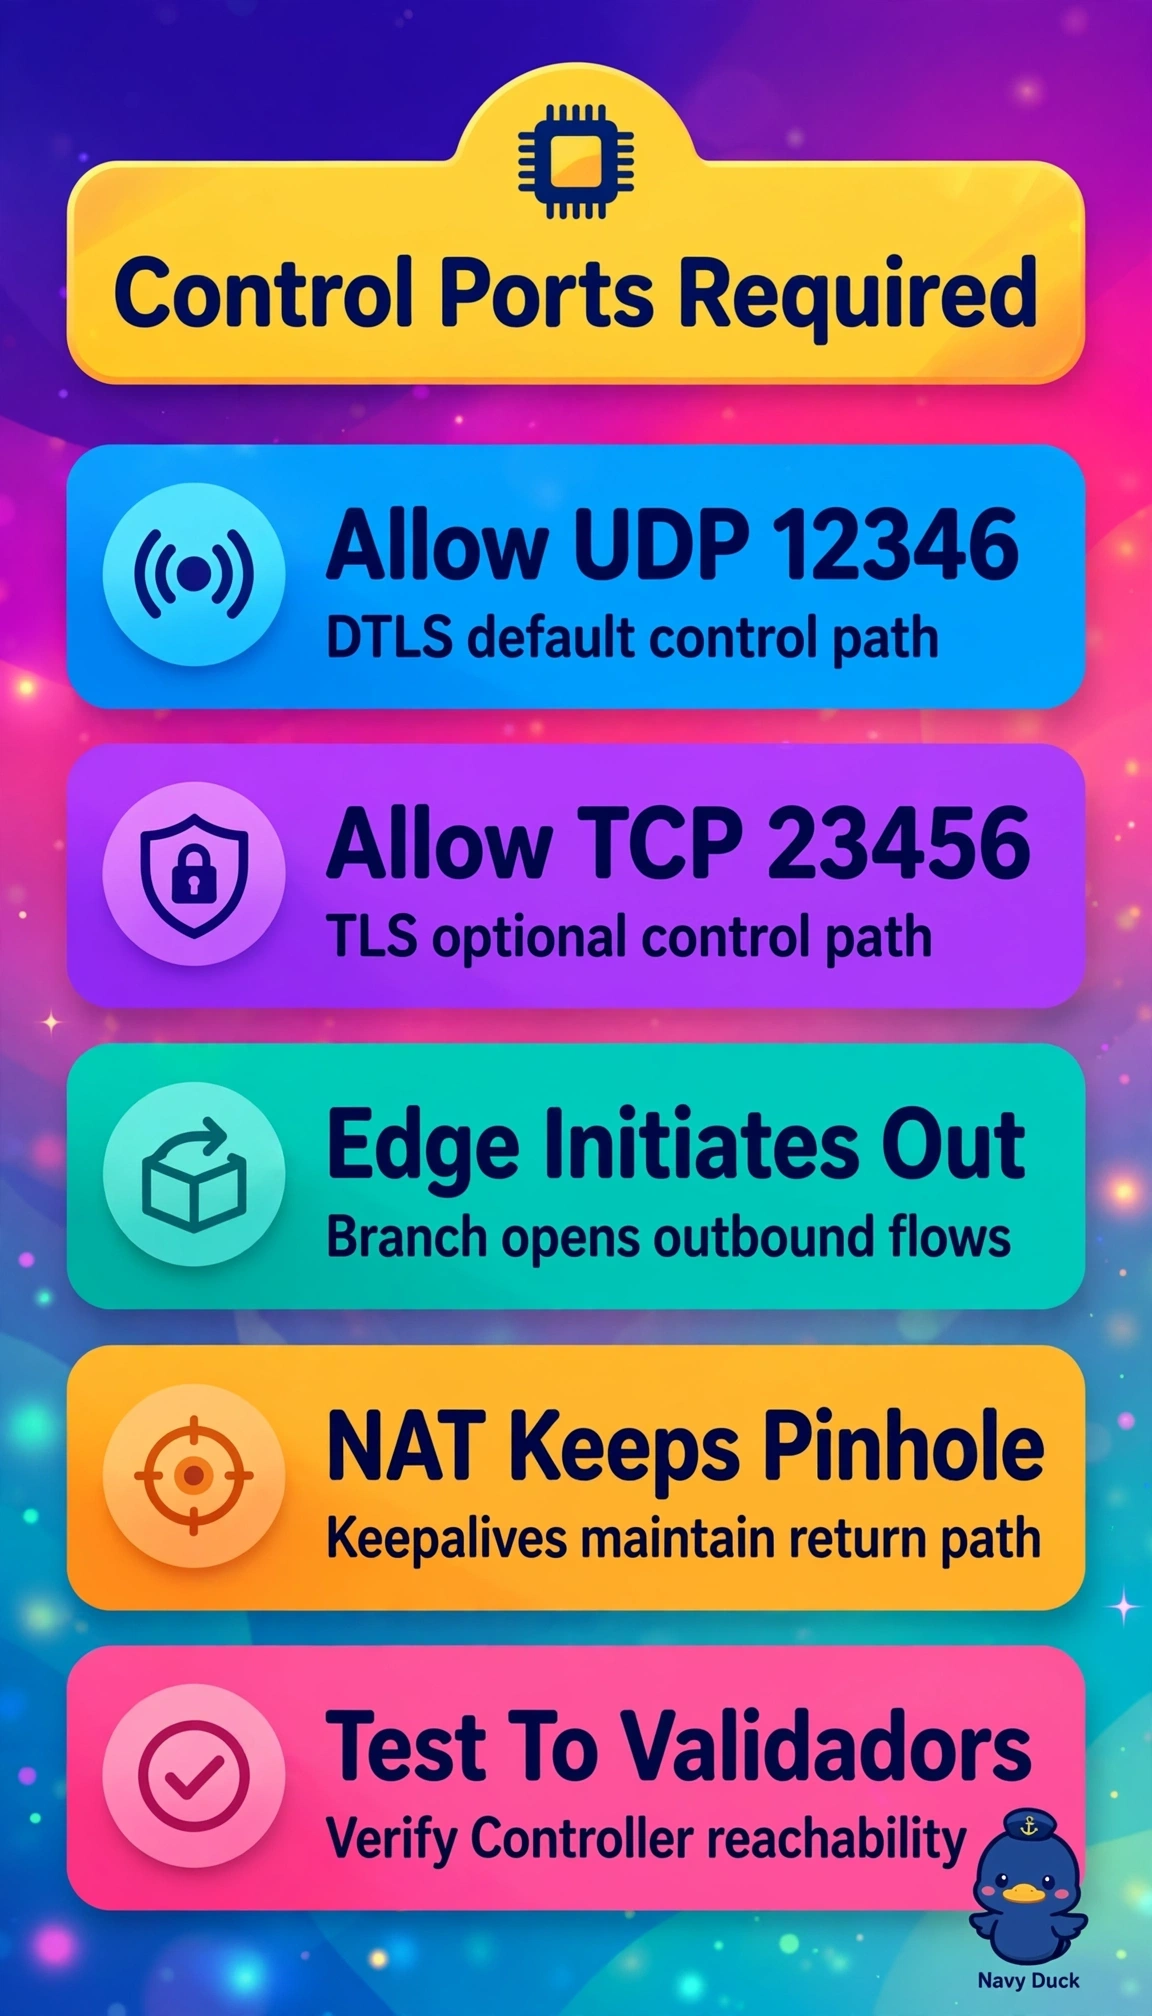
You're opening the right doors for the control handshake to slip through. Edges initiate DTLS outbound, so reachability on UDP 12346 (and TCP 23456 for TLS) is non-negotiable.
Full Explanation
The correct requirement reflects that the WAN Edge initiates control outbound to both Validator for orchestration and discovery and Controller for policy and routing, using DTLS over UDP 12346 by default with TLS over TCP 23456 as an optional alternative toward the Controller, so the branch firewall must permit those outbound sessions and NAT must preserve return traffic, which explains why open HTTPS alone leaves control down while data can still flow. Permitting only outbound TCP 443 fails conceptually because 443 supports management and certificate or web access but does not transport DTLS control messages, so HTTPS reachability does not prove control-plane reachability. Permitting only UDP 500 and 4500 for IKE and NAT-T fails conceptually because those ports sustain data-plane IPsec tunnels, which accounts for working data traffic, but they do not establish the control-plane DTLS or TLS sessions that must form before routes and policy are learned. Permitting the correct control ports to the Controller only fails conceptually because initial bring-up requires Validator reachability for authentication, orchestration and controller discovery, so omitting the Validator breaks formation even when controller ports are open. Exam caveat is to separate control, data and management planes by port and initiation direction and to remember cloud control is outbound-initiated with return NAT rather than an inbound pinhole to the Edge. Practical check is to review firewall accept and deny counters for outbound UDP 12346 and TCP 23456 toward Validator and Controller addresses, verify NAT translations and timeouts preserve the sessions, and capture the DTLS handshake while confirming Validator reachability before troubleshooting Controller adjacency.