
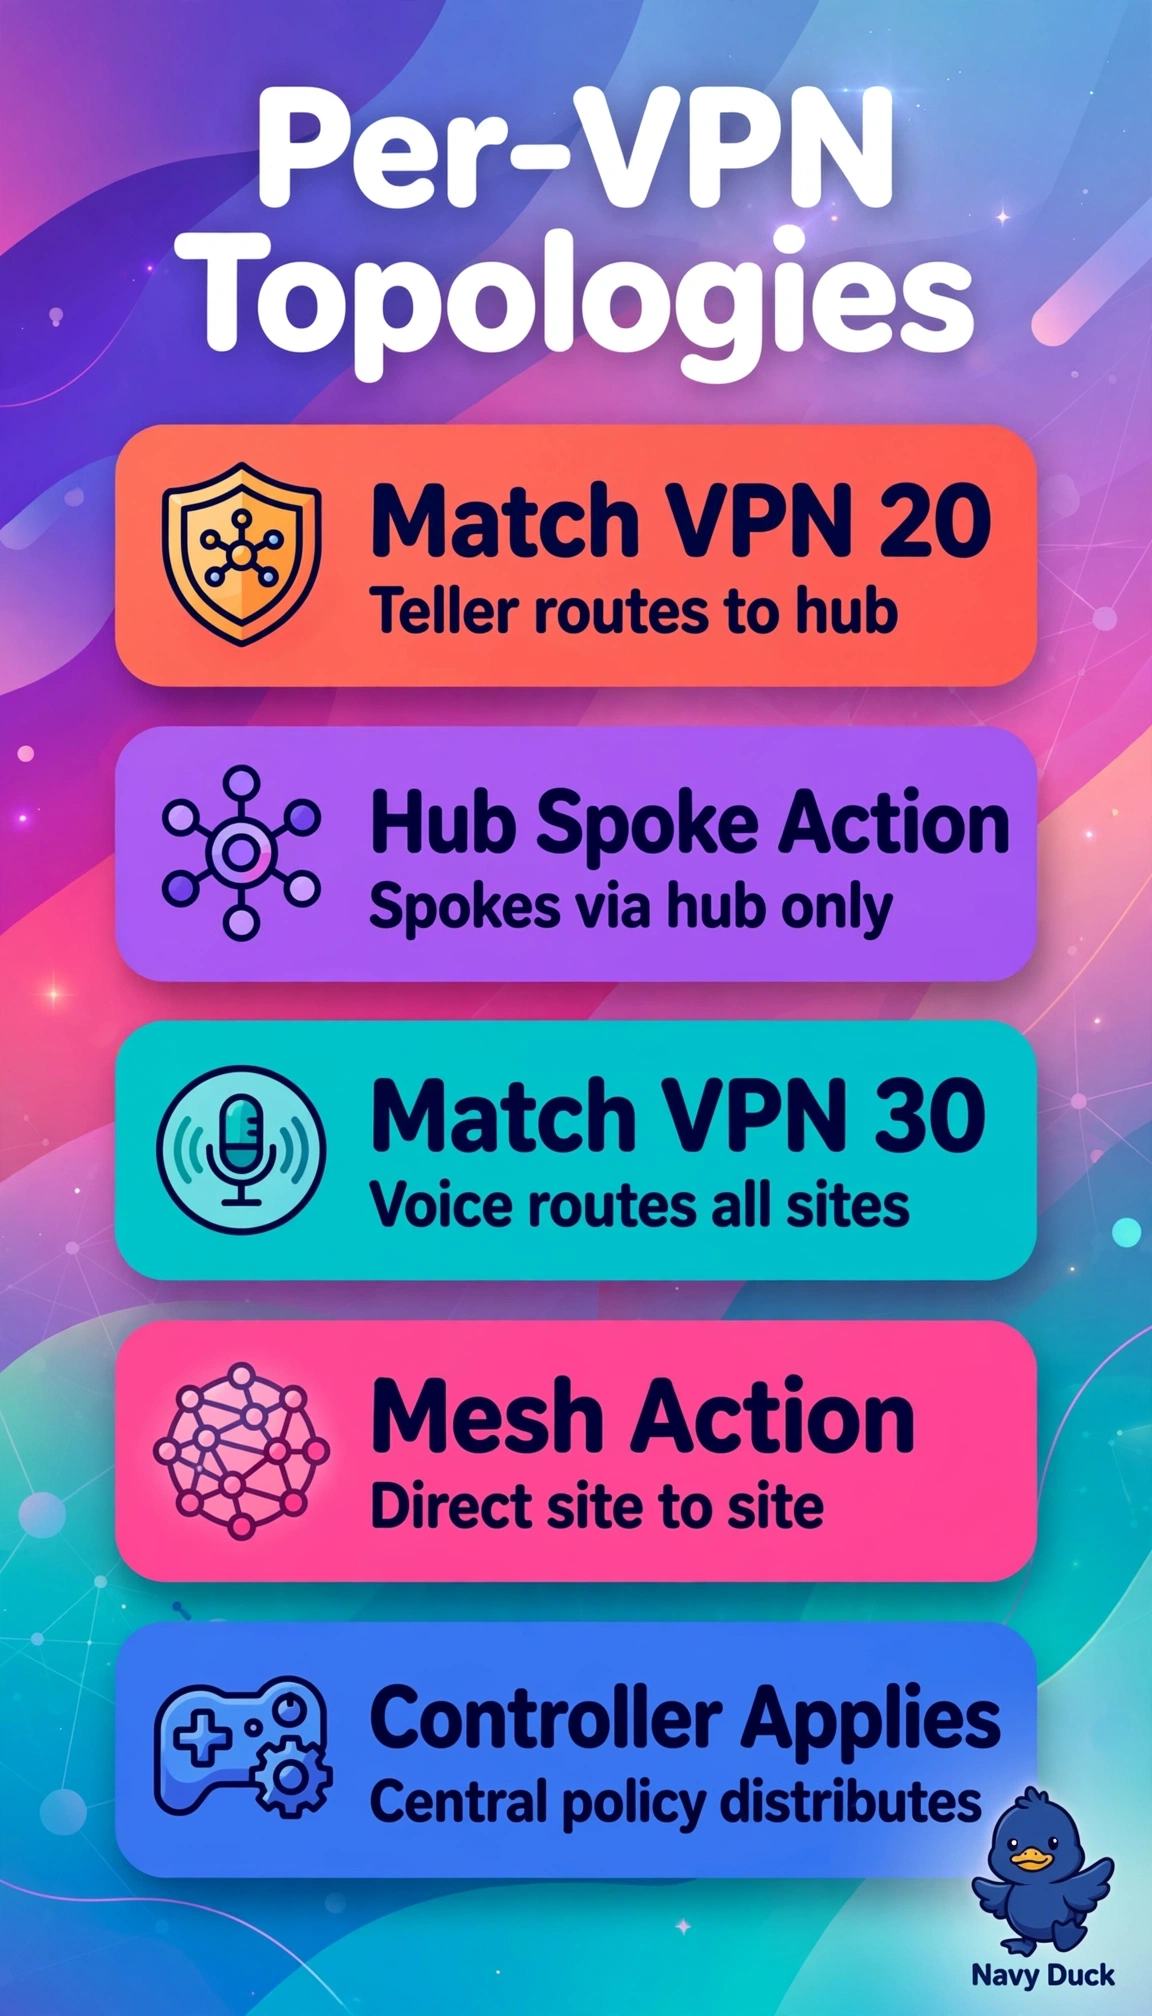
A bank needs VPN 20 for teller traffic restricted to hub-and-spoke through the data center and VPN 30 for voice engineers requiring full mesh between campuses, both running over the same SD-WAN fabric. The architect must enforce different topologies per VPN centrally. Which end-to-end segmentation approach with control policy meets this dual-topology requirement?
Select an answer to reveal the explanation.
Short Explanation
You need two VPNs behaving like totally different networks on one fabric, and that calls for precision. Control policy on the Controller lets you sculpt hub-and-spoke for one VPN and mesh for another.
Full Explanation
The correct approach is right because centralized control policy on the SD-WAN Controller (formerly vSmart) manipulates TLOC routes per VPN, so one policy can constrain VPN 20 advertisements to data-center TLOCs for hub-and-spoke while permitting full VPN 30 TLOC exchange for mesh, preserving segmentation and dual topologies over the same fabric. Forcing hub-and-spoke for both VPNs through the data center is a legitimate pattern for compliance and inspection but fails here by topology concept because VPN 30 voice then loses direct campus paths, adding latency and hub load contrary to the explicit full-mesh requirement. Using a centralized data policy with identical VPN 20 and VPN 30 intent is widely used for forwarding, path preference and QoS but fails by control-plane concept because data policy cannot create topology, only control policy governing OMP TLOC advertisement can enforce hub-and-spoke versus mesh. Using localized control policy on each router with correct per-VPN intent can achieve similar routes in a lab but fails by management concept because the scenario demands central enforcement for consistency, scale and auditability from SD-WAN Manager and the Controller. As an exam caveat, associate topology, TLOC, site list and hub-and-spoke versus mesh with control policy and associate application routing, QoS and forwarding with data policy. As a practical check, push the policy centrally then verify VPN 20 branches learn only hub TLOCs and VPN 30 branches learn all campus TLOCs with show sdwan omp tlocs and traffic tests.