
A healthcare network with 120 WAN Edge routers must forward critical SD-WAN alarms to a central syslog server and SNMP manager, with email alerts for severity-critical events and no flood of minor alarms. Operators use SD-WAN Manager for visibility. Which alarm and notification configuration meets the forwarding requirement?
Select an answer to reveal the explanation.
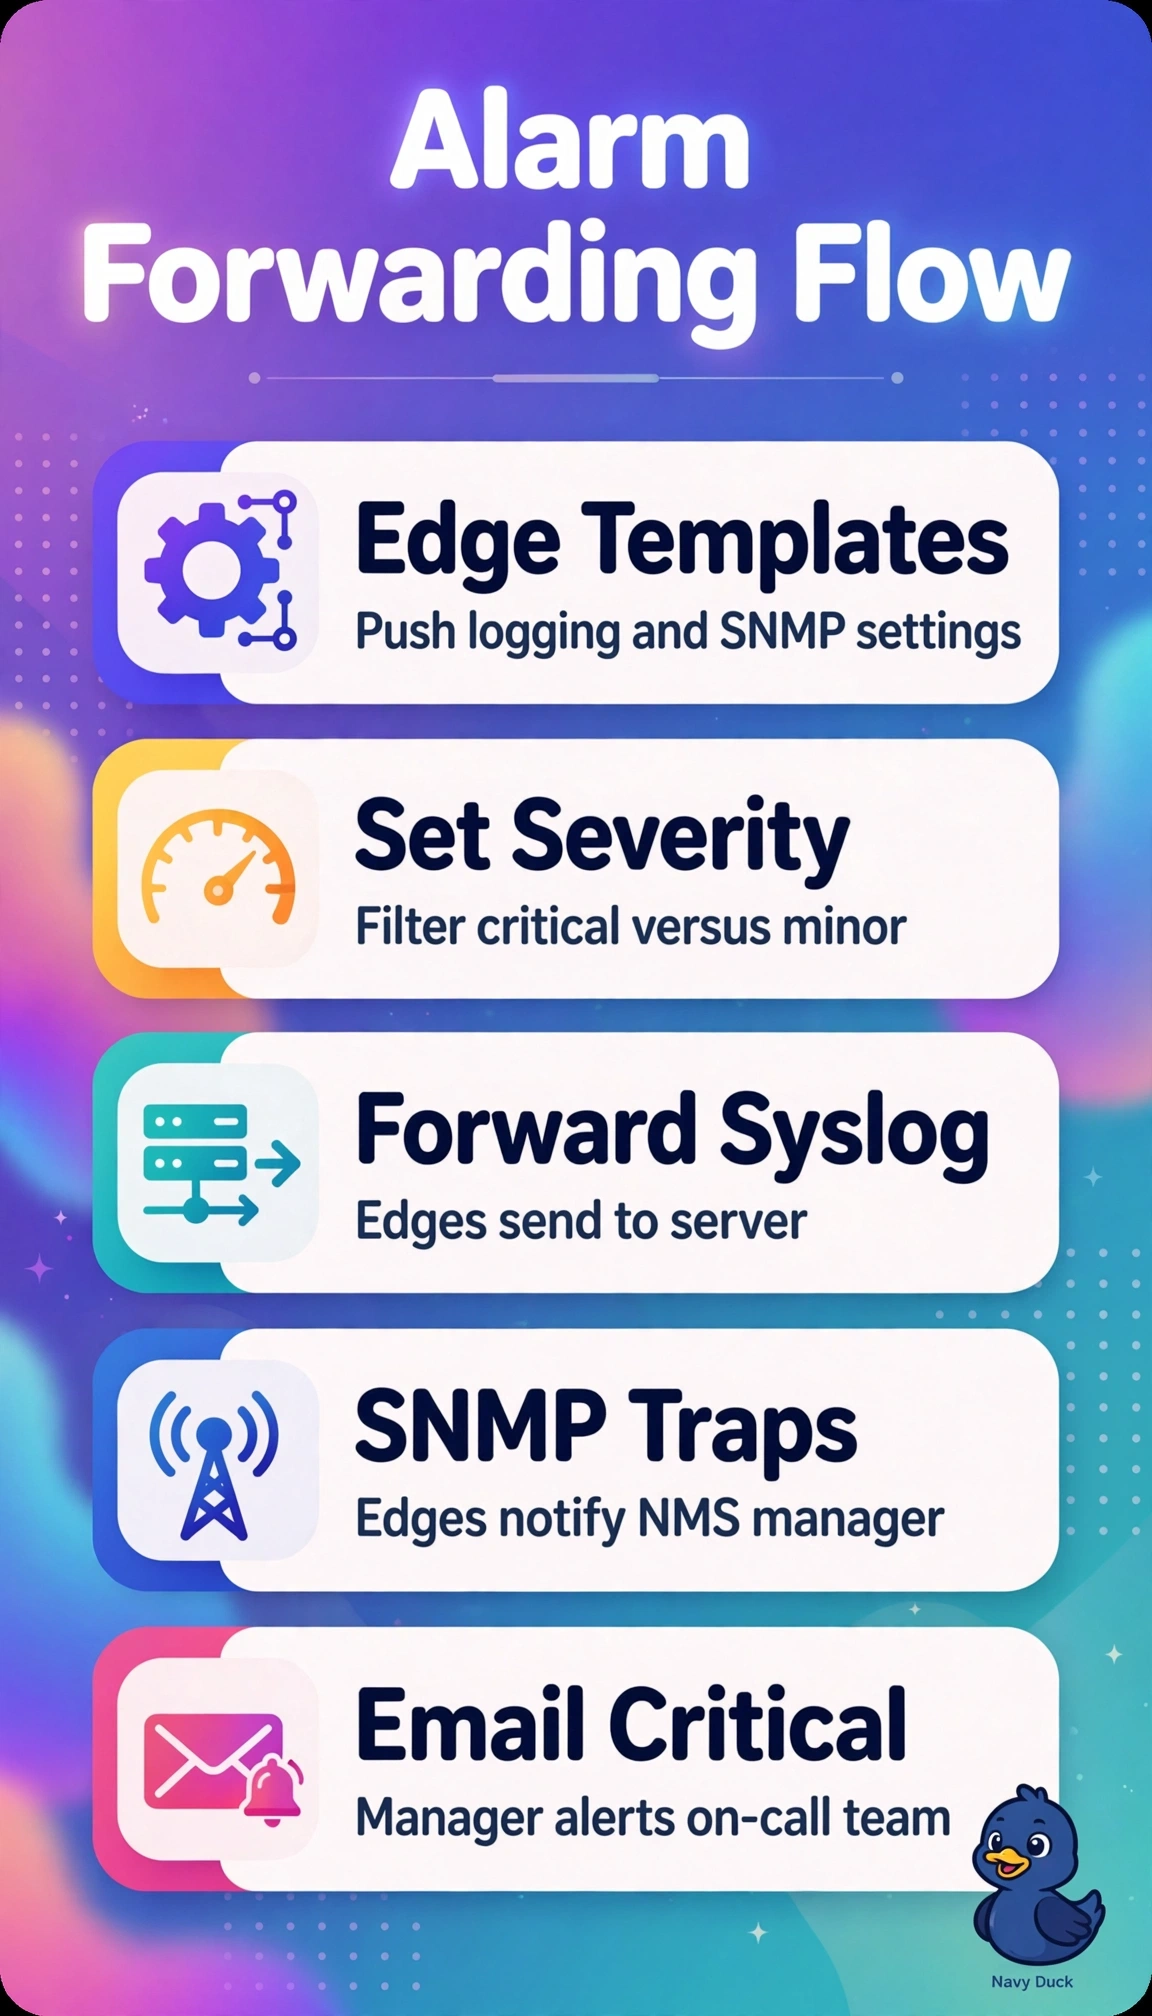
Short Explanation
You need a smart pager, not a firehose of beeps from every device. Severity filtering at the Edge templates and in Manager email keeps only critical events flowing. Set the threshold once and your on-call nights get quieter.
Full Explanation
The correct configuration splits the job by where each notification originates: WAN Edge routers generate syslog messages and SNMP traps themselves, so the Logging and SNMP settings (server, trap target, minimum severity) are pushed once to all 120 Edges through device templates, while SD-WAN Manager alarm notifications provide severity-filtered email for critical alarms. The alternative that emails every severity and forwards everything fails on filtering, since unfiltered events meet the destinations but violate the no-flood constraint and desensitize responders. The alternative that forwards matching events from Manager to syslog and keeps SNMP polling fails on mechanism, since Manager alarm notifications deliver by email or webhook rather than to a syslog server, and polling retrieves state on a schedule instead of pushing asynchronous traps for urgent faults. The alternative that relies on Manager email and webhooks alone fails on coverage, because without syslog and trap targets on the Edges the central syslog server and SNMP manager receive nothing. Exam caveat: distinguish device-generated syslog and traps, configured in templates, from Manager-generated email and webhook notifications. Practical check: trigger a critical test event and confirm it reaches the syslog server, the trap receiver, and email, with minor events absent.