
A new manufacturing fabric has Manager and Controllers online, but two WAN Edges behind NAT cannot find peers and show no DTLS sessions. Staging confirmed certificates and organization name are correct. Which Validator orchestration and NAT discovery behavior should the engineer verify to allow initial authentication?
Select an answer to reveal the explanation.
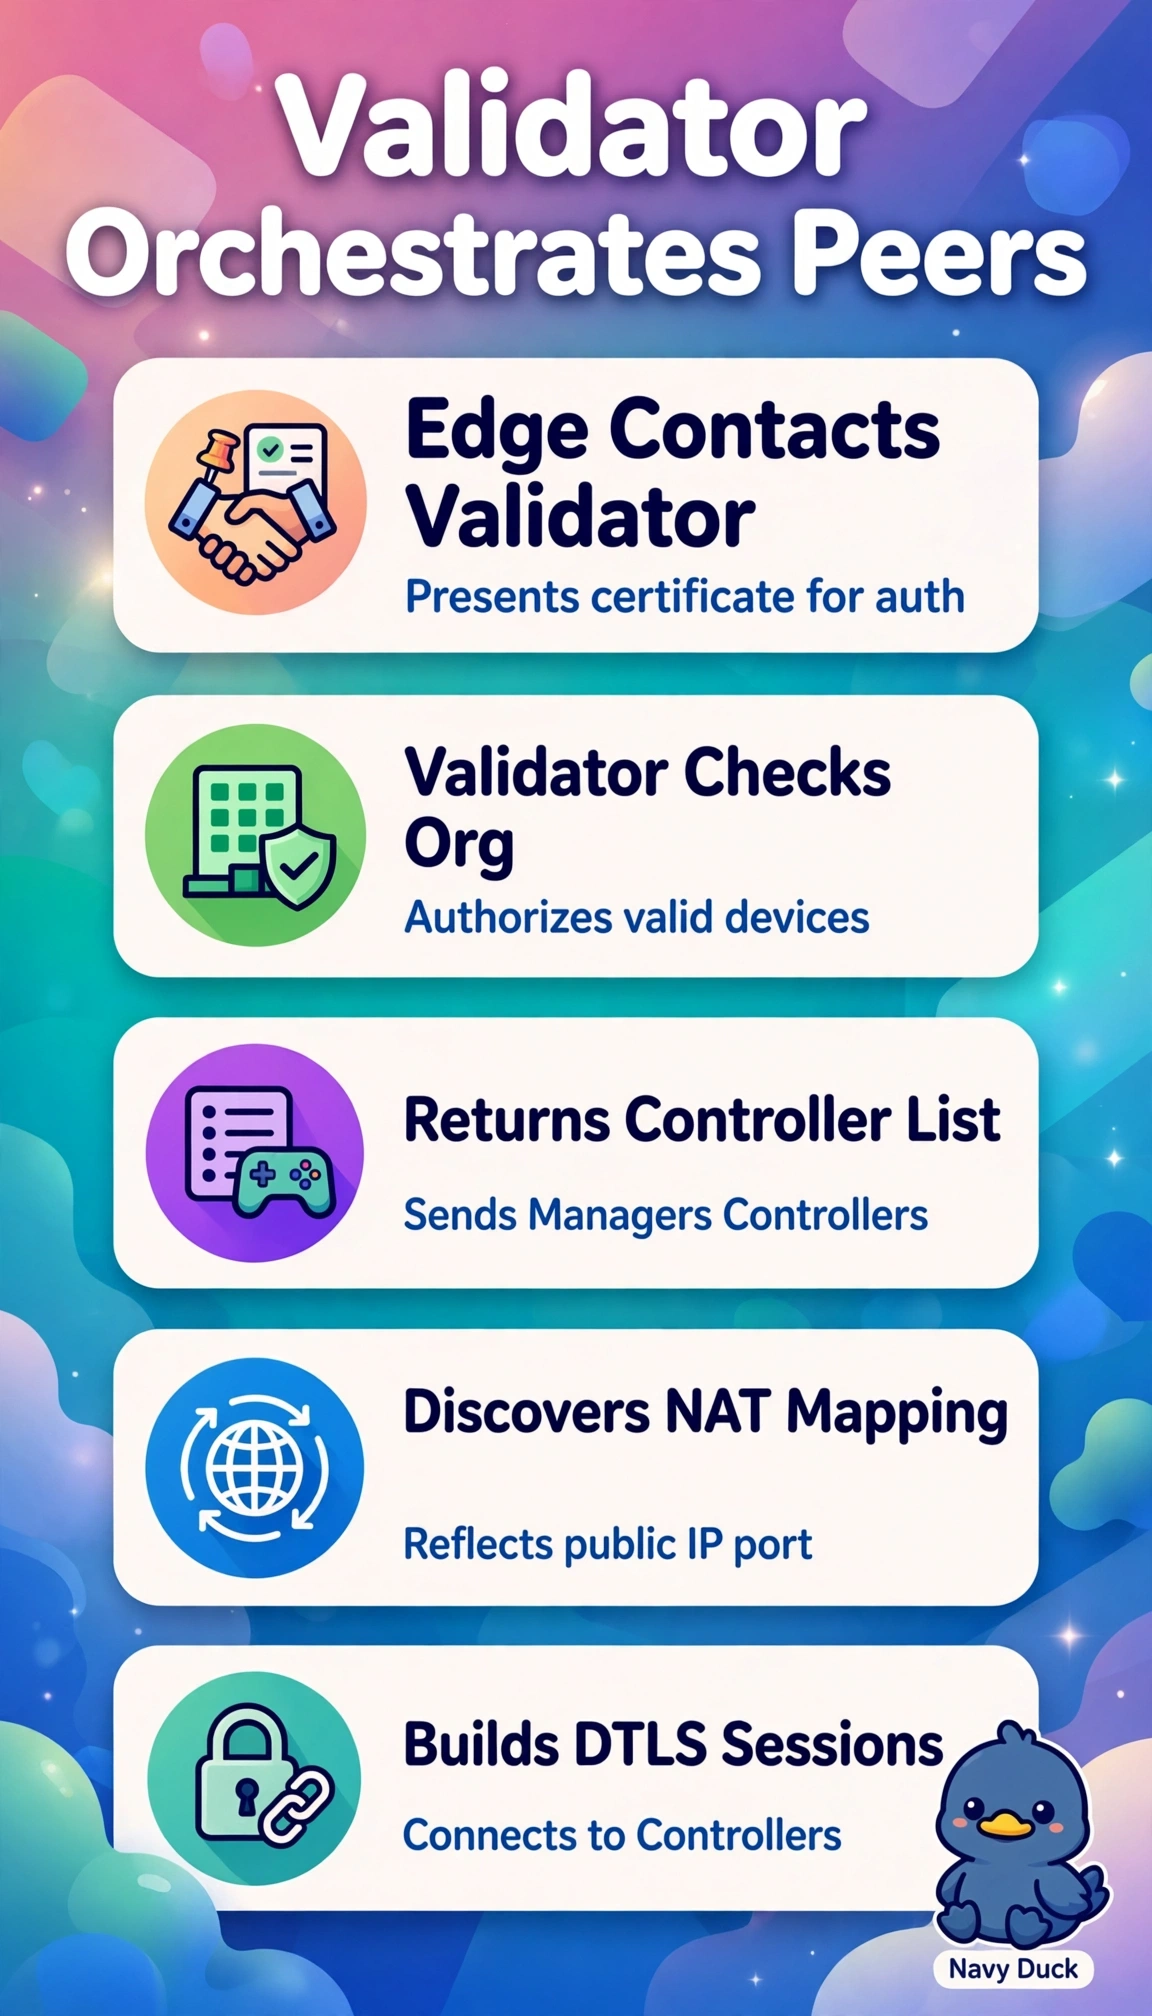
Short Explanation
You're looking for the introducer, not the manager. The Validator performs initial orchestration and tells devices who to trust behind NAT. It's like a wedding coordinator who checks invitations then seats everyone.
Full Explanation
The SD-WAN Validator, formerly vBond, is the always-reachable orchestrator that authenticates every device certificate against the organization, returns the authorized lists of SD-WAN Manager and SD-WAN Controllers, and facilitates NAT traversal by reflecting the public IP and port seen during the initial connection so peers can build DTLS and TLS sessions to the correct public mappings. Pointing initial orchestration at the SD-WAN Manager fails by plane because the Manager, formerly vManage, provides management, templates and monitoring after orchestration, but does not perform initial authentication and NAT discovery. Expecting full-mesh DTLS before orchestration fails by sequence because Edge routers cannot know legitimate Controller addresses until the Validator authorizes them, so sessions would have no trust anchor. Learning controllers via OMP fails by protocol order because OMP only runs after DTLS to Controllers is established, so it cannot bootstrap its own control connections or NAT bindings. Exam caveat: if the question hinges on first contact, NAT reflection and allowed-lists, answer Validator even when Manager and Controller are also present. Practical check: confirm Validator reachability on port 12346 and that the Edge organization name matches the Validator whitelist.