
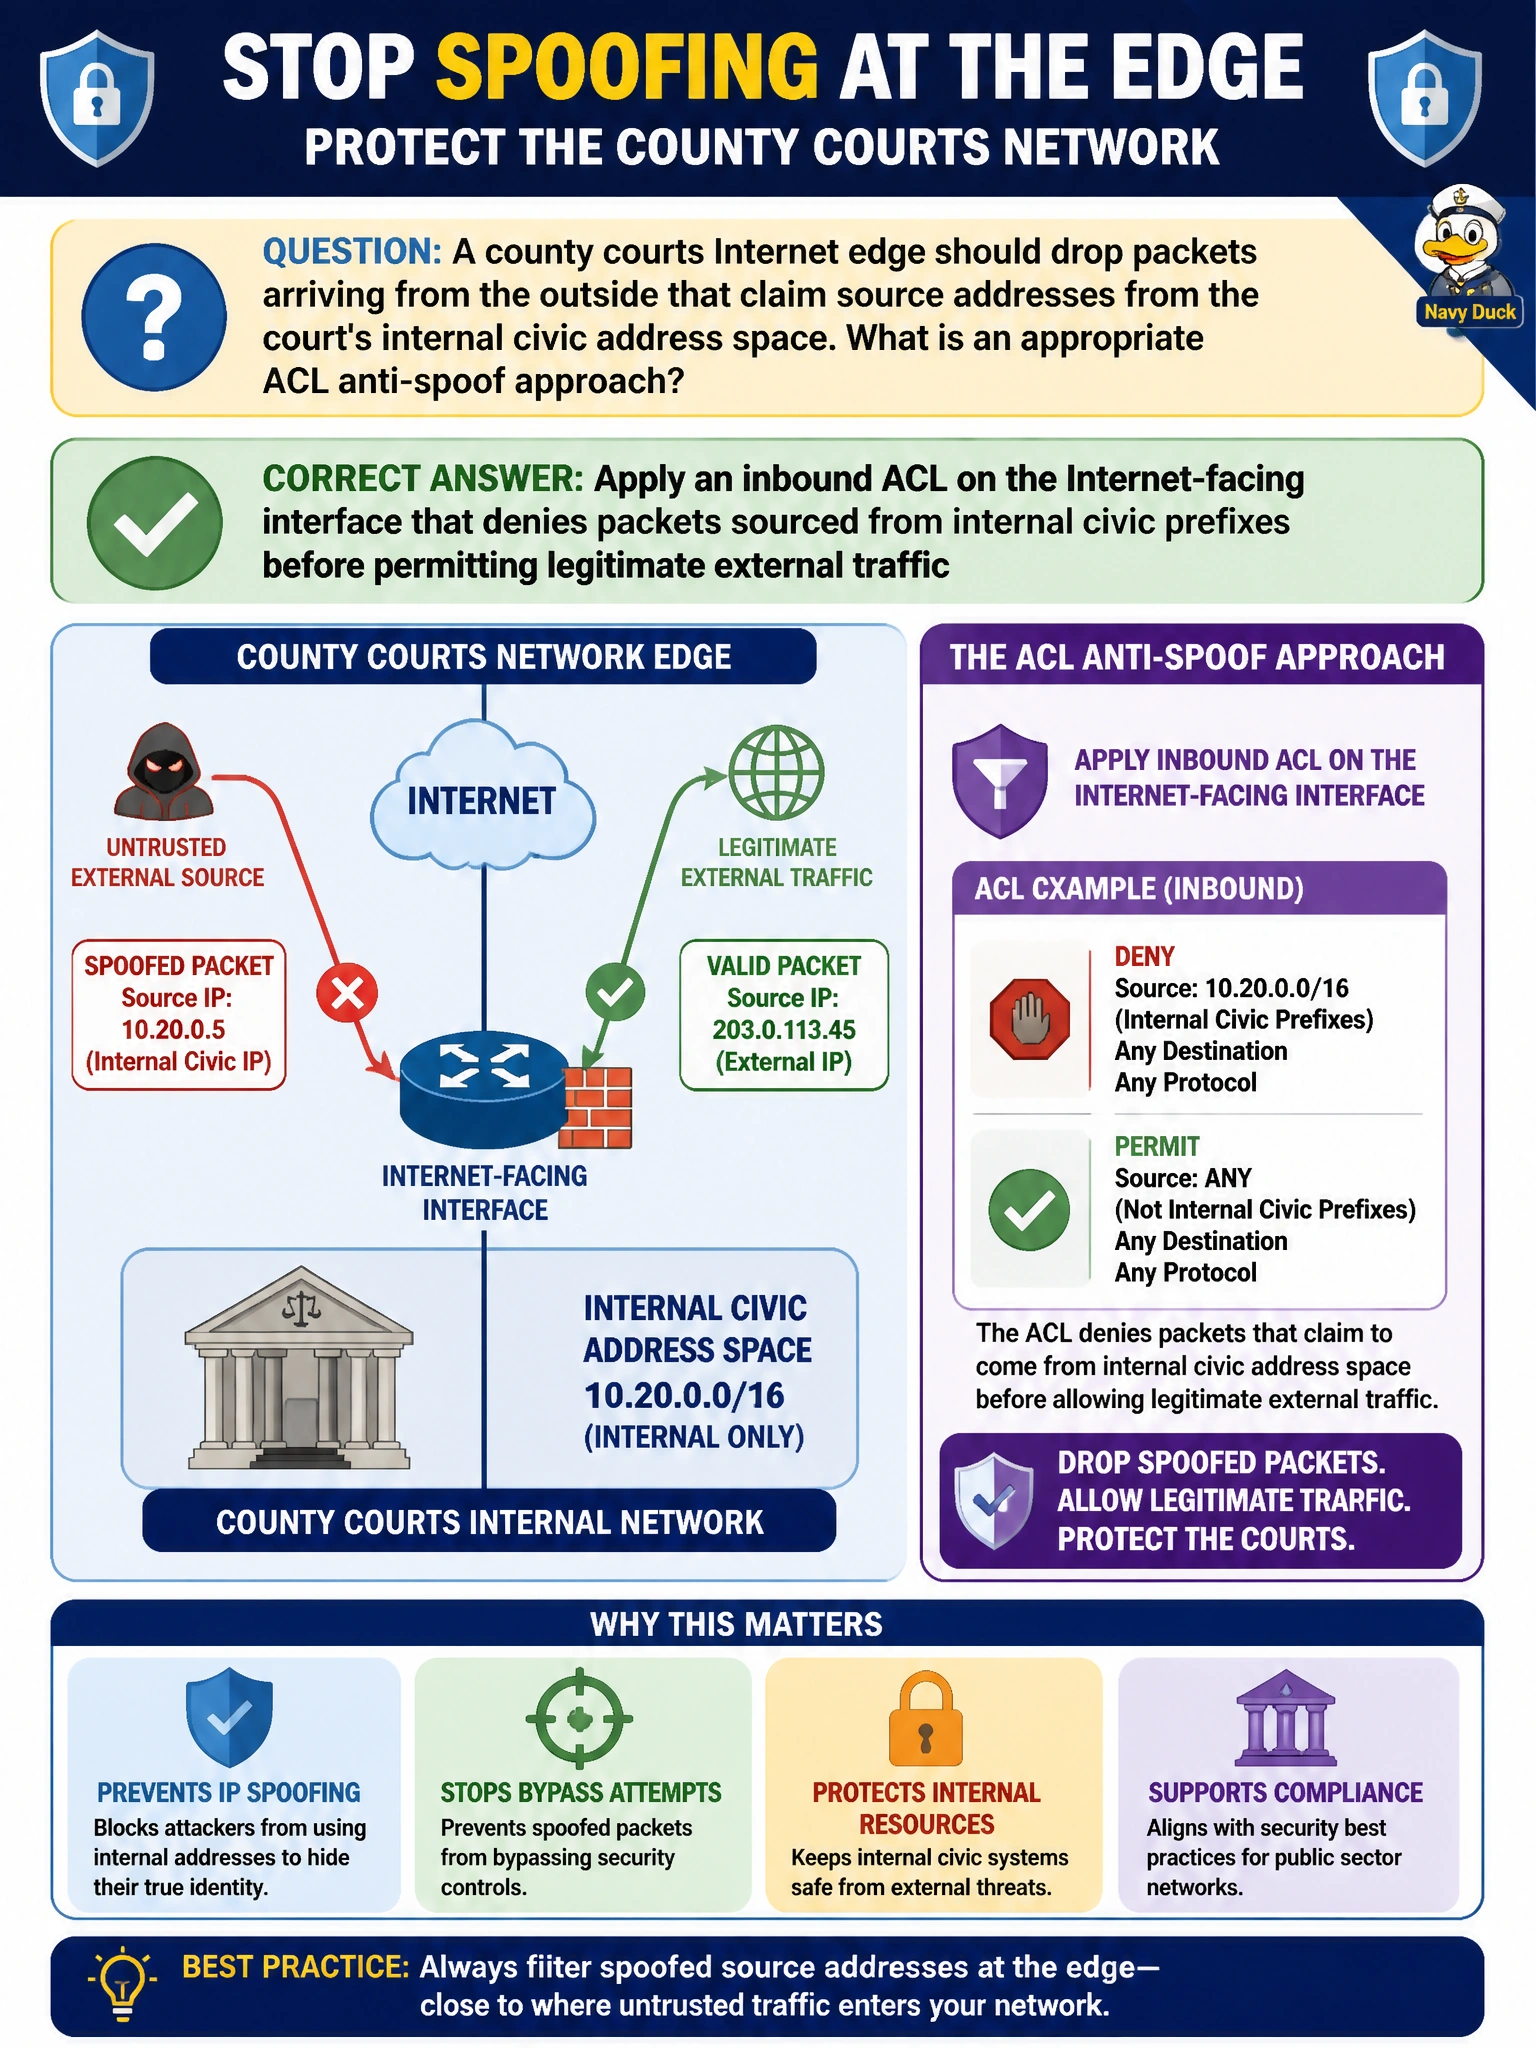
A county courts Internet edge should drop packets arriving from the outside that claim source addresses from the court's internal civic address space. What is an appropriate ACL anti-spoof approach?
Select an answer to reveal the explanation.
Short Explanation
If a package arrives at the front gate claiming it already came from inside the courthouse, toss it. An inbound edge ACL that denies your own internal sources from the Internet does that job.
Full Explanation
A county courts Internet edge should drop packets arriving from the outside that claim source addresses from the court's internal civic address space by applying an inbound ACL on the Internet-facing interface that denies packets sourced from internal civic prefixes before permitting legitimate external traffic. That anti-spoof approach works because forged packets with internal sources appear on the external interface; denying those sources inbound at the edge prevents them from entering the civic network as if they were trusted inside hosts. Applying only an outbound ACL that permits all sources from the Internet toward internal prefixes fails because outbound filtering of egress does not stop inbound spoofed packets at ingress, and a blanket permit of Internet sources does not implement anti-spoof denial of internal source space. Relying solely on increasing OSPF hello timers fails conceptually: hello timers affect adjacency keepalive timing, not validation of IP source legitimacy on the Internet edge. Disabling CEF so spoofed packets are process-switched into a quarantine VRF automatically fails because turning off CEF is not an anti-spoof mechanism and does not auto-quarantine based on source spoofing. Exam caveat: keep the deny-internal-sources entries ahead of broad permits, and do not accidentally deny legitimate traffic that should use those prefixes on internal interfaces—this ACL belongs on the Internet-facing inbound path. Operational check: place explicit denies for RFC1918/internal civic aggregates inbound on the WAN edge, follow with required permits, verify with show access-lists counters while sourcing test packets with spoofed internal addresses from an external test point.