
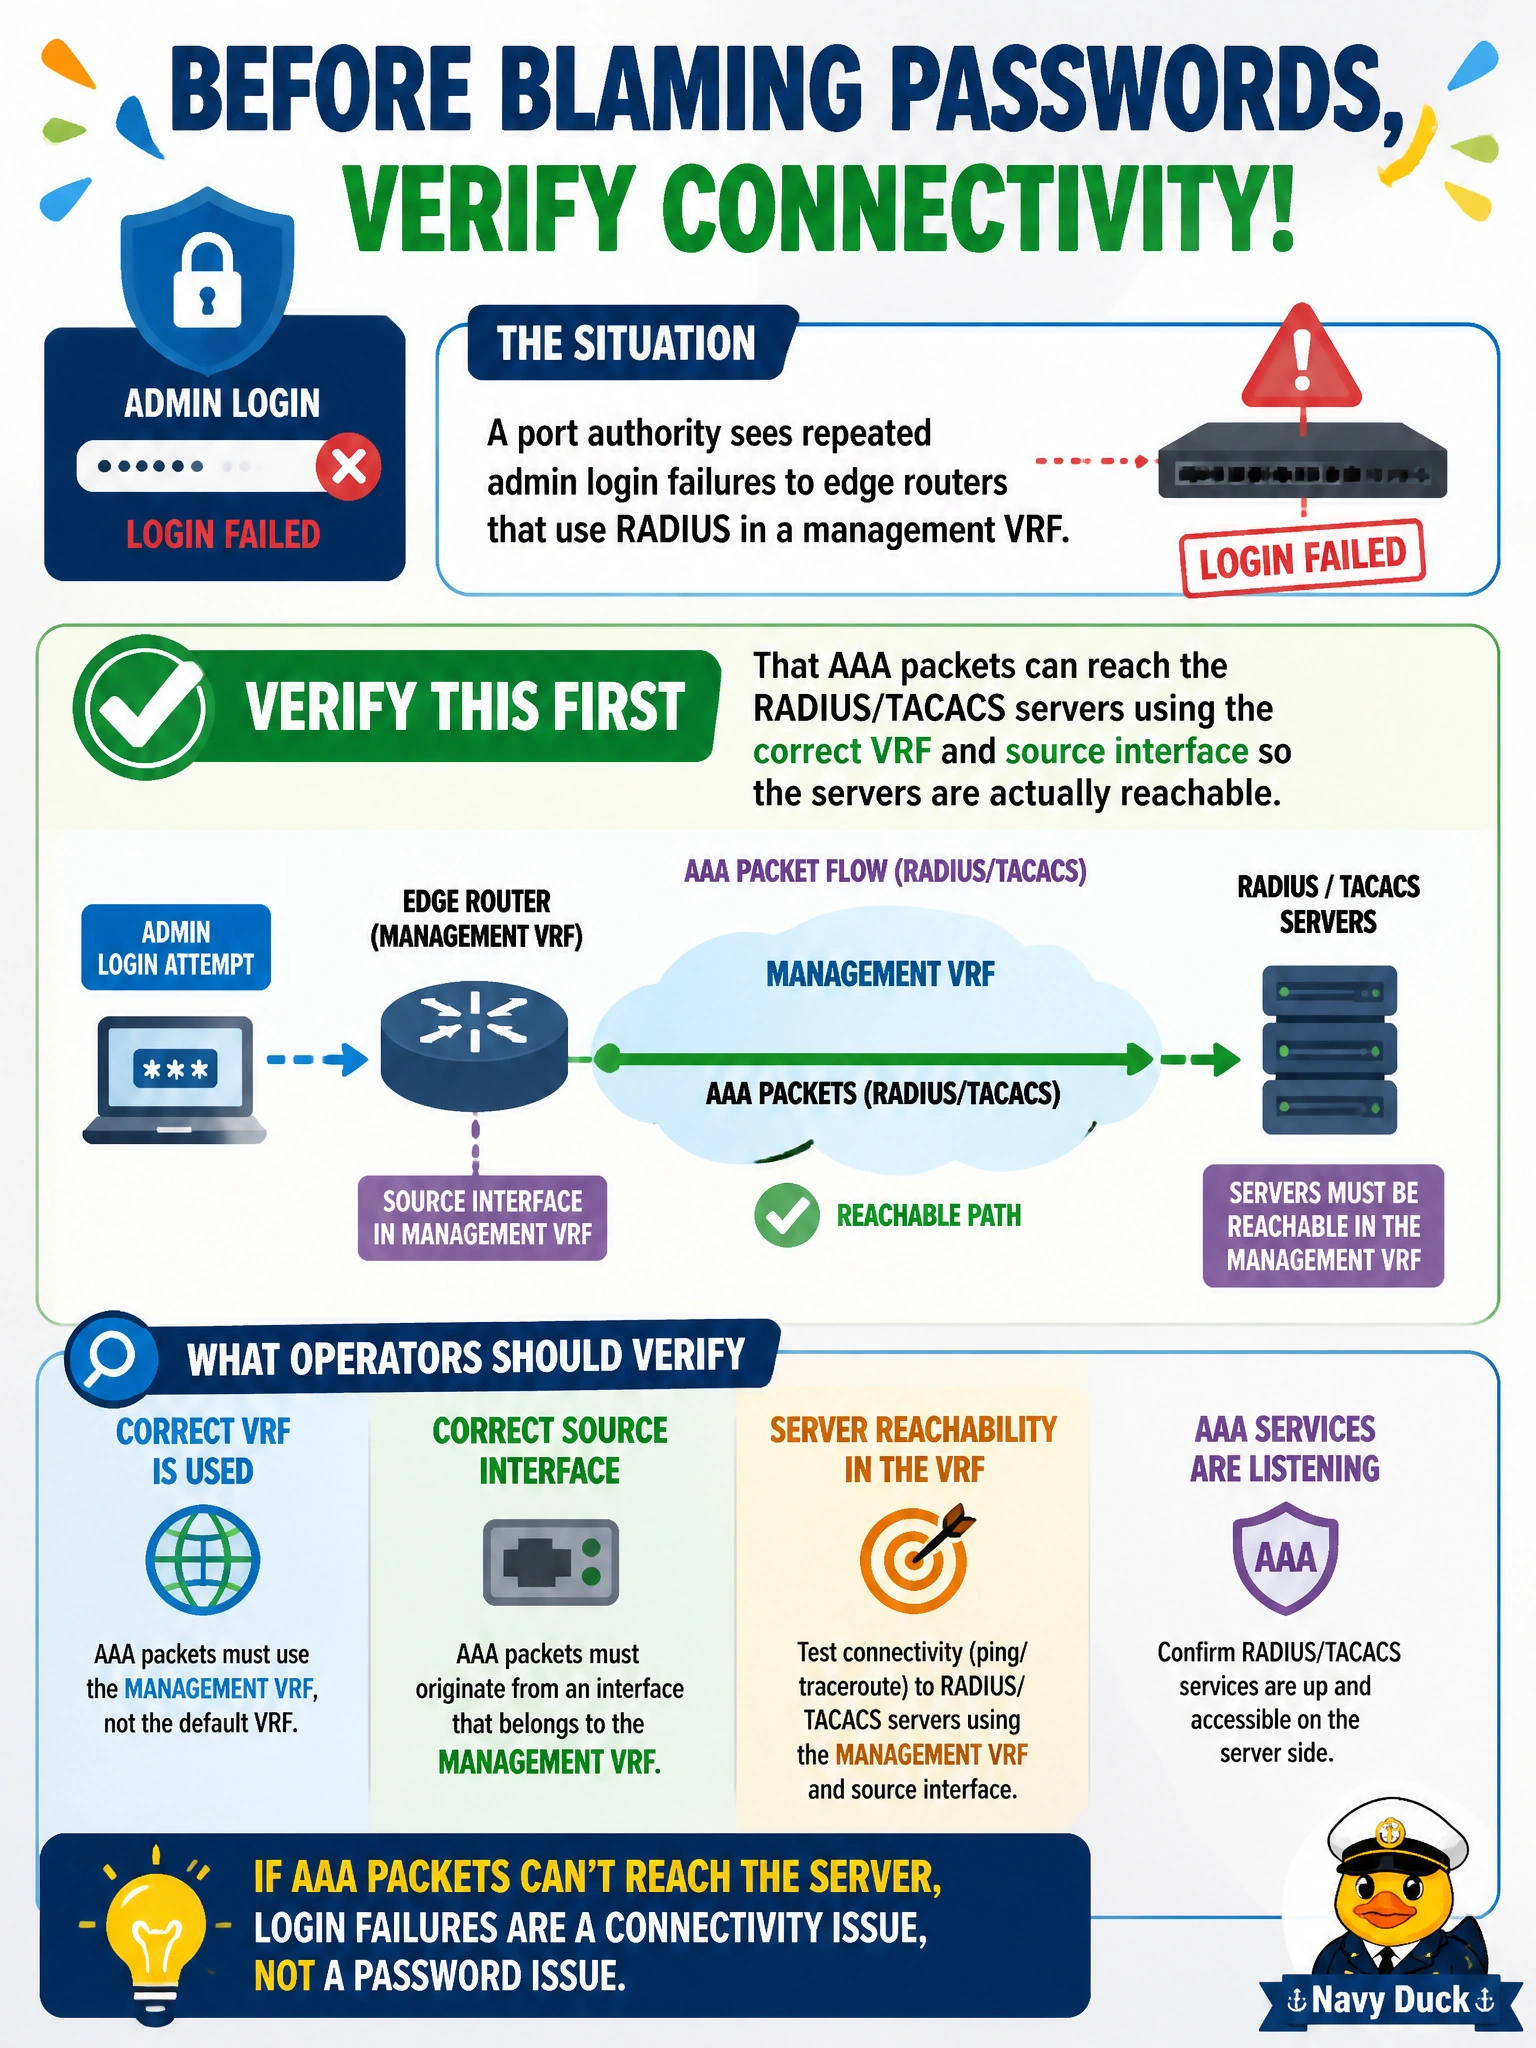
A port authority sees repeated admin login failures to edge routers that use RADIUS in a management VRF. What should operators verify before concluding that user passwords are wrong?
Select an answer to reveal the explanation.
Short Explanation
If the badge server is on the far side of a locked door, wrong passwords aren't your first problem. Prove the router can actually talk to RADIUS/TACACS in the right VRF before grilling the operator's passphrase.
Full Explanation
Repeated admin login failures on port-authority edge routers that use RADIUS in a management VRF should first drive a reachability check: AAA packets must leave via the correct VRF and source interface so the RADIUS/TACACS servers are actually reachable. Wrong passwords are a later hypothesis. The correct approach works because AAA clients bind to IP transport; if the request never arrives or replies return to the wrong context, every login looks like an authentication failure even when credentials are valid. Requiring every VTY ACL to permit only BGP multicasts fails because AAA needs unicast IP reachability to authentication servers, not BGP multicast permissions, and VTY ACLs do not substitute for server path validation. Disabling NetFlow version 5 globally because flow export supposedly blocks RADIUS fails conceptually—NetFlow export is independent of RADIUS client/server exchange and is not a design prerequisite for AAA success. Removing OSPF stub areas from the entire civic WAN before any AAA server can answer fails because OSPF area type is not a universal blocker of AAA; the relevant question is whether the management VRF has a route and return path to the servers. Exam caveat: servers reachable in the global table but not in the management VRF produce especially misleading "bad password" symptoms. Operational check: from the router in the management VRF, ping/traceroute the AAA servers using the configured source interface, verify aaa group server vrf/source-interface settings, confirm ACLs/firewalls allow RADIUS/TACACS ports, then retest login before resetting civic admin credentials.