
A transit authority reviews AAA debugs after failed civic-router logins. How should an explicit reject from the AAA server be treated differently from a timeout with no reply?
Select an answer to reveal the explanation.
Short Explanation
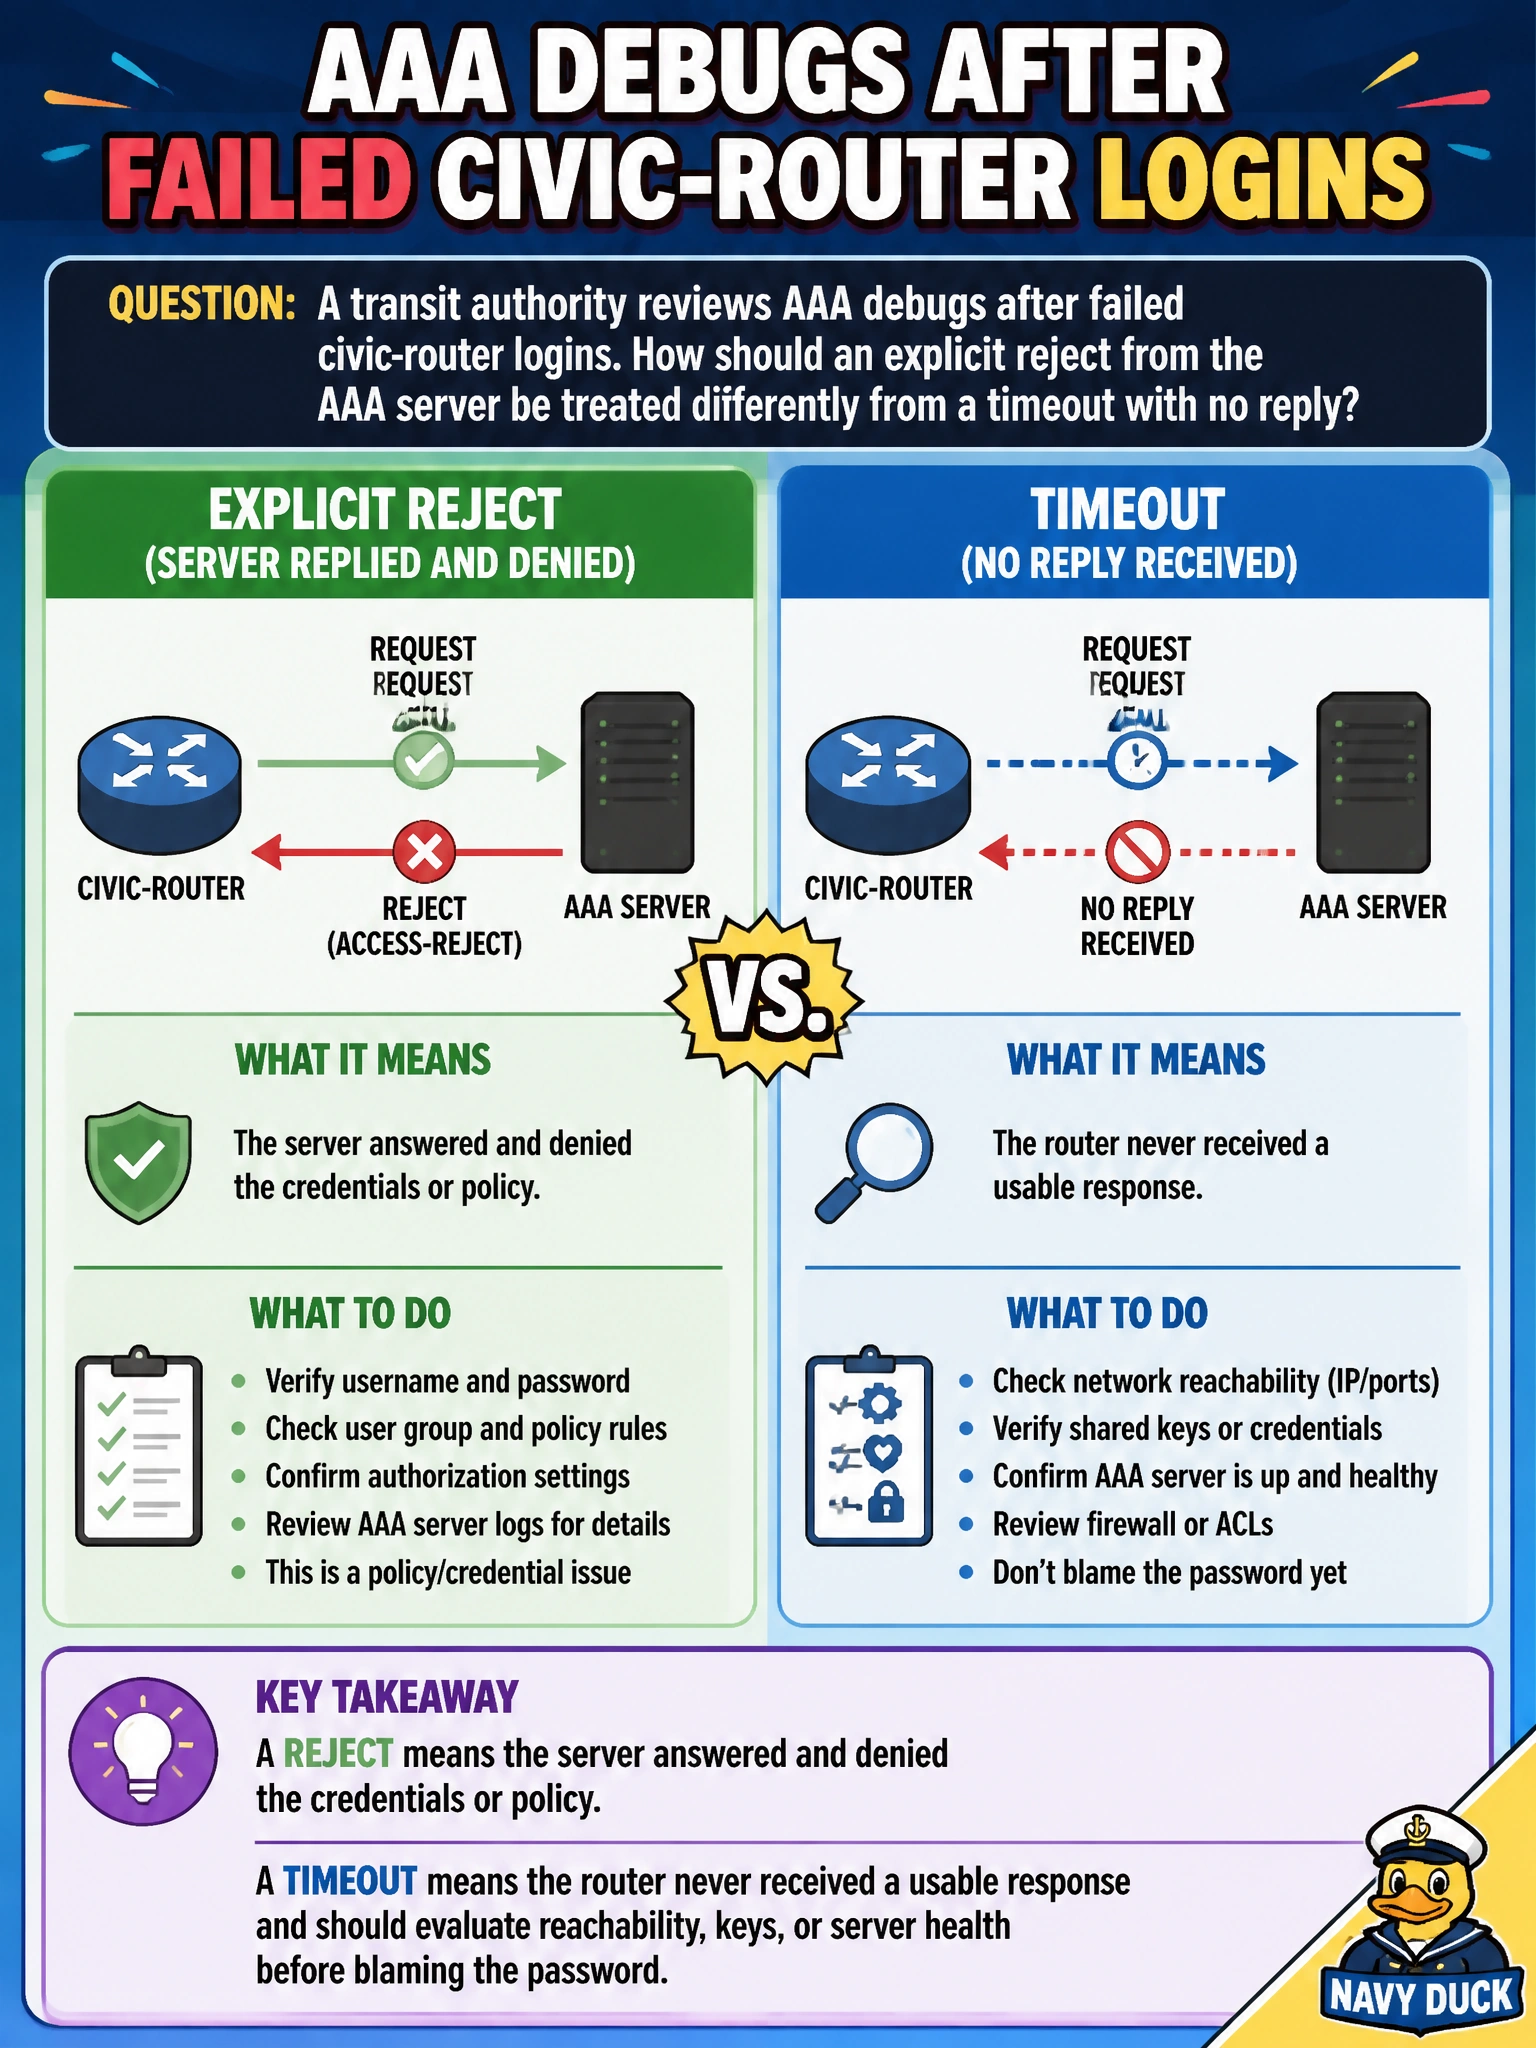
A reject is the security desk saying "no." A timeout is nobody picking up the phone. Don't reset the user's password until you know whether HQ answered or the call never got there.
Full Explanation
When a transit authority reviews AAA debugs after failed civic-router logins, an explicit reject from the AAA server must be treated differently from a timeout with no reply. A reject means the server answered and denied the credentials or policy—so the path and crypto/keying to the server largely worked, and the investigation should focus on username, password, authorization attributes, or server-side policy. A timeout means the router never received a usable response, so reachability, VRF/source-interface, shared keys, server process health, or firewalling should be evaluated before blaming the operator password. Treating reject and timeout as identical and always meaning the local enable secret is wrong fails because enable-secret issues are a separate privilege path and neither AAA outcome maps exclusively to that root cause. Claiming a timeout always proves the username is authorized and only CoPP must be removed fails conceptually: a timeout proves non-response, not successful authorization, and CoPP is only one of many possible causes of lost AAA traffic. Mapping reject to disabled CEF and timeout to invalid ACL numbering fails because CEF and ACL numbering schemes are unrelated to AAA accept/reject semantics. Exam caveat: intermittent timeouts can look like flaky passwords to users; correlate debug timestamps with server logs before forcing password resets across the civic admin population. Operational check: capture whether AAA debugs show REJECT versus TIMEOUT/ERROR, then for timeouts verify management VRF routing, source interface, ACL/CoPP permits for TACACS+/RADIUS, and server reachability; for rejects verify credentials and server authorization profiles for that admin identity.