
An emergency-management office scopes WAN VPN training to ENARSI Domain 2.3. Which boundary correctly keeps focus on DMVPN rather than FlexVPN concentration?
Select an answer to reveal the explanation.
Short Explanation
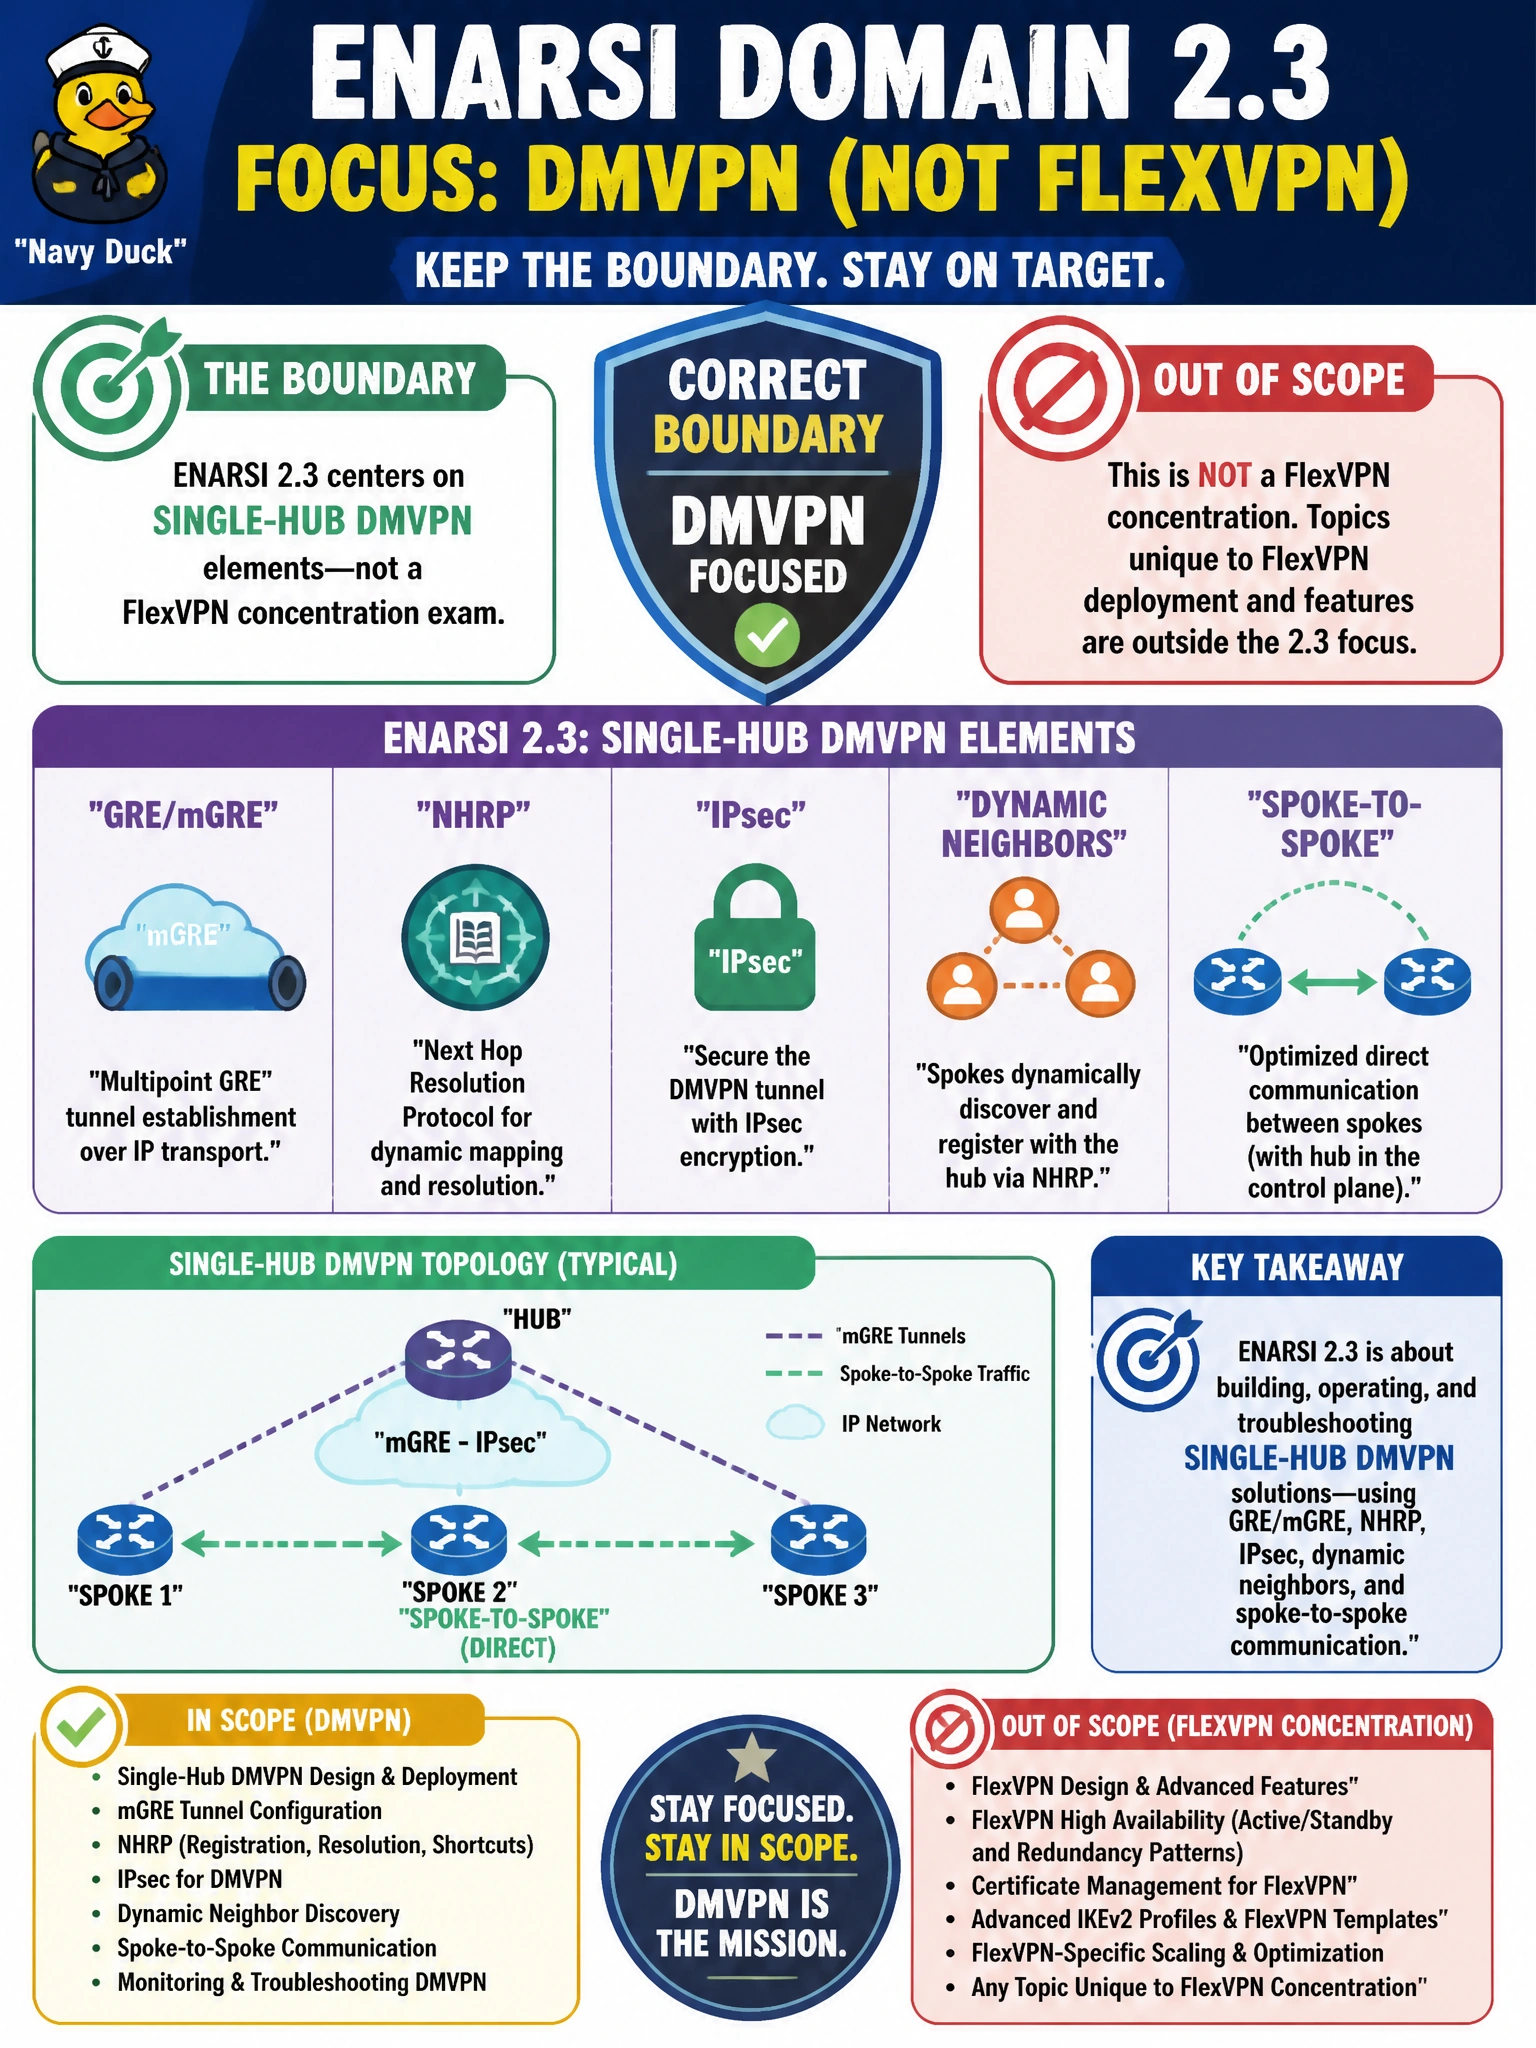
You can keep your ENARSI 2.3 training focused on the single-hub DMVPN toolkit: GRE/mGRE, NHRP, IPsec, dynamic neighbors, and spoke-to-spoke behavior. That gives you the right boundary without turning the course into FlexVPN training.
Full Explanation
Scoping emergency-management WAN VPN training to ENARSI Domain 2.3 means centering on single-hub DMVPN elements: GRE/mGRE, NHRP, IPsec, dynamic neighbors, and spoke-to-spoke behavior. That is the domain boundary for EOC and shelter interconnect labs; it is not a FlexVPN concentration exam. Treating the domain as primarily FlexVPN IKEv2 virtual-access authoring with no DMVPN topics misstates the blueprint emphasis. Requiring full CCIE SP MPLS-TE labs before any DMVPN spoke may register invents a prerequisite that Domain 2.3 does not impose. Declaring DMVPN out of scope and training only on Catalyst Center fabric virtual-network design abandons the VPN Technologies DMVPN objectives emergency-management engineers need for ENARSI. Exam caveat: when a stem cites Domain 2.3 or single-hub DMVPN, focus on GRE/mGRE, NHRP, IPsec, and dynamic-neighbor or spoke-to-spoke behavior rather than neighboring topics. Practical check: lab a single hub with those elements, verify registration and optional spoke-to-spoke operation, and capture before-and-after outputs in the municipal ticket to prove the fix. Re-check overlay or AAA health after the change window closes.