
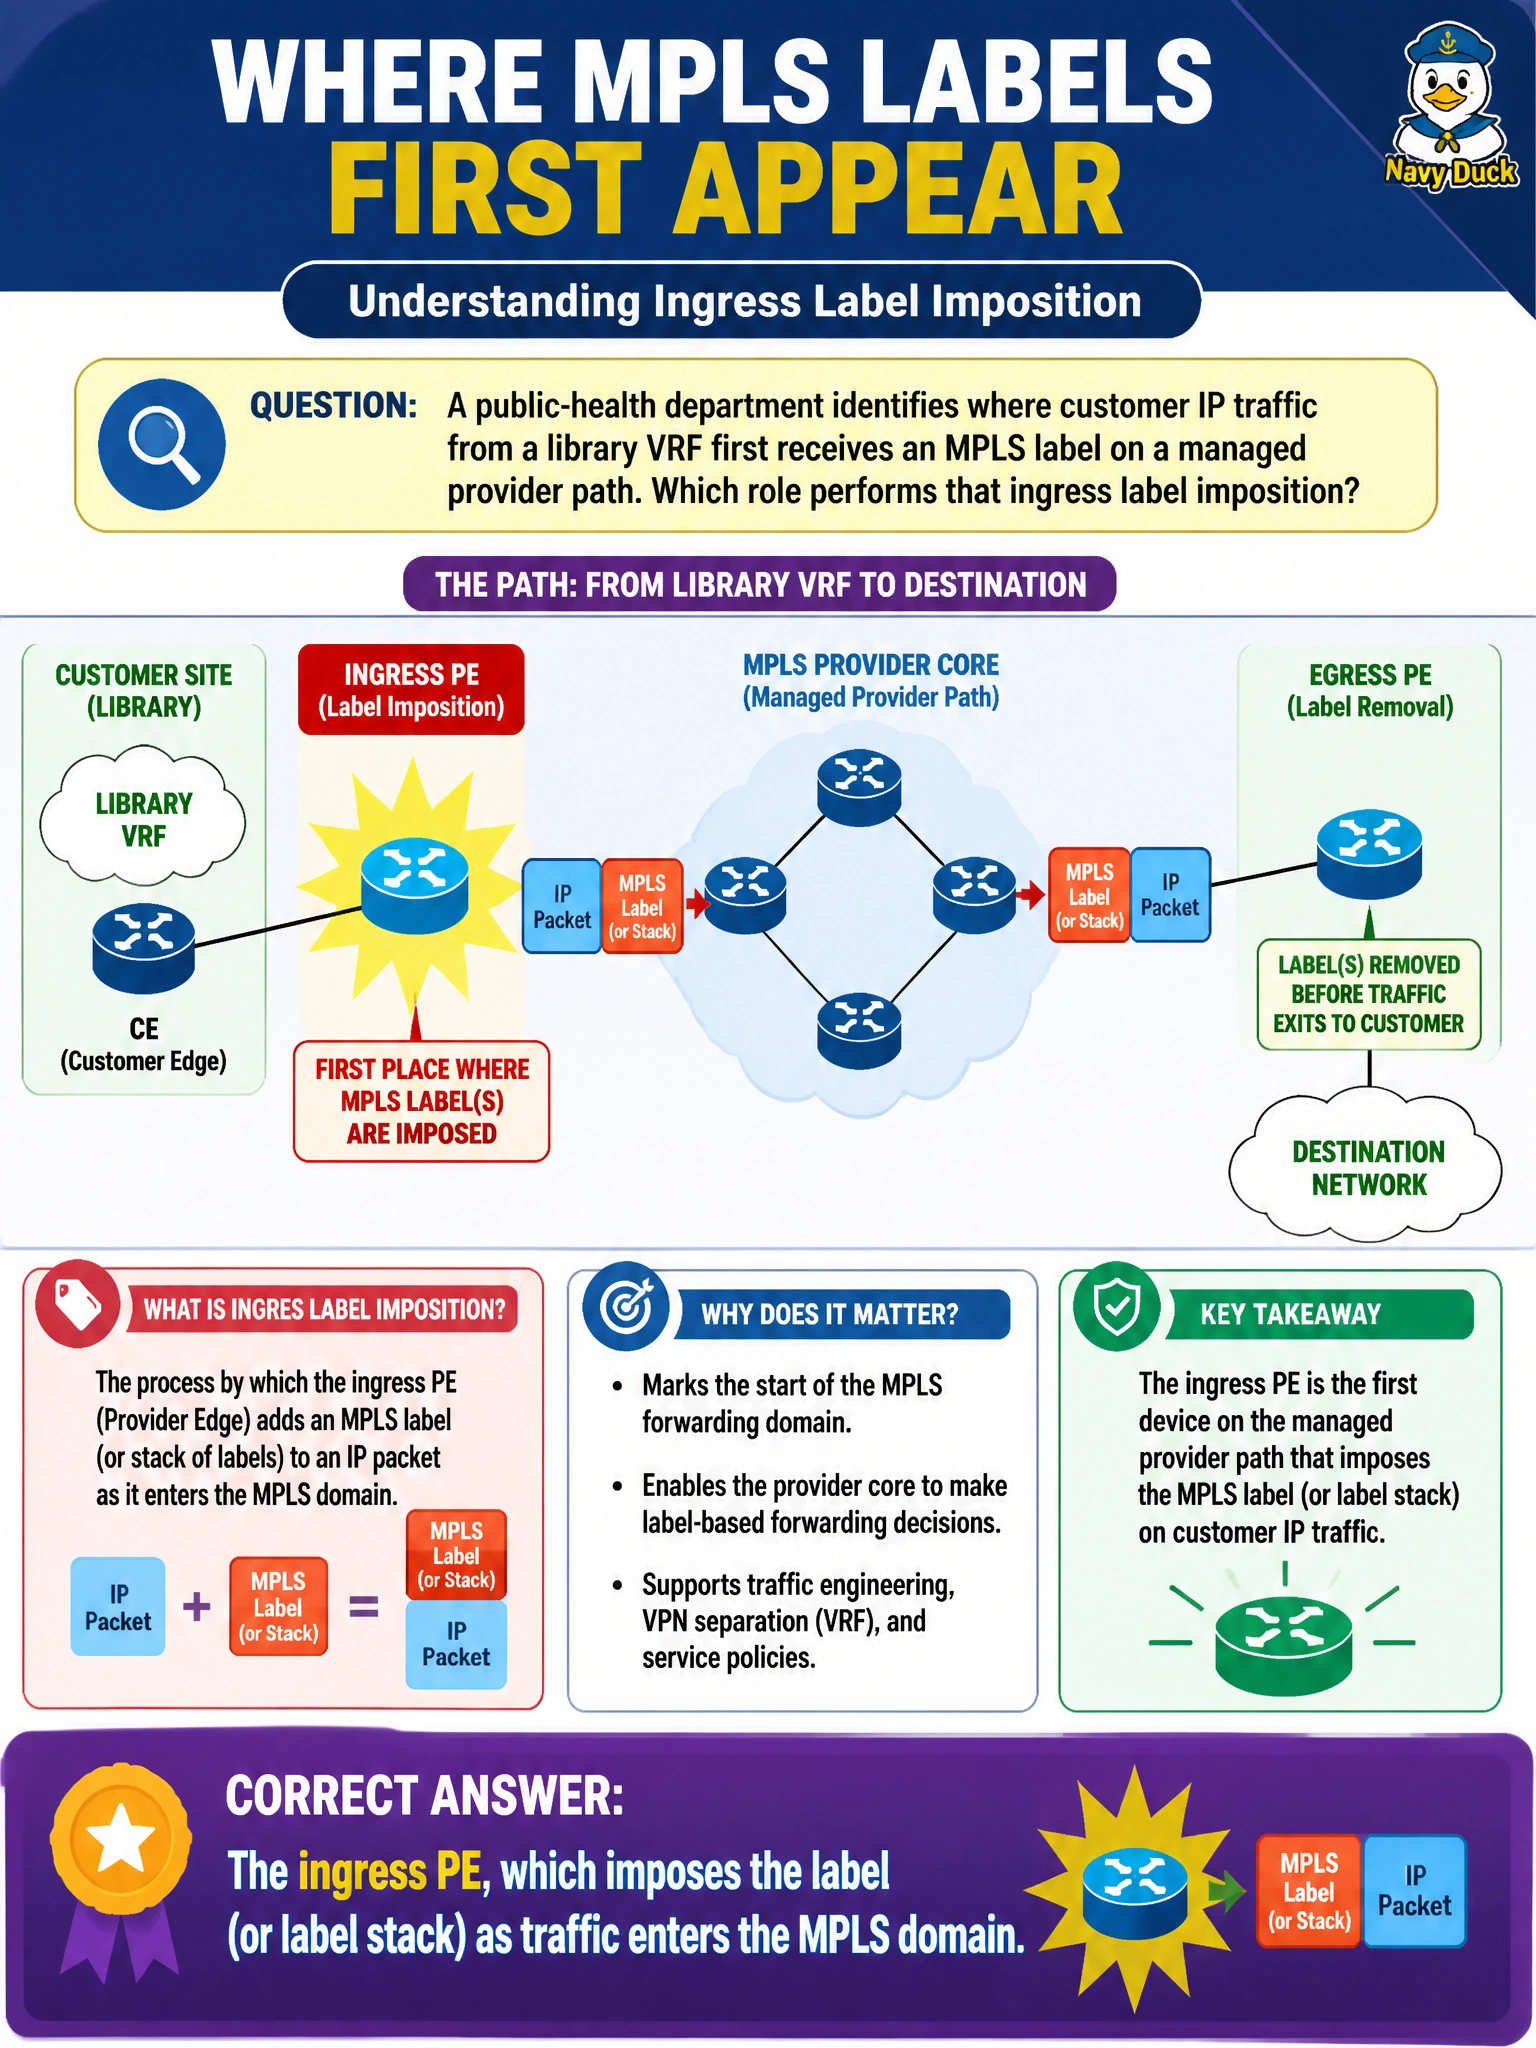
A public-health department identifies where customer IP traffic from a library VRF first receives an MPLS label on a managed provider path. Which role performs that ingress label imposition?
Select an answer to reveal the explanation.
Short Explanation
The ingress PE is the on-ramp attendant: civic IP shows up unlabeled from the CE/VRF, and that PE sticks the MPLS label(s) on before the packet hits the labeled core.
Full Explanation
When a public-health department asks where customer IP traffic from a library VRF first receives an MPLS label on a managed provider path, the answer is the ingress PE. Unlabeled IP from the CE/VRF arrives on the attachment circuit; the ingress PE performs label imposition—pushing the transport label and, for L3VPN, the inner VPN label—as traffic enters the MPLS domain. That on-ramp role is the first place provider labels are applied for that civic flow.
The CE router does not always impose provider labels before packets leave the library LAN in classic PE-CE IP attachment. The CE speaks IP (or a PE-CE routing protocol) to the PE; provider label imposition is a PE MPLS-domain function, not a mandatory CE LAN behavior.
A core P router originating the VPN label and pushing it toward the CE reverses edge and core roles. P routers swap transport labels in the core; they do not originate VPN labels toward CEs or push labels onto CE-bound unlabeled attachment traffic as their primary role.
The egress PE only, because labels are never added until the final hop, contradicts imposition-at-ingress. The egress PE is associated with disposition (and receiving PHP'd packets), not with first adding labels at the last hop.
Exam caveat: in L3VPN the stack is typically VPN label plus outer transport label; PHP may remove the outer label before the egress PE. Still, first imposition for CE IP entering the provider MPLS domain is at the ingress PE.
Operational check: on the ingress PE, show mpls forwarding-table / show ip cef vrf <library> should show push of labels toward the core; the PE-CE interface should show unlabeled IP. Packet capture on the PE-P link should show labeled frames after imposition.