
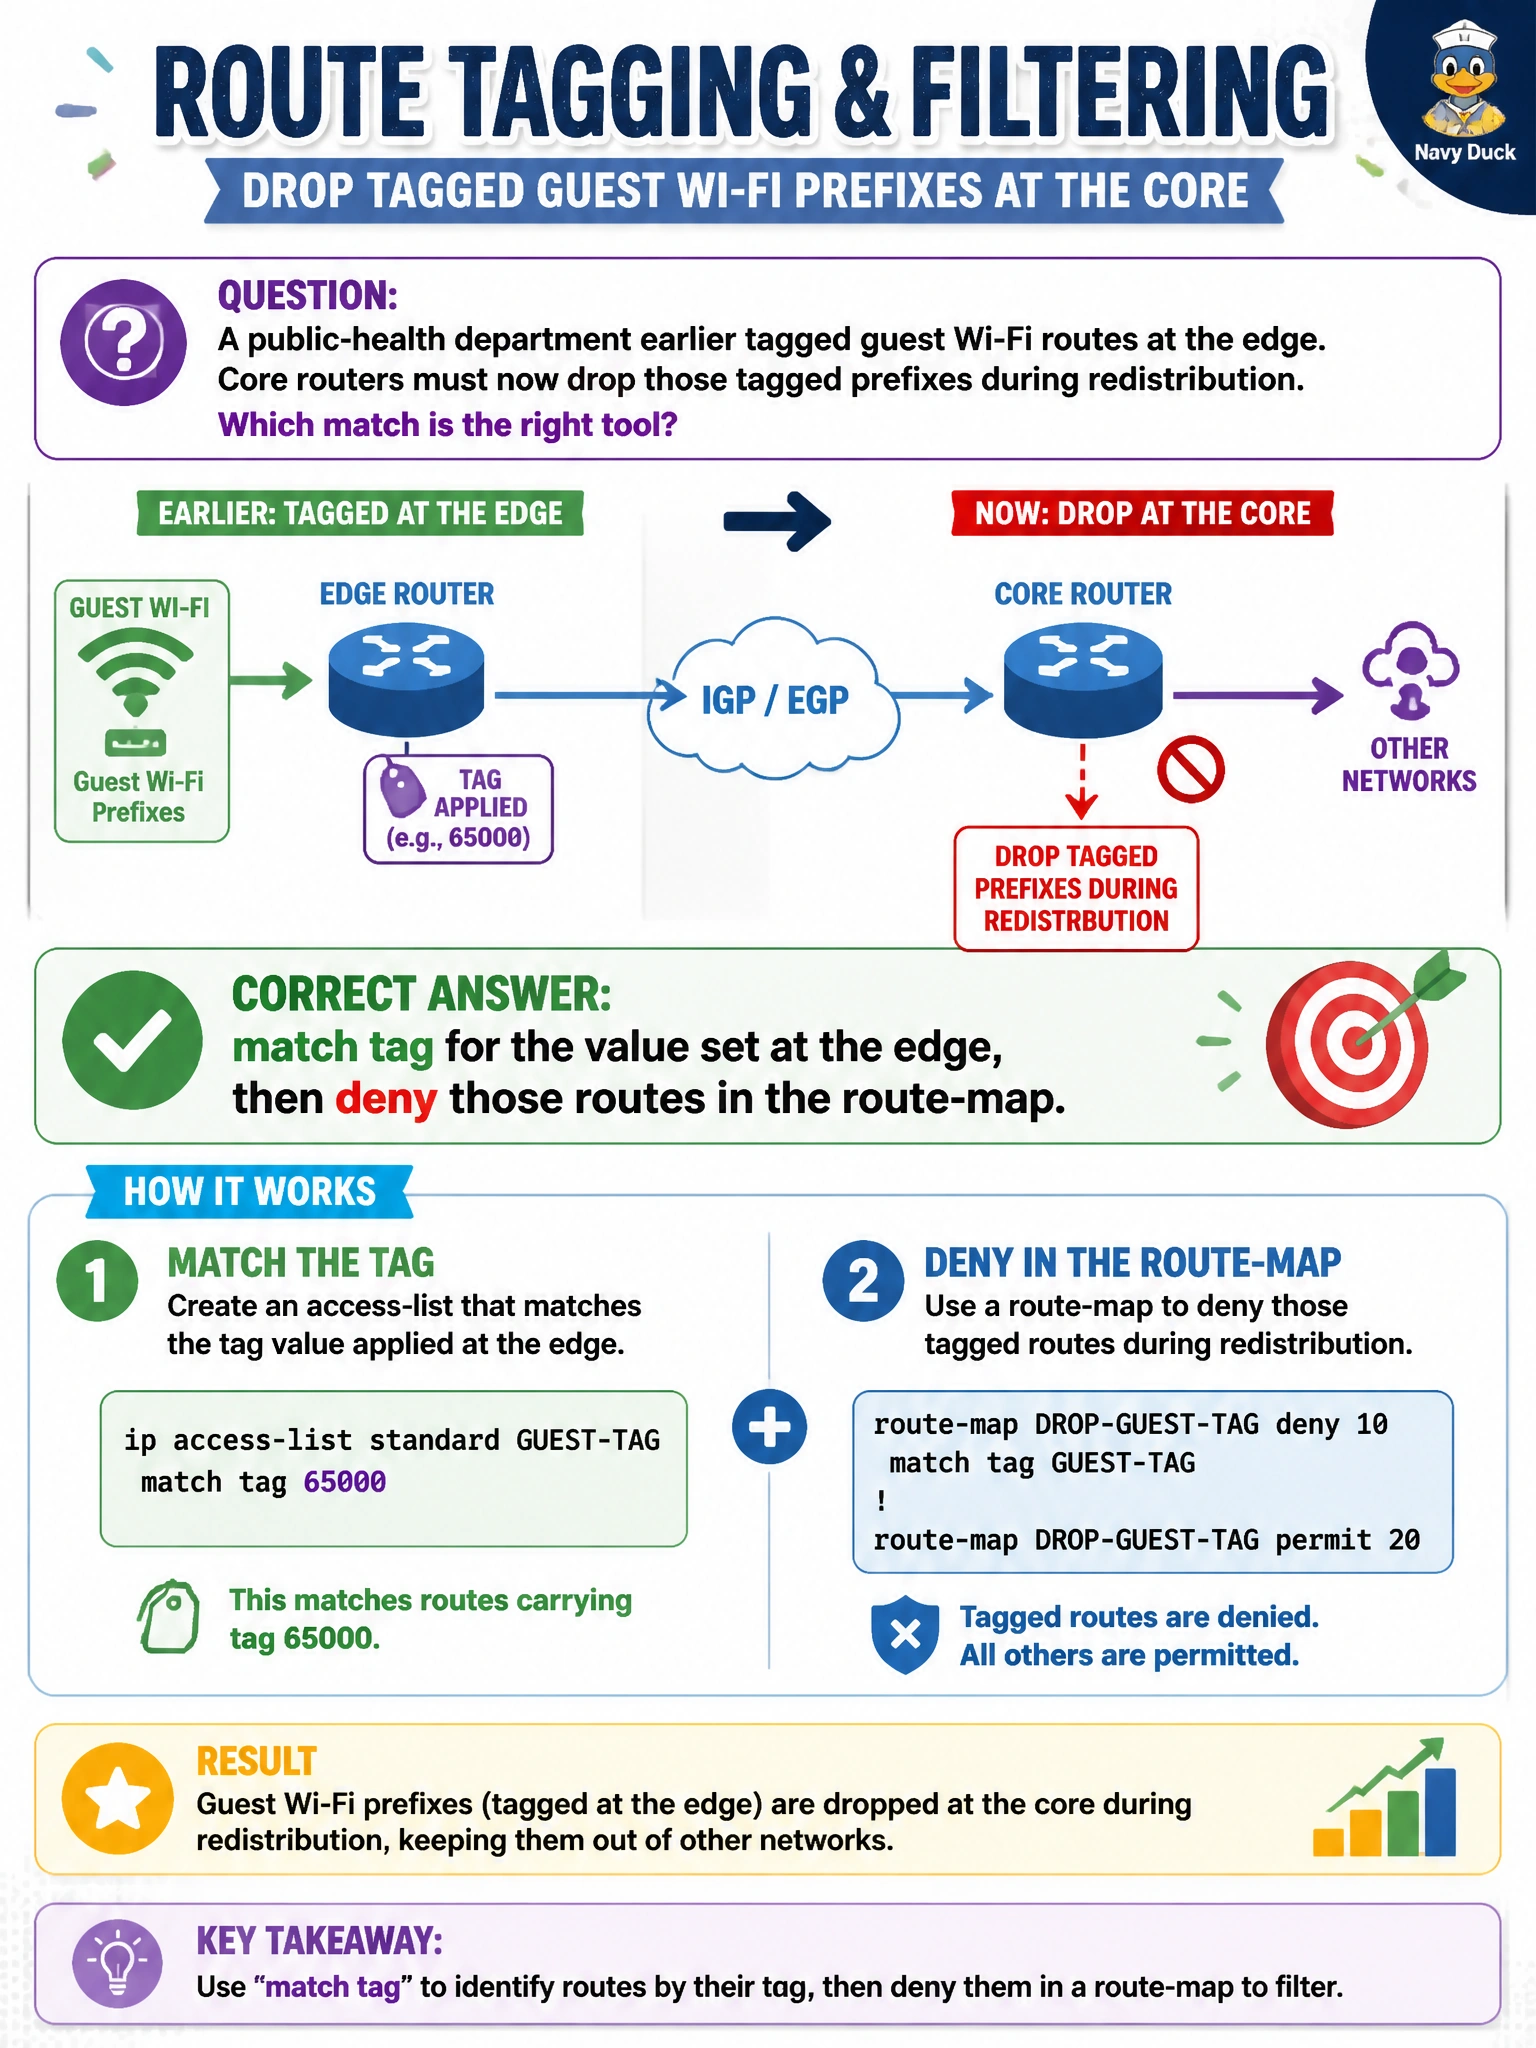
A public-health department earlier tagged guest Wi-Fi routes at the edge. Core routers must now drop those tagged prefixes during redistribution. Which match is the right tool?
Select an answer to reveal the explanation.
Short Explanation
Those edge sticky notes are still on the guest routes. Core policy just matches the same tag and denies it, so you don't have to re-list every Wi-Fi prefix by hand.
Full Explanation
When guest Wi-Fi routes were tagged at the public-health edge during redistribution, that numeric tag travels with the route in the IGP as an external attribute (protocol-dependent display). Core routers that must drop those tagged prefixes during a later redistribution should match tag <same-value> and deny those matches in the route-map (then permit other prefixes as required). This avoids maintaining a brittle ACL of every guest Wi-Fi prefix and stays aligned with the edge tagging scheme.
The as-path match pointing at the guest SSID name is wrong because as-path applies to BGP AS_PATH regex, not an SSID name and not IGP tags. The community-list match built from OSPF area IDs only is wrong because community-list targets BGP communities, not OSPF area IDs, and does not select IGP-tagged guest routes. The source-protocol connected match used exclusively for wireless controllers is wrong because it would only select connected sources, missing already-redistributed guest externals whose source protocol is no longer connected.
Exam caveat: the tag value at the core must equal the value set at the edge; undocumented tag schemes cause silent policy misses. match tag works for routes that still carry the tag into the redistribution process—if an intermediate redistribute stripped tags, the core cannot match them. Prefer deny-by-tag plus an explicit permit for legitimate health-department prefixes so implicit deny does not over-block.
Operational check: identify a known guest prefix with show ip route <prefix> detail (or protocol external output) and note its tag. Apply the core redistribute route-map with match tag deny, then confirm that prefix no longer enters the target domain while untagged clinic prefixes do. show route-map hit counters on the deny clause should increase when guest routes are evaluated.