
At a bank, reviewers compare several probes against one web application from the same afternoon. Which probe is command injection?
Select an answer to reveal the explanation.
Short Explanation
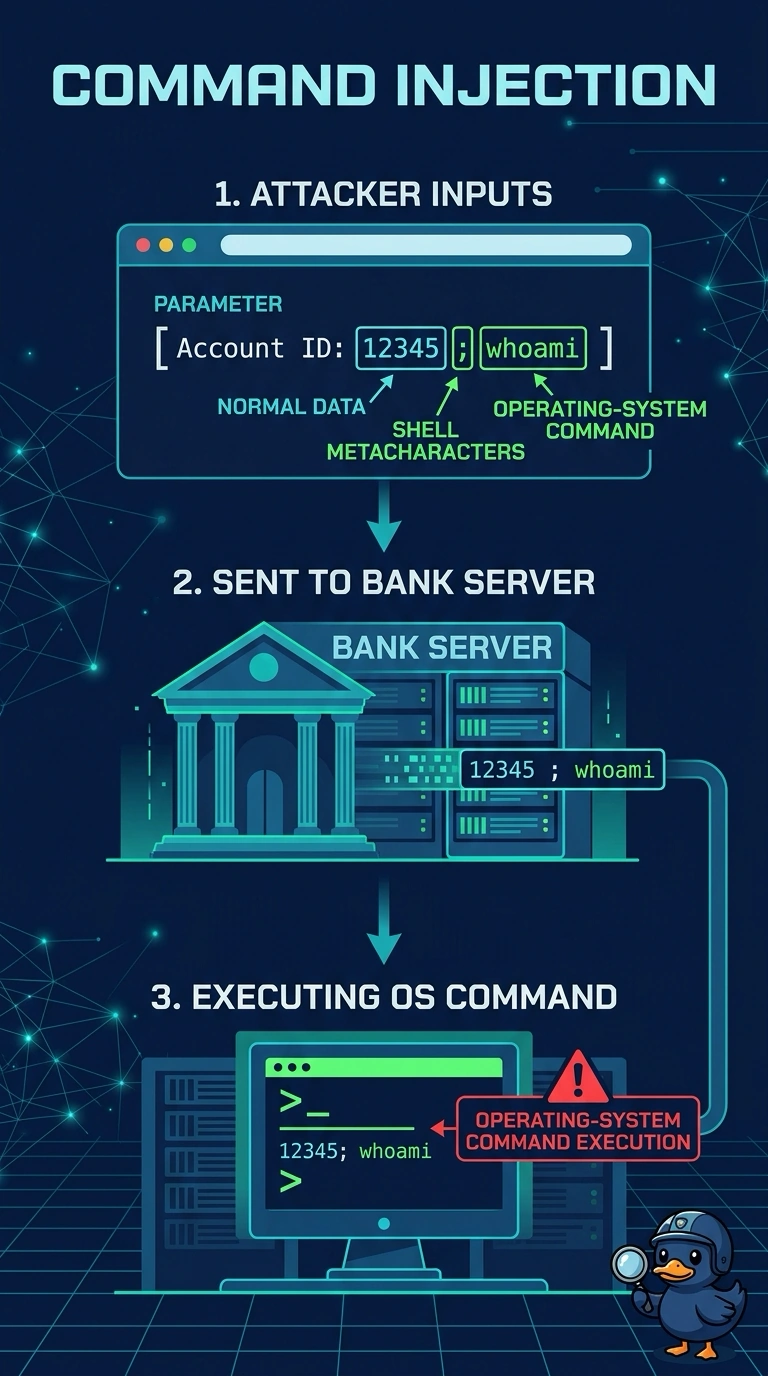
Three knocks can sound alike until you notice who they are calling. You want the probe aimed at an operating-system command, and shell metacharacters in the parameter are that probe. The trap is picking the SQL comment, the script tag, or a bare SYN.
Full Explanation
Command injection is input aimed at a command interpreter so the server runs an operating-system command. Shell metacharacters sent for that purpose are the command-injection probe, distinct from syntax aimed at a database or a browser. Shell metacharacters in a parameter, aimed at an operating-system command on the bank server, is the matching probe. A quote followed by a SQL comment in a parameter, aimed at changing the database query behind the form, is SQL injection syntax directed at the query, not at a shell. A script tag in a parameter, aimed at running in the browser of a staff member who later opens the page, is cross-site scripting aimed at a browser. A single SYN packet to the site, aimed at opening a transport session and carrying no application command, is the start of a TCP handshake and contains no command, query, or script. On the exam, the characters matter only together with the sink they target; metacharacters are command injection when they are aimed at an operating-system command. In operations, check whether that parameter is passed to a shell, a query, or the HTML response before you name the probe.