
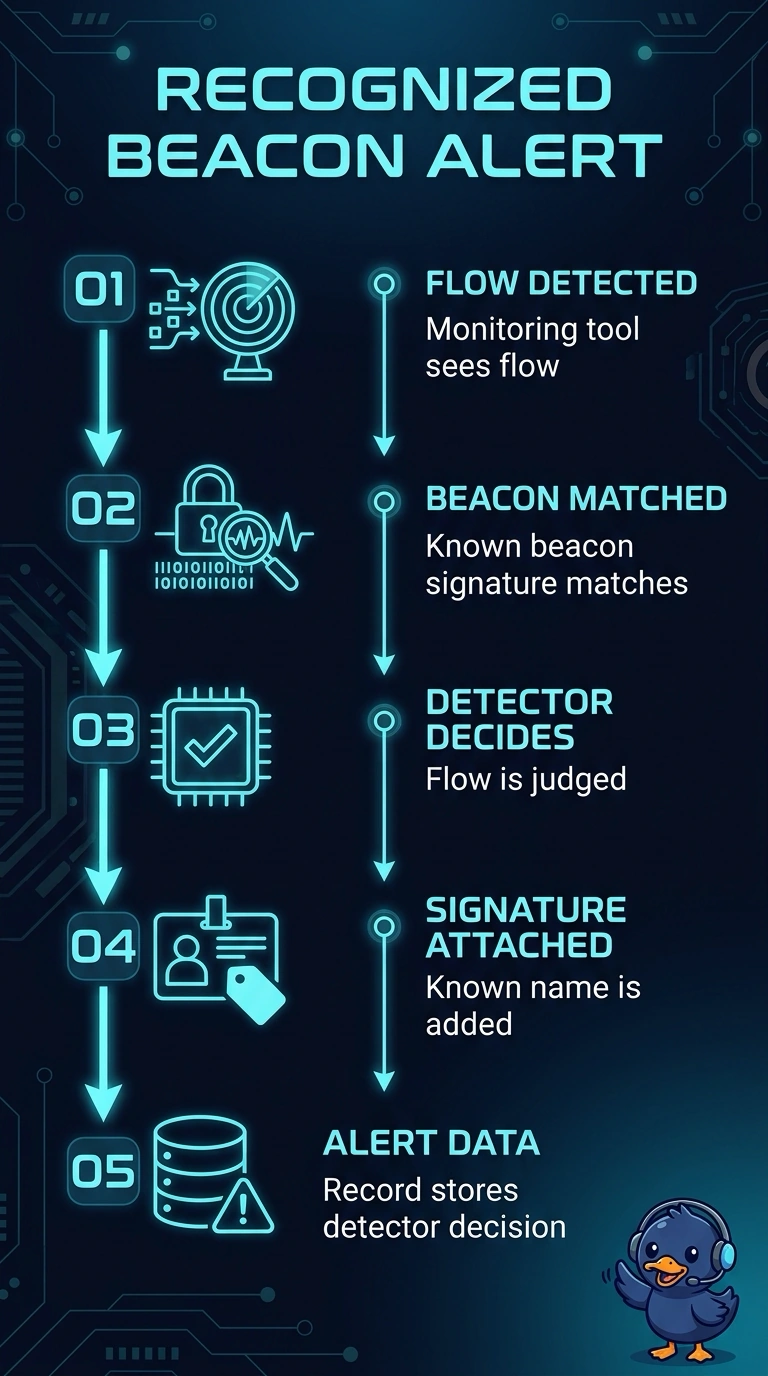
At a bank, a monitoring tool has already decided that one flow matches a known beacon and has attached a signature name to that decision. Which type of security data is this record?
Select an answer to reveal the explanation.
Short Explanation
A smoke alarm is not a floor plan of the room. You are looking at a record that already decided a flow matches a known beacon and named the signature. The trap is calling that judgment a raw count, a chart, or an owner entry.
Full Explanation
Alert data is a detector's decision, stored with the name of the match, rather than a neutral description of a conversation. The bank's tool has already decided the flow matches a known beacon and has attached a signature name, so the record is a judgment. The data type is Alert data: a detector already judged this flow and attached a known beacon signature name to it. Raw session counts and a volume chart can sit beside an alert, and they are not what this record is. Raw session counts that list who talked to whom, with no judgment recorded on the flow describe partners and volume without a verdict, and this record already carries a verdict. A statistical chart of volume over time, with no signature decision stored on the record is an aggregate picture, and the scenario describes one named detection rather than a chart. An asset inventory entry that names the workstation owner and nothing about the flow answers who owns a machine and does not record a beacon decision. Exam caveat: alert data can carry a signature name and a verdict without including the bytes that were inside the flow. Operational check: open the detection record and confirm a signature or rule name is stored with the verdict before you treat the row as a judgment.