
Leadership at a logistics hub wants to know whether tonight's outbound volume is unusual for that site. Which data type answers the question?
Select an answer to reveal the explanation.
Short Explanation
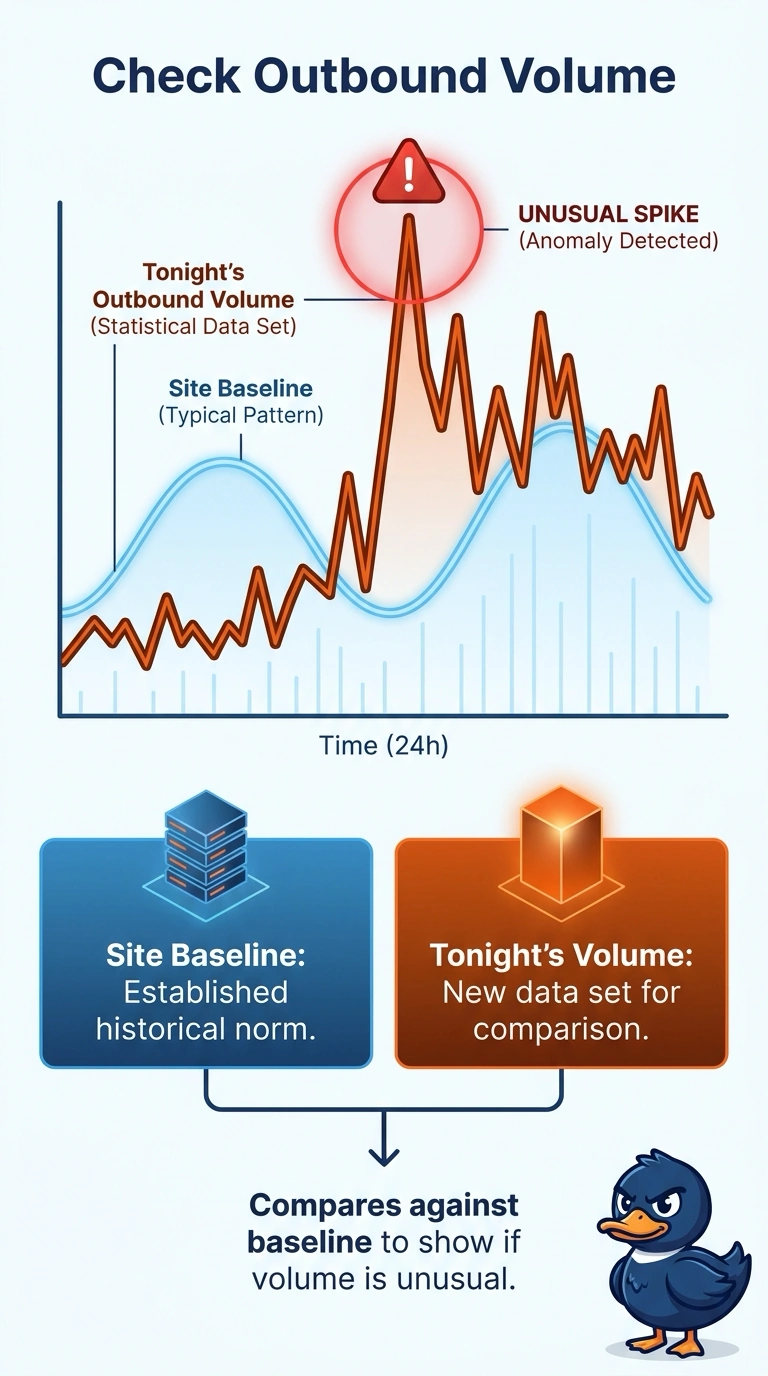
One grocery receipt cannot tell you whether the store had an unusual night. You compare the evening total with a normal evening, which is statistical data against a baseline. The trap is one packet, one firewall deny, or a certificate serial number.
Full Explanation
Judging whether a site's outbound volume is unusual requires totals compared with that site's normal pattern. Statistical data against a baseline is that comparison. One packet, one deny, and one certificate identifier cannot show the site's volume. "Statistical data set against the site baseline to show whether outbound volume is unusual". Comparing outbound volume with the site baseline is how you decide whether tonight is unusual. "The payload of a single outbound packet captured during the busiest minute at the hub tonight". One packet's payload is the bytes inside a single packet. Those bytes are not the site's outbound volume and cannot show a departure from normal. "A single firewall deny for one host that tried an unused port after the hub had closed". One firewall deny is a single blocked attempt. A single event does not measure whether the hub's outbound volume is unusual. "The serial number of a certificate presented by one partner gateway to the hub tonight". A certificate serial number identifies a certificate. It does not measure outbound volume at the site. Exam caveat: a single deny or a single packet can still be a lead for a different question. Neither one answers whether the site total is unusual. Operational check: compare tonight's outbound volume for this hub with the baseline the site already keeps for that period, and record the comparison without inventing a new threshold.