
At a hospital, legal staff need the contents of an unencrypted file that a workstation downloaded. Which data type should the analyst retrieve to supply those contents?
Select an answer to reveal the explanation.
Short Explanation
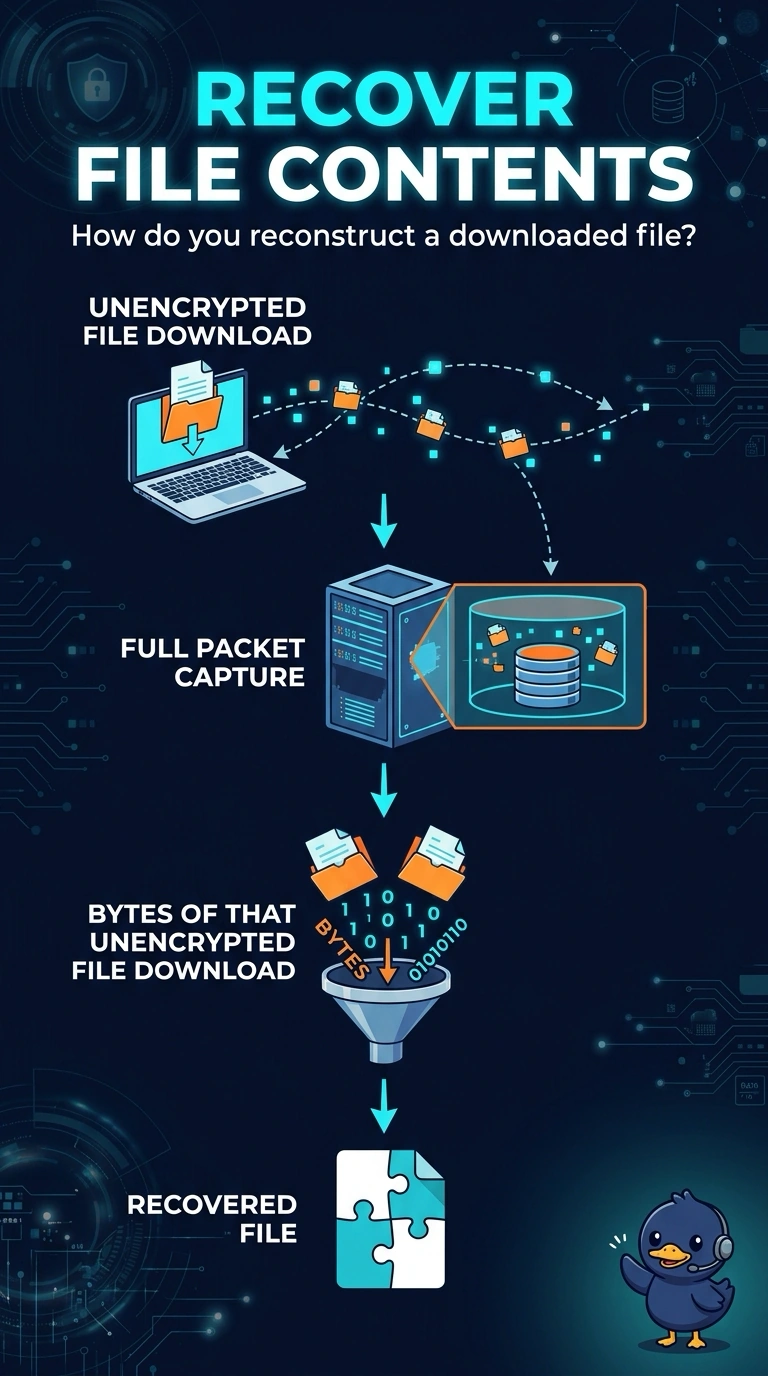
When legal asks for the document, a page count will not do, and you need the pages themselves. You pull a full packet capture of the unencrypted download. The trap is a volume baseline, an alert title, or byte totals in place of the file.
Full Explanation
Full packet capture keeps the packet bytes, including payload. For an unencrypted download, those bytes are the file legal asked to see. Summaries can describe that a transfer happened, and they do not contain the file. "Full packet capture that still holds the bytes of that unencrypted file download". The capture still holds the downloaded bytes, so the file contents can be recovered from it. "A statistical baseline that compares this hour of hospital traffic with the usual volume pattern". A baseline compares volume with a normal pattern. It has no file bytes for legal to read. "An alert name that labels the download and includes none of the transferred file bytes". An alert name is a label that a detection produced. The label is not the transferred file. "Session byte counts that record the transfer size and leave out the file contents themselves". Byte counts say how large the transfer was. The size is not the contents of the file. Exam caveat: had the download been encrypted, the same capture would hold ciphertext rather than a readable file. This request is for an unencrypted download. Operational check: reassemble the TCP stream for that transfer and confirm the file bytes are present in the capture.