
An MSSP customer wants byte counts for a conversation that ended yesterday, and nobody saved the packets. Which source can still show those counts?
Select an answer to reveal the explanation.
Short Explanation
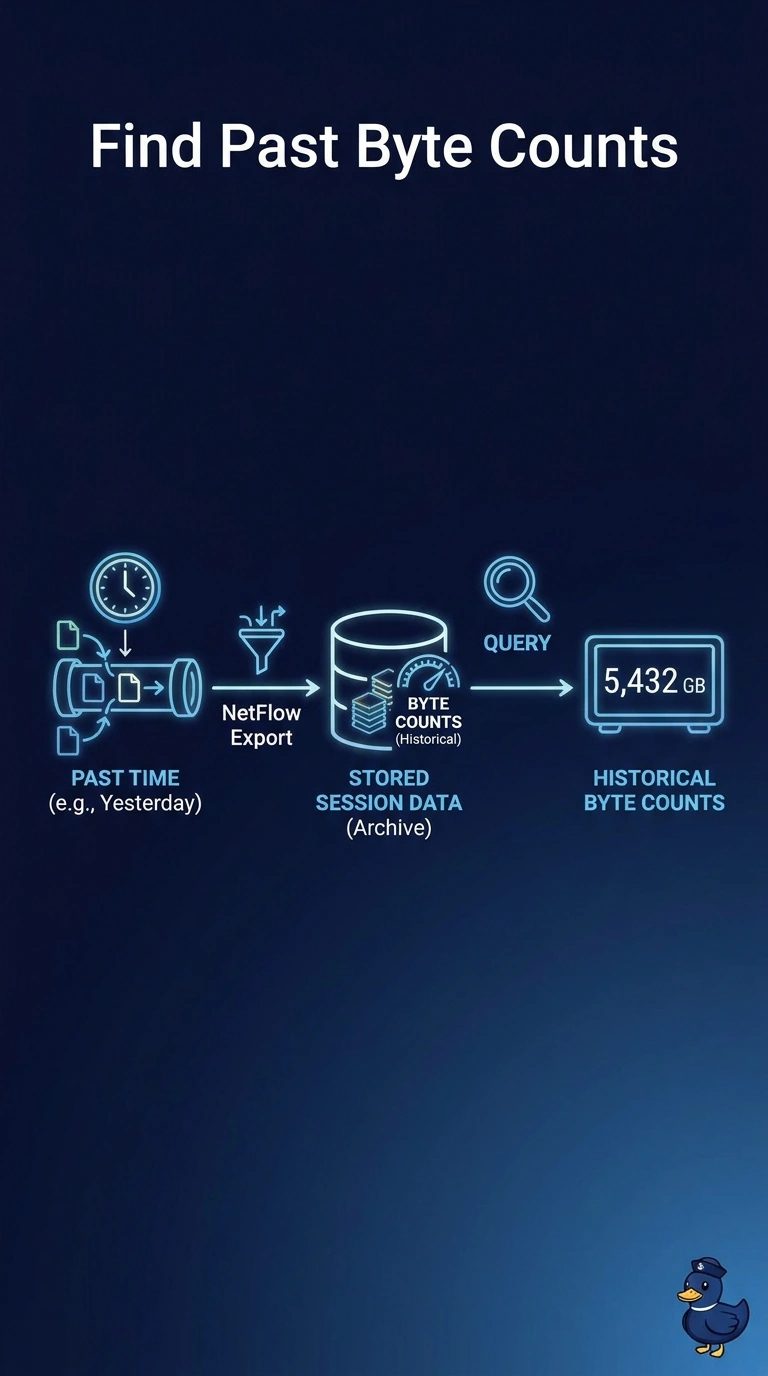
The booth can still report yesterday's count after the camera was never loaded. Byte counts for a finished conversation live in NetFlow or session data that was exported at the time, which is what you still have. A capture that was not started, a web filter on a non-web flow, or a file hash will not show those counts.
Full Explanation
Session data is the conversation summary exported while the flow exists: the 5-tuple plus counters such as bytes and packets. Once that record is exported, it remains after the packets themselves are gone. Nobody saved a packet capture yesterday, so the surviving byte counts are in the flow export. NetFlow or other session data exported at the time and still holding those byte counts. A capture that was not running has no file to reopen. A tcpdump capture nobody started, so no packet file remains for that finished conversation cannot be reconstructed after the fact. A web policy does not cover this flow. A web-content category produced for a conversation that was not web traffic to begin with would not have been generated for a non-web conversation, and a category is not a byte count. A file fingerprint measures a file, not a flow. An endpoint file hash collected from a customer PC and unrelated to the conversation size identifies bytes of a binary on a host and says nothing about how many bytes the conversation moved. Exam caveat: flow or session data helps only when export was already running at the time of the conversation. It stores the summary, not the payload, which is why it can outlast a capture nobody started. Operational check: pull the flow record for that 5-tuple, read the byte counter, and note that no packet file exists for the same interval.