
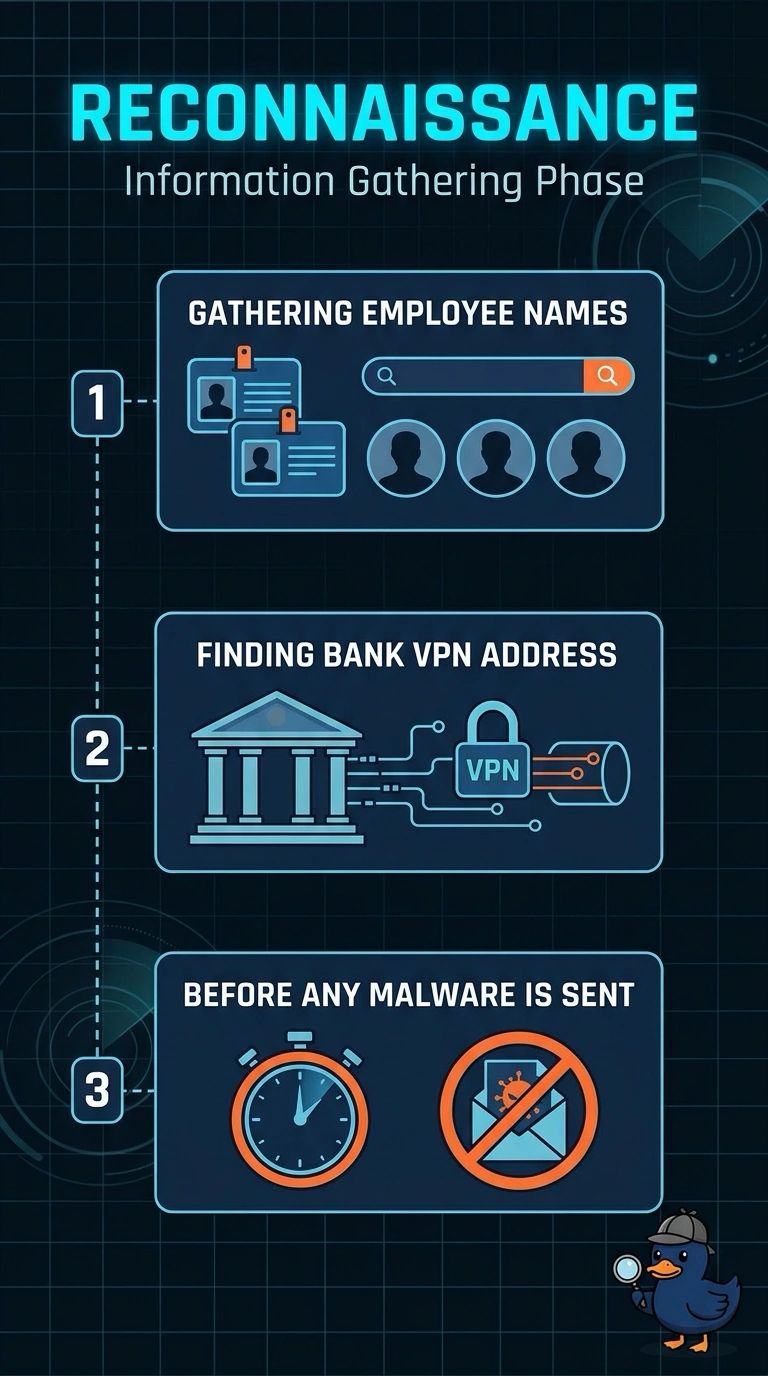
A crew is researching employee names and a bank VPN address, and no malware has been sent. Which Lockheed Kill Chain phase fits this activity?
Select an answer to reveal the explanation.
Short Explanation
Walking the outside of the bank and writing down the door codes is not the same as moving in. You are still in reconnaissance: names and the VPN address, with no malware sent. The trap is jumping ahead to installation, command and control, or actions on objectives.
Full Explanation
The Lockheed Kill Chain starts with reconnaissance: learning about the target before a payload is sent. The crew is collecting employee names and the bank VPN address, and no malware has been sent. That activity is "Reconnaissance, gathering employee names and the VPN address before any malware is sent". Installation is planting malware so it remains on a host. Nothing has been placed on a bank system, so "Installation, the point where malware is planted on a bank system and left to survive" is later than this work. Command and control is a channel from malware that is already installed. There is no such call-out here, so "Command and control, the point where installed malware calls back for tasking from the crew" fails. Actions on objectives is the theft or the change the crew came to make. Names and an address are not that outcome, so "Actions on objectives, the point where the crew copies bank data or changes bank systems" fails. Exam caveat: reconnaissance can continue after later phases in a live incident, but with no malware sent this activity is still the recon phase. Operational check: record the names and the VPN address as targeting data and watch for a later delivery instead of isolating a host that has not been touched.