
Malware is already on an agency host, it calls out for tasks, and it has not yet copied files. Which Lockheed Kill Chain phase fits this activity?
Select an answer to reveal the explanation.
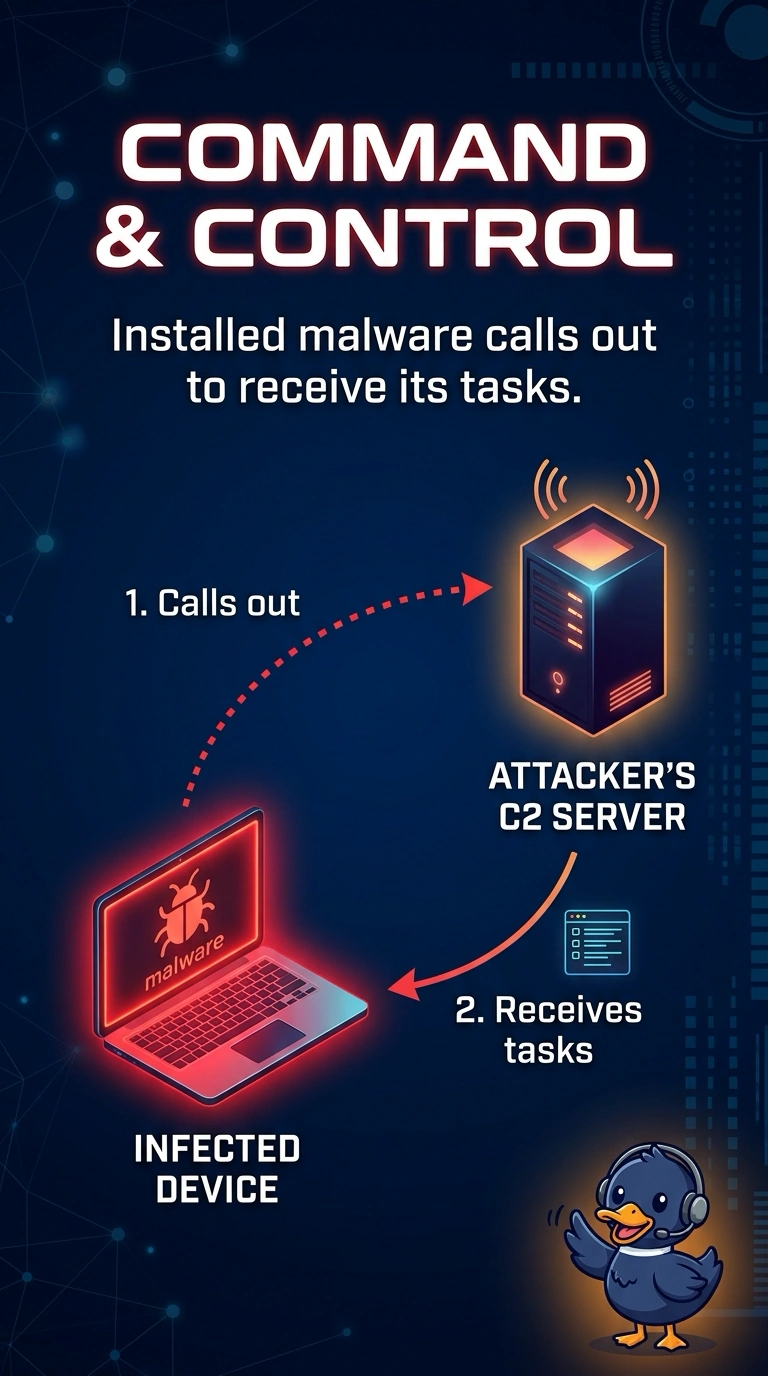
Short Explanation
The burglar is already inside and is on the phone for instructions, but the safe is still closed. You are in command and control: the malware calls out for tasks and has not copied the files yet. The trap is stepping back to weaponization or reconnaissance, or naming a Diamond victim corner as if it were a phase.
Full Explanation
The malware is already on the agency host and is calling out for tasks. In the Lockheed Kill Chain, that call-out is command and control. The files have not been copied yet, and the phase in front of the analyst is still the tasking channel. The phase is "Command and control, the step where installed malware calls out to receive its tasks". Weaponization is building the payload before it is sent. That work is earlier than a call-out from an installed host, so "Weaponization, the earlier step where the payload was built before it reached this host" fails. Reconnaissance is collecting names, addresses, and exposed services. The host is already infected and calling out, so "Reconnaissance, the step where the crew only collected names, addresses, and exposed services" fails. The Diamond Model has a victim corner for who was hit. That corner is not a Kill Chain phase name, so "The Diamond Model victim corner, offered here as if it were the name of a Kill Chain phase" fails. Exam caveat: do not rename this call-out with a Diamond corner; the Kill Chain name for installed malware requesting tasks is command and control. Operational check: record the outbound tasking channel, including its destination and port, and keep the question of copied files separate until a transfer appears.