
At a logistics hub, a record lists byte and packet counts for one 5-tuple and includes no payload and no security verdict. Which source produces a record with that shape?
Select an answer to reveal the explanation.
Short Explanation
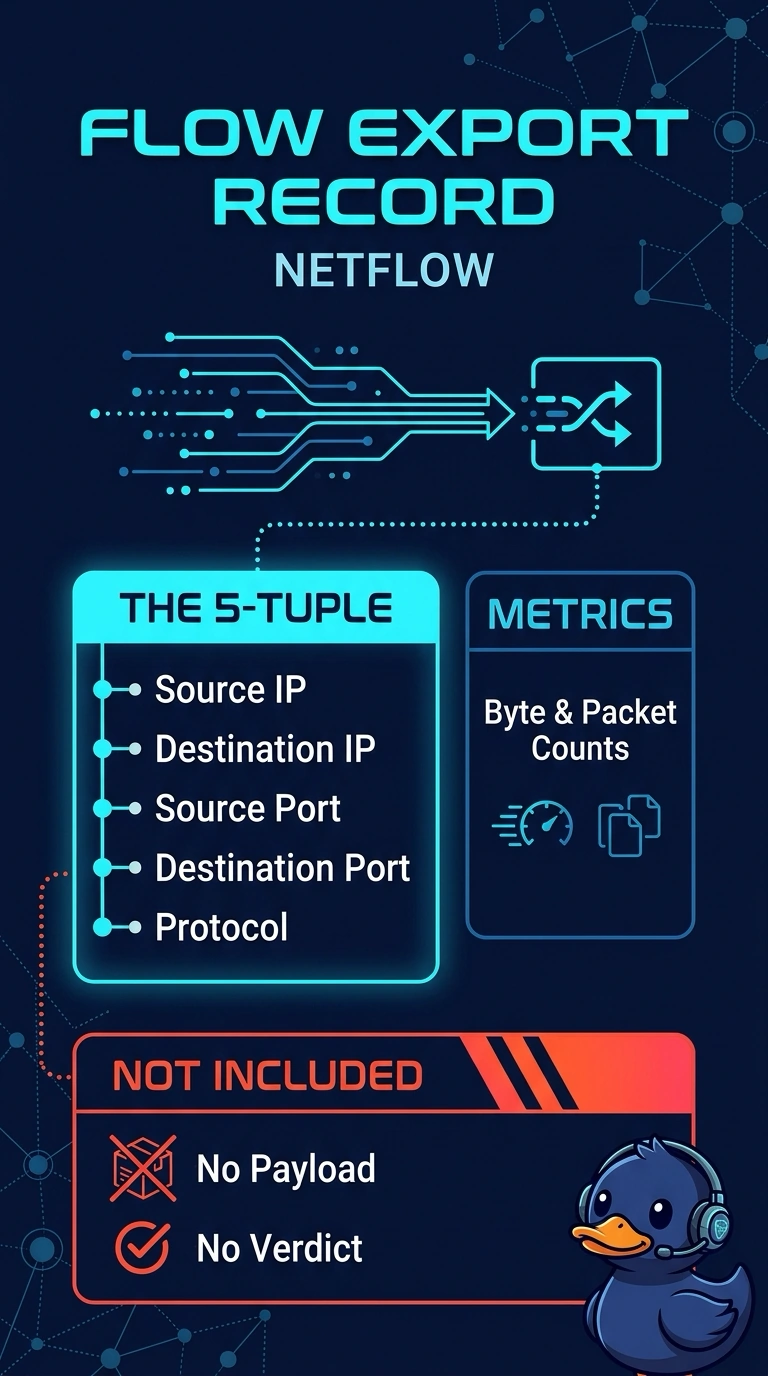
A turnstile totals how many people passed and stays silent about the conversation. Byte and packet counts on a 5-tuple, with no payload and no verdict, are that kind of summary, so you are looking at NetFlow or similar flow data. An intrusion alert, a proxy URL, or a quarantine event would have carried a judgment or a file.
Full Explanation
A 5-tuple is the source IP, destination IP, source port, destination port, and protocol. Flow export adds counters such as packets and bytes for that conversation and stops there. It does not store the payload and it does not attach an attack verdict. The hub record is that summary. NetFlow or similar flow export showing byte and packet counts for the 5-tuple, with no payload and no verdict. An intrusion sensor would have named a detection. An IPS alert that names a matching signature and a block or drop verdict for that conversation contains a judgment this record explicitly lacks. A proxy would have kept the request target. A proxy log that records the full requested URL and the user identity behind the connection is application-request logging, not a bare counter. Endpoint protection would have named a file action. An antivirus quarantine event that names the malicious file removed from a hub workstation is a host disposition, and nothing in this record identifies a file or a quarantine. Exam caveat: some flow exports can be extended, but a line that is only counts for a 5-tuple, with no payload and no verdict, is still flow data. If you need a signature, a URL, or a quarantined filename, you need one of the other sources. Operational check: confirm the record exposes packet and byte counters and that the signature ID, URL, and filename fields are absent before you treat it as flow data.