
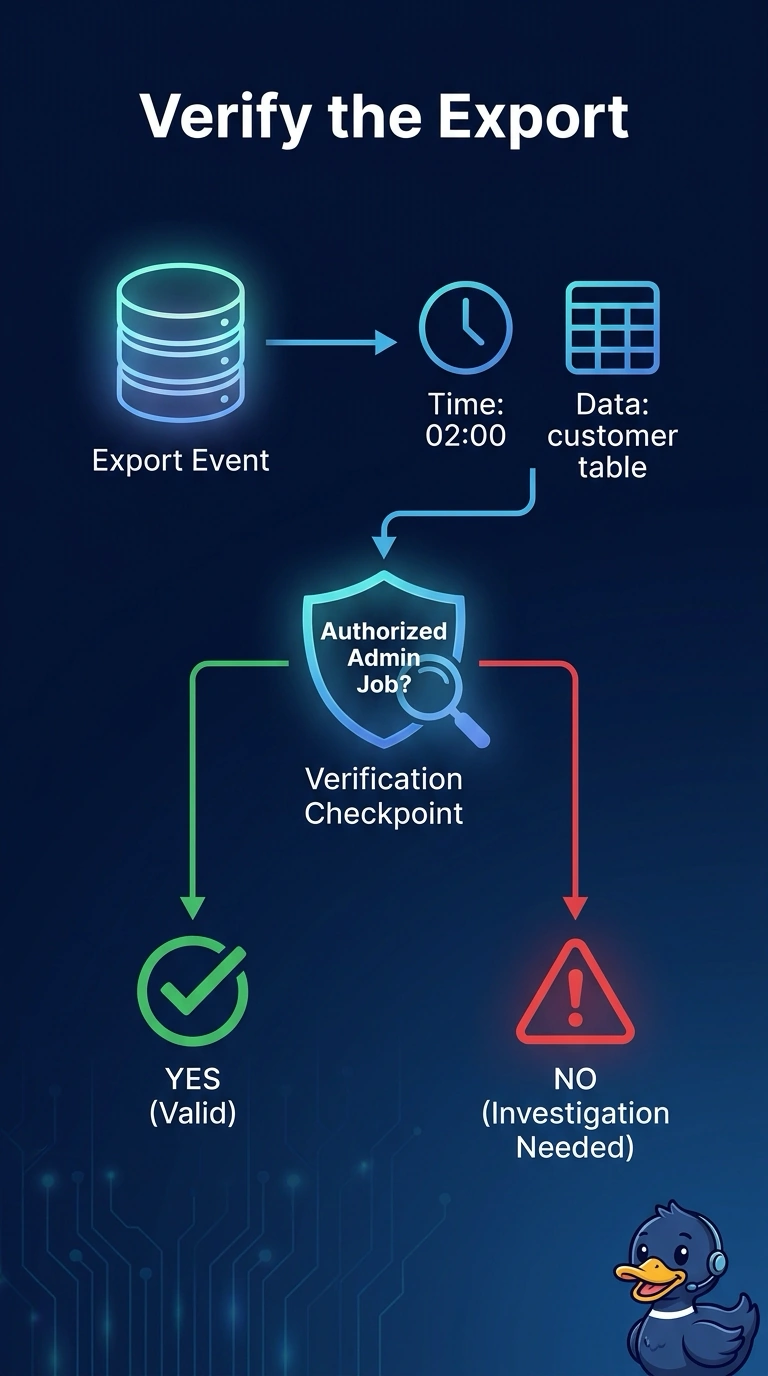
At a manufacturer, an application log records an administrator export of the customer table at 02:00 from a workstation that has no night shift. What should the analyst do first?
Select an answer to reveal the explanation.
Short Explanation
The oven timer at two in the morning might be the baker's normal shift, so you ask before you throw out the dough. You confirm whether the customer-table export was an authorized job. The trap is wiping the workstation, ignoring an application log, or calling it a VPN outage.
Full Explanation
The right selection is "Confirm whether the 02:00 export of the customer table was an authorized administrative job". An application log can record a real export, the hour is only a lead, and scheduled jobs often run at night. Until you know the export was unauthorized, wiping or relabeling the event is the wrong move. The statement "Wipe the workstation at once so nobody can repeat the customer-table export from it" destroys workstation context before anyone has checked whether the job was approved. The statement "Ignore the entry on the grounds that an application log cannot record a real customer export" throws away a record that is specifically about a data export. The statement "Treat the entry as a VPN outage and hand it only to the team that runs remote access" invents a remote-access failure the log line does not describe. Exam caveat: an odd hour is not proof of theft, and an export that is confirmed unauthorized can move to containment after that check. Operational check: compare the export with the change calendar and with that administrator's approved jobs before the workstation is isolated.