
An integration lead asks whether IRM needs its own separate user directory product for GRC personas. What is the correct technical answer?
Select an answer to reveal the explanation.
Short Explanation
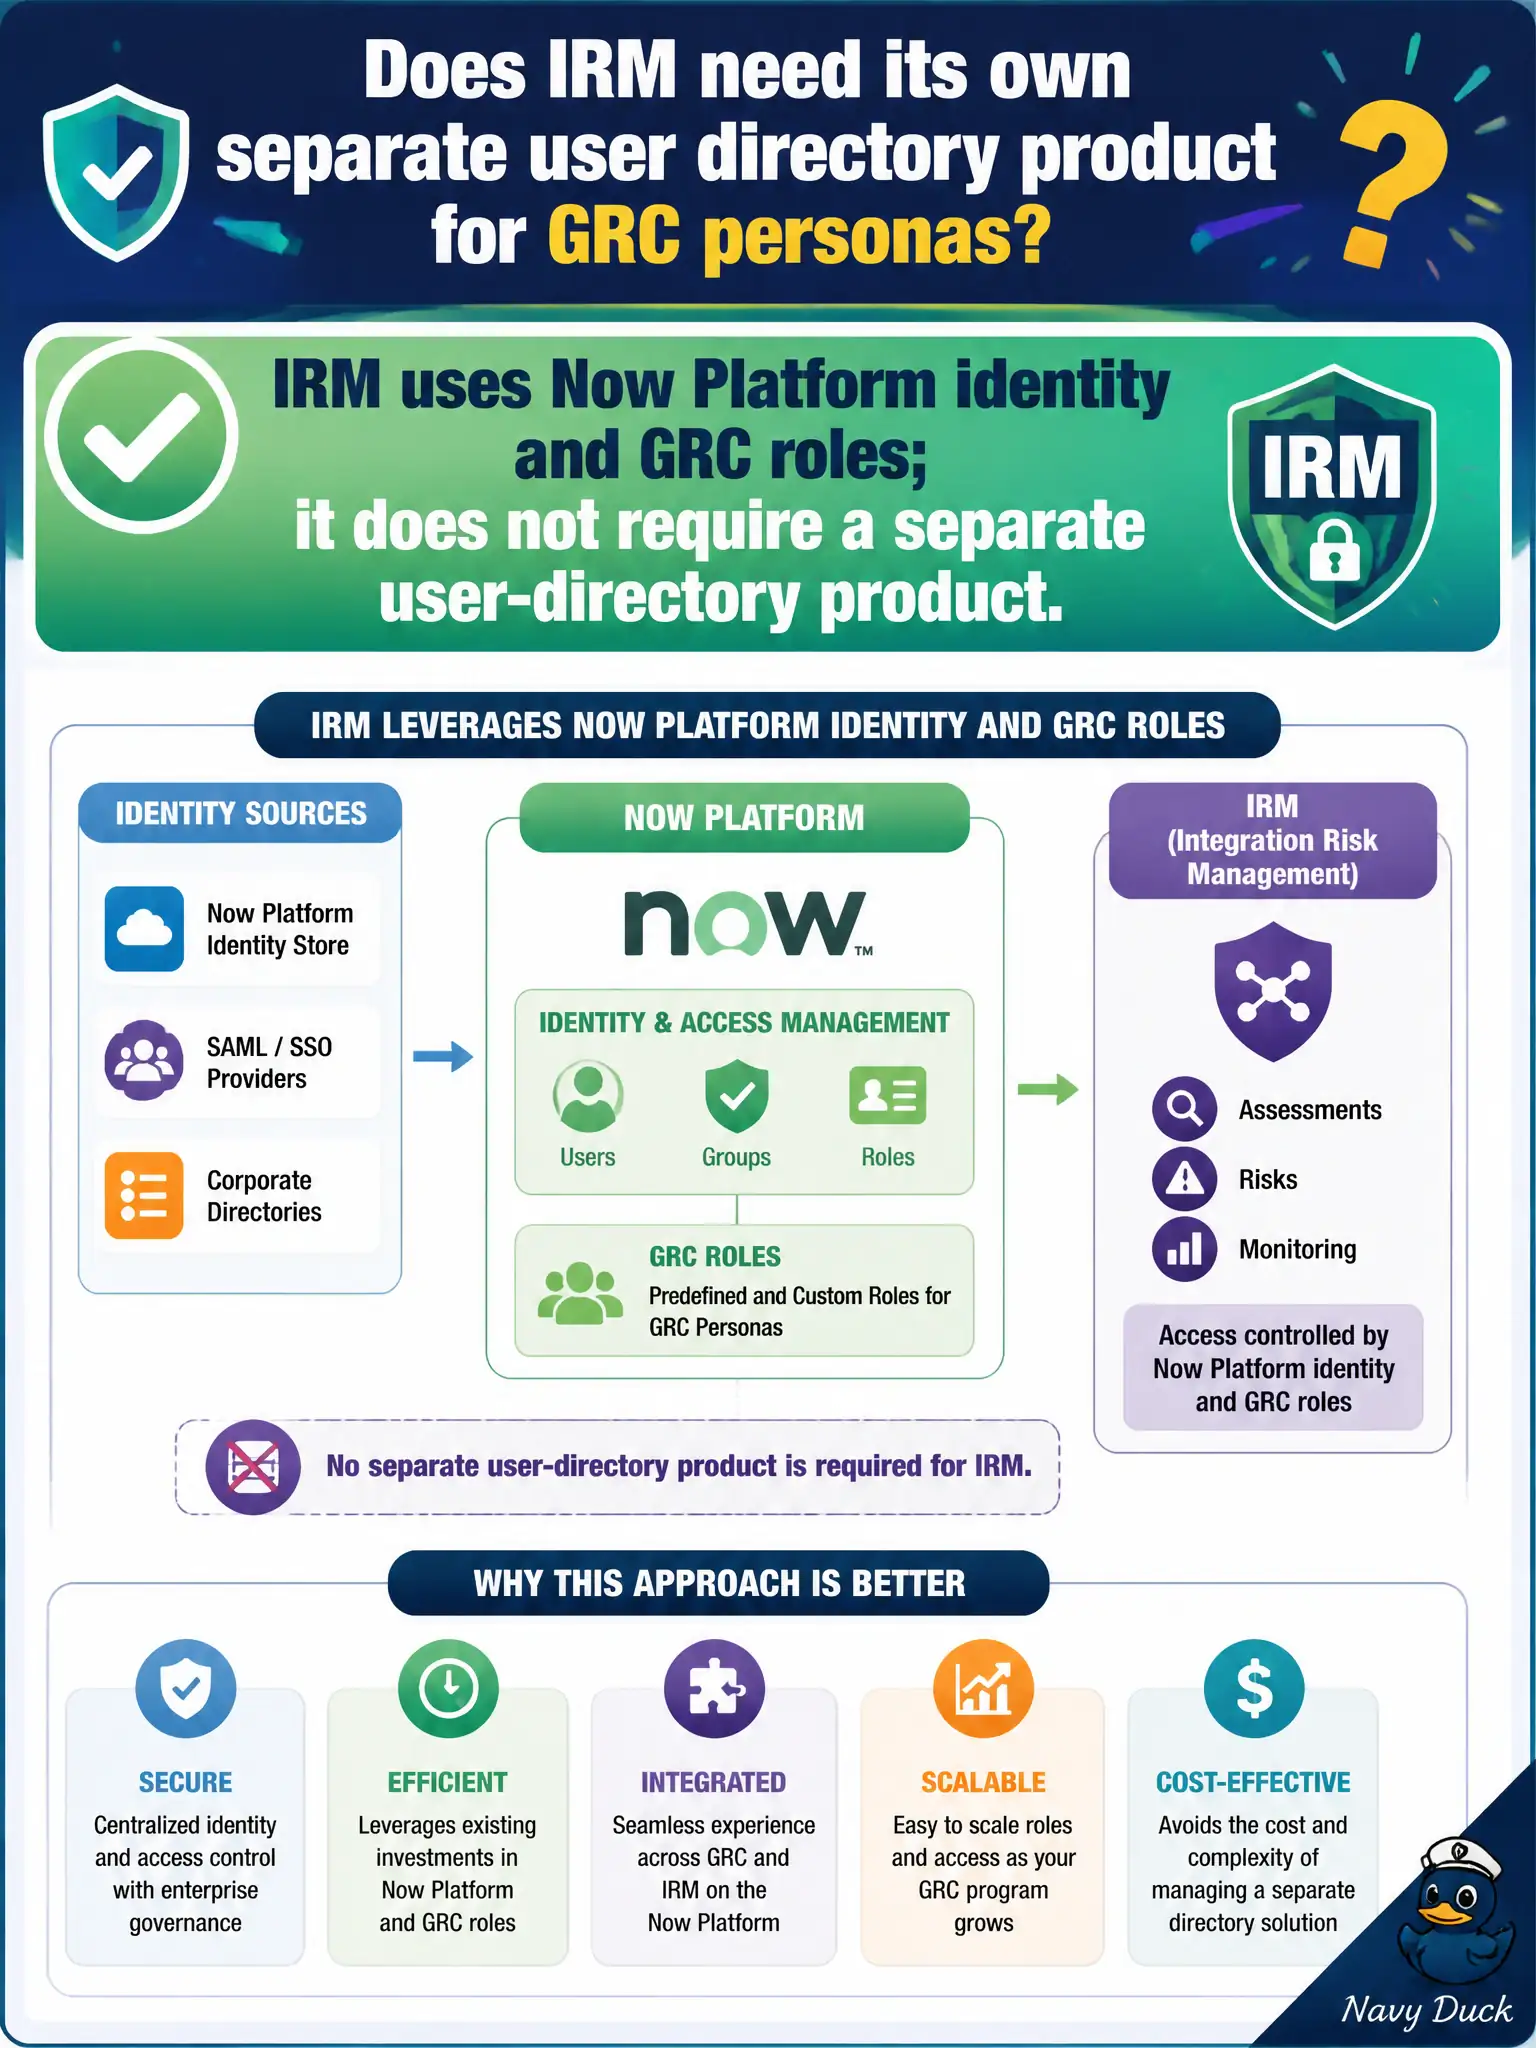
IRM does not ship its own mystery phone book. People and roles come from the same Now Platform identity you already use, plus GRC-specific roles for personas. No need for a second directory island just because compliance went live.
Full Explanation
IRM uses Now Platform identity and GRC roles; it does not require a separate user-directory product for GRC personas. People, groups, and authentication remain platform concerns that cities already operate through their IdP and user administration practices. IRM adds role-based access for risk, compliance, and audit work so the same employees can own entities and complete attestations without a second account island. Inventing a parallel directory increases cost, reconciliation errors, and access reviews without improving GRC outcomes. Mandating a dedicated LDAP forest that cannot sync with platform users invents isolation and operational pain. Requiring all GRC users to authenticate only through a CIS-HR employee portal incorrectly makes HRSD the sole identity path for Risk and Compliance. Insisting entity owners must be external vendor accounts managed solely in TPRM misplaces ownership for internal civic entities and applications. Exam caveat: identity is platform-native plus GRC roles—not a new directory SKU or sibling-product mandate on CIS-RC. Operational check for the integration lead: map policy owner, control owner, risk manager, and audit manager personas to platform groups and GRC roles in a RACI, verify login with existing IdP users in subprod, and confirm no parallel GRC-only directory appears in the design.