
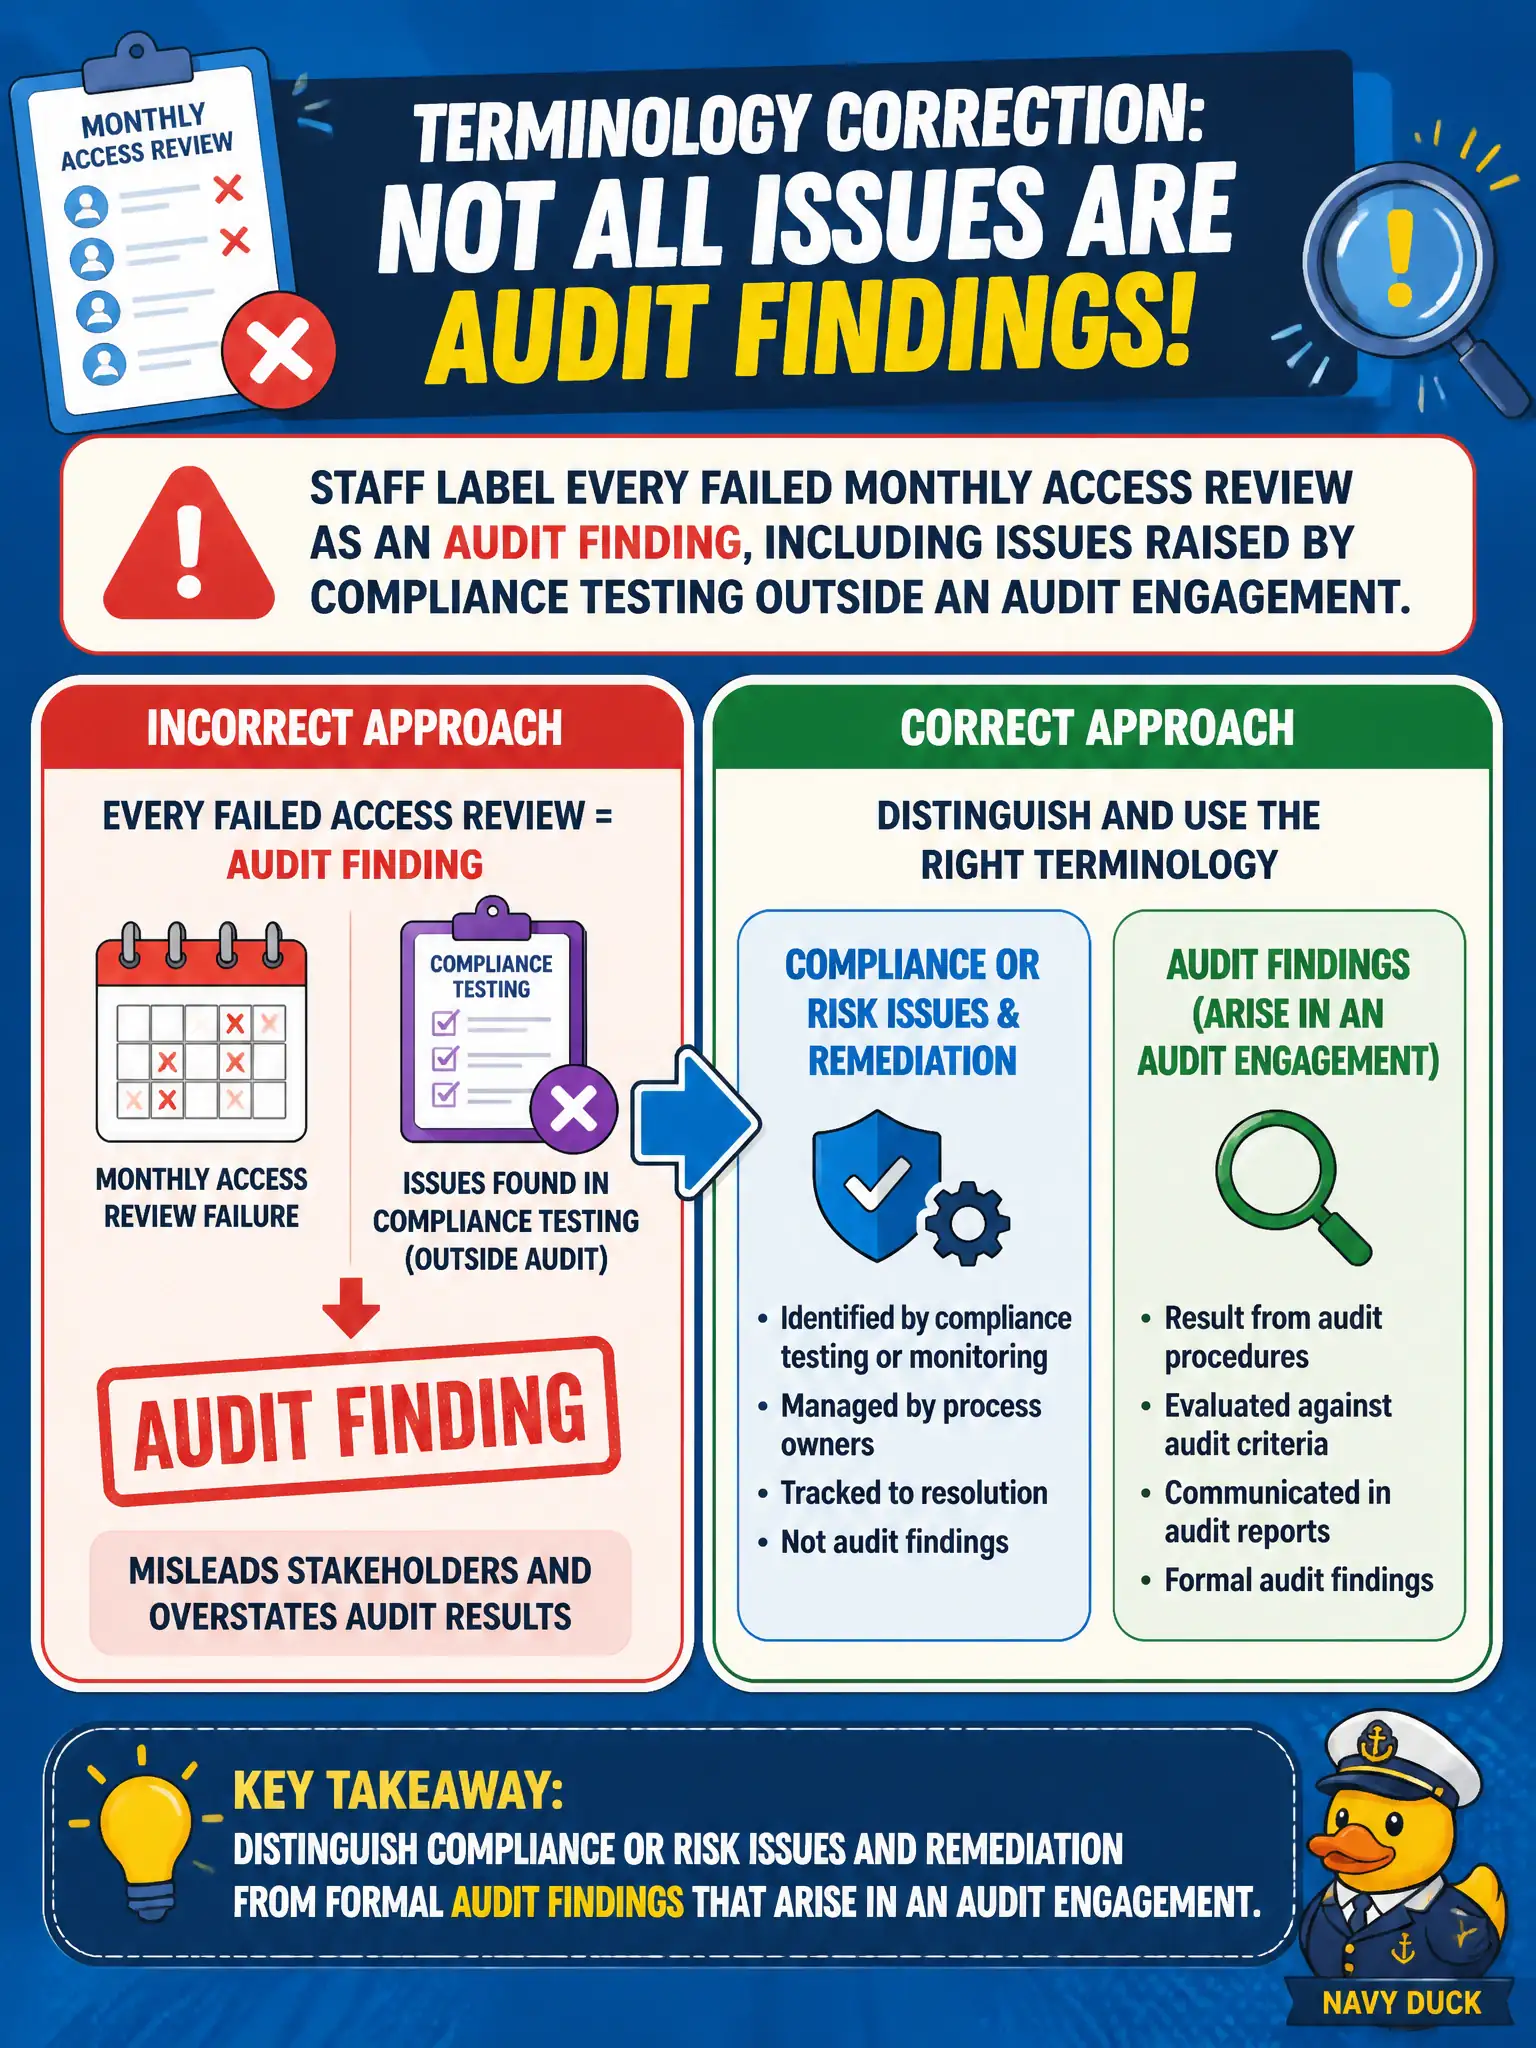
Staff label every failed monthly access review as an audit finding, including issues raised by compliance testing outside an audit engagement. What terminology correction is needed?
Select an answer to reveal the explanation.
Short Explanation
Not every red flag is an auditor’s stamp. Failed access reviews from compliance testing are issues to fix; audit findings are what formal assurance engagements officially raise.
Full Explanation
Failed monthly access reviews raised by compliance testing are compliance or risk issues needing remediation; they are not automatically formal audit findings. Audit findings arise from audit engagements with independent assurance characteristics. Staff who label every failed review as an audit finding overload audit language, confuse workflows, and blur lines of defense in a civic program. The needed correction is to distinguish issues and remediation from engagement-originated findings. Calling every failed control a security incident so SIR owns remediation routes control failures into the wrong product and owner model. Renaming all issues as software license exceptions under SAM substitutes entitlement handling for control remediation. Treating audit findings and indicators as the same record type collapses human or engagement outcomes with measured monitoring signals. Exam caveat: terminology depth questions separate issue, finding, and indicator concepts rather than treating every red flag as an auditor’s stamp. Operational check for the team: for one failed access review outside an engagement, create or update an IRM issue assigned to the control owner, keep audit finding records reserved for engagement work, and verify dashboards filter the two populations separately.