
After a regulatory-change record adds a new citation, who should decide whether existing controls already cover it?
Select an answer to reveal the explanation.
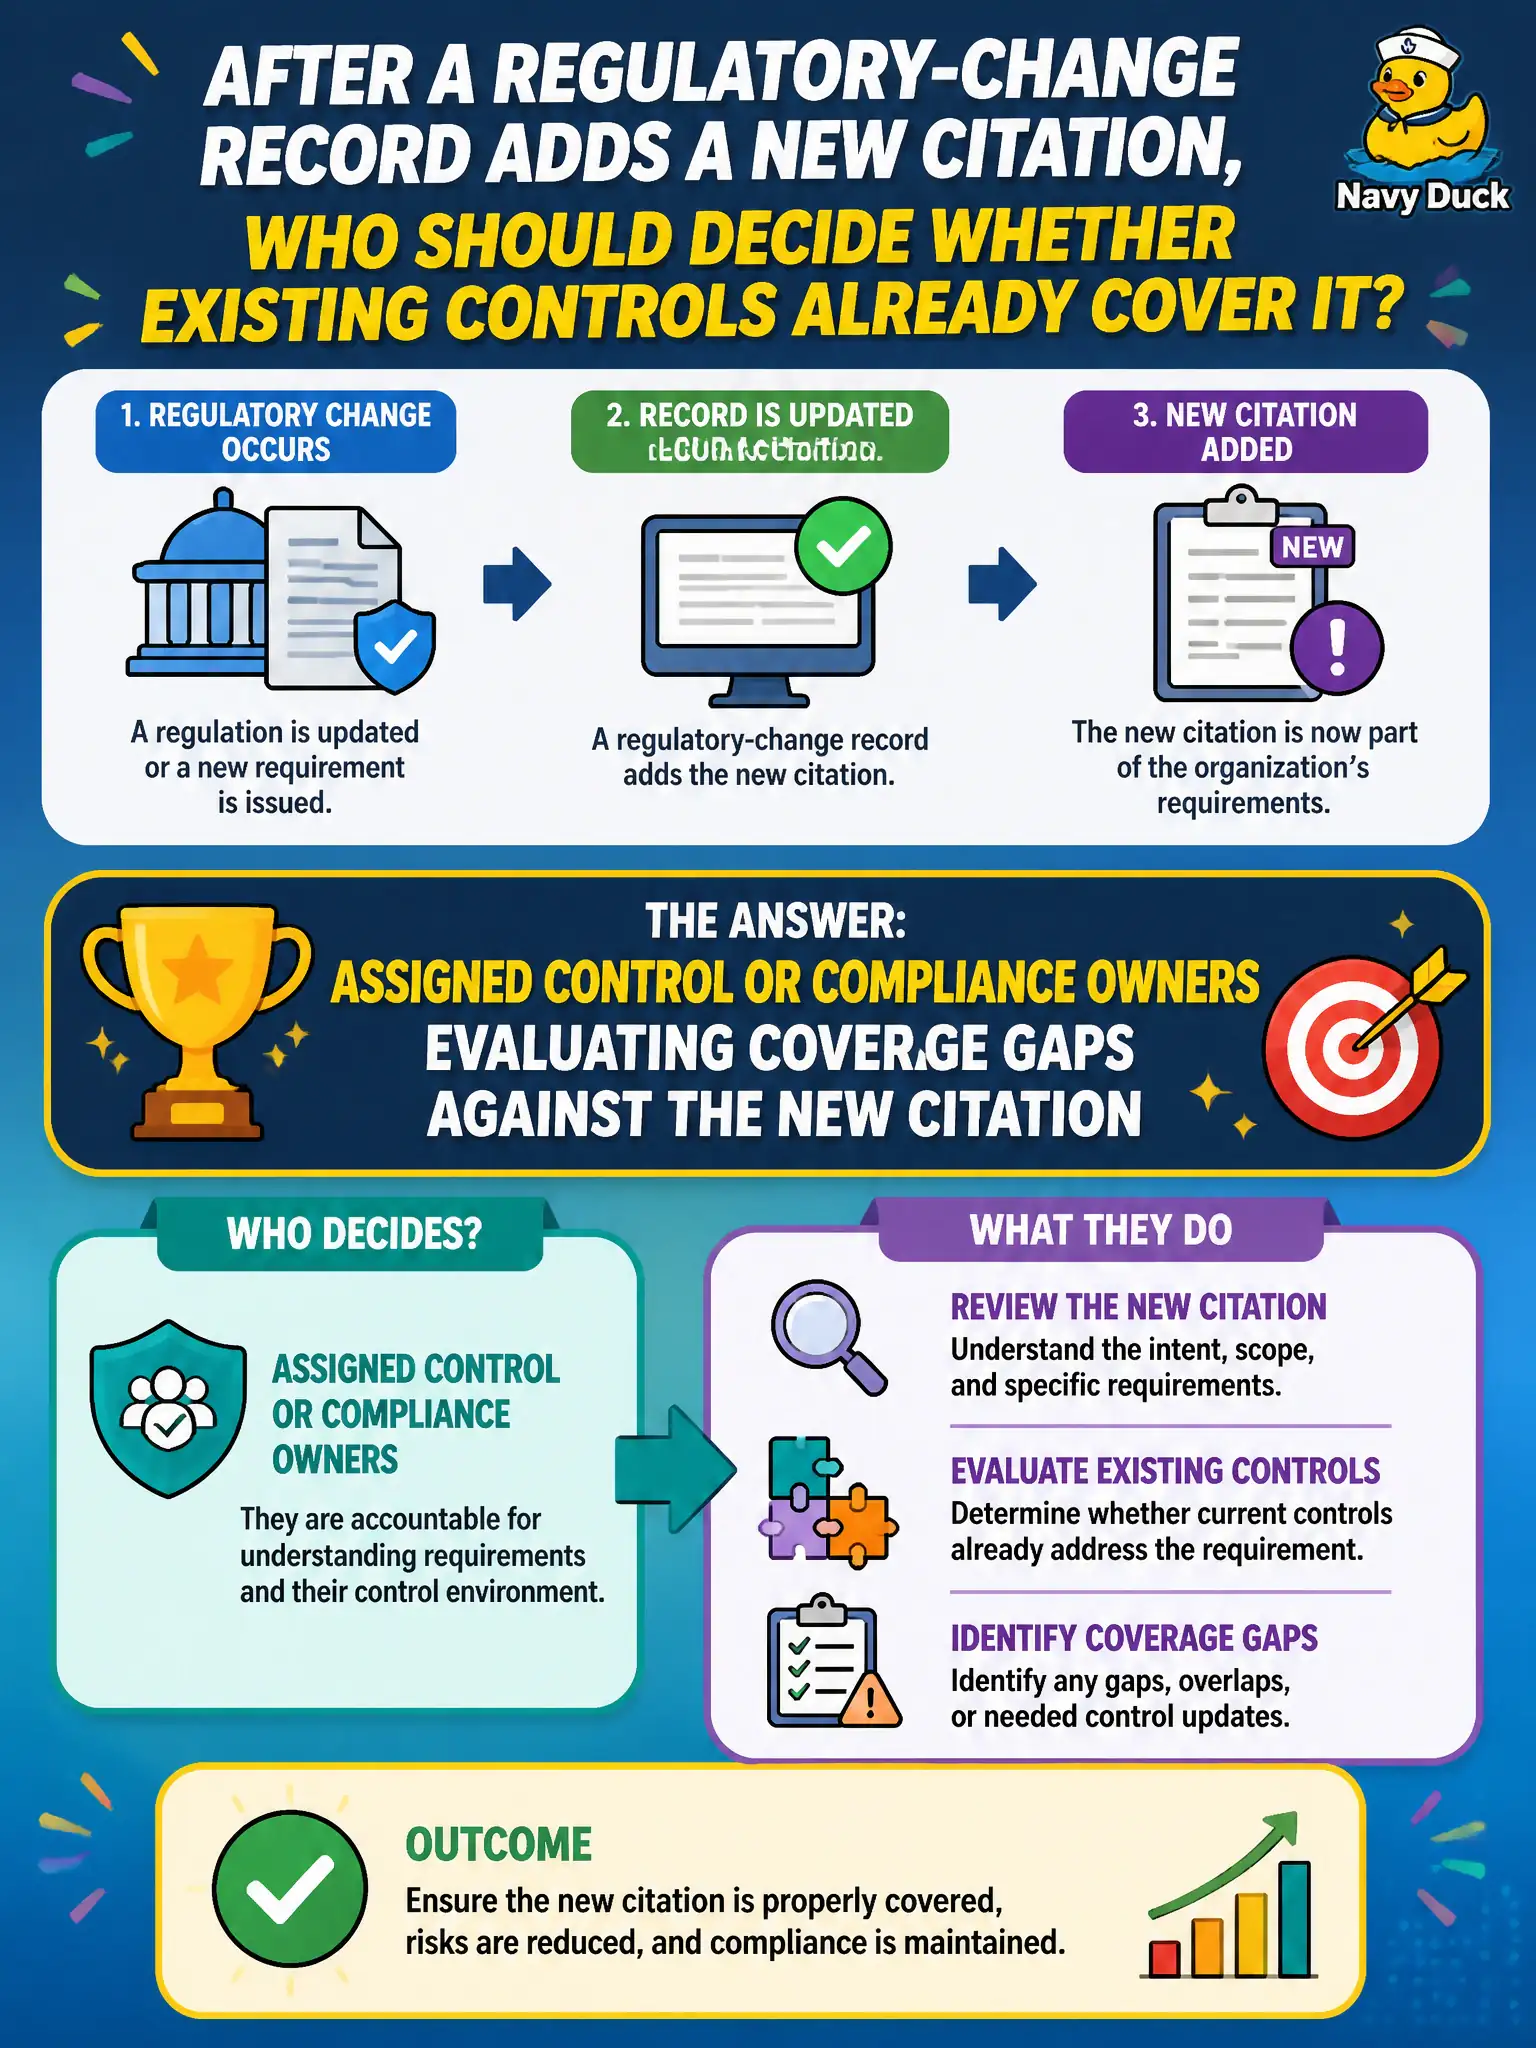
Short Explanation
Somebody named has to stare at the new rule and say 'we already cover this' or 'we don't.' Assign control/compliance owners to run that gap check. Mid-servers and license auditors aren't the right jury.
Full Explanation
After a regulatory-change record adds a new citation, assigned control or compliance owners should decide whether existing controls already cover it by evaluating coverage gaps against that citation. Named human ownership of the gap decision is required; automation and unrelated roles cannot declare privacy coverage for a county. This is the accountability step after intake.
Leaving the decision only to the CMDB discovery mid-server with no human review confuses discovery with compliance judgment. Anonymous public chatbots with no named ownership fail governance. SAM license auditors as default owners of privacy citations misassign software entitlement reviewers to privacy control coverage.
Exam caveat: control/compliance owners evaluate citation coverage gaps—not mid-servers, chatbots, or SAM auditors.
Operational check: assign owners on the new citation impact tasks; require a cover/gap decision; open issues where gaps exist; record the decision on the regulatory-change trail.
Coverage decisions should be recorded with rationale and effective date, and gaps must open IRM issues with owners—not disappear into chat. Exclude mid-server automation and SAM auditors from privacy citation ownership assignments.