
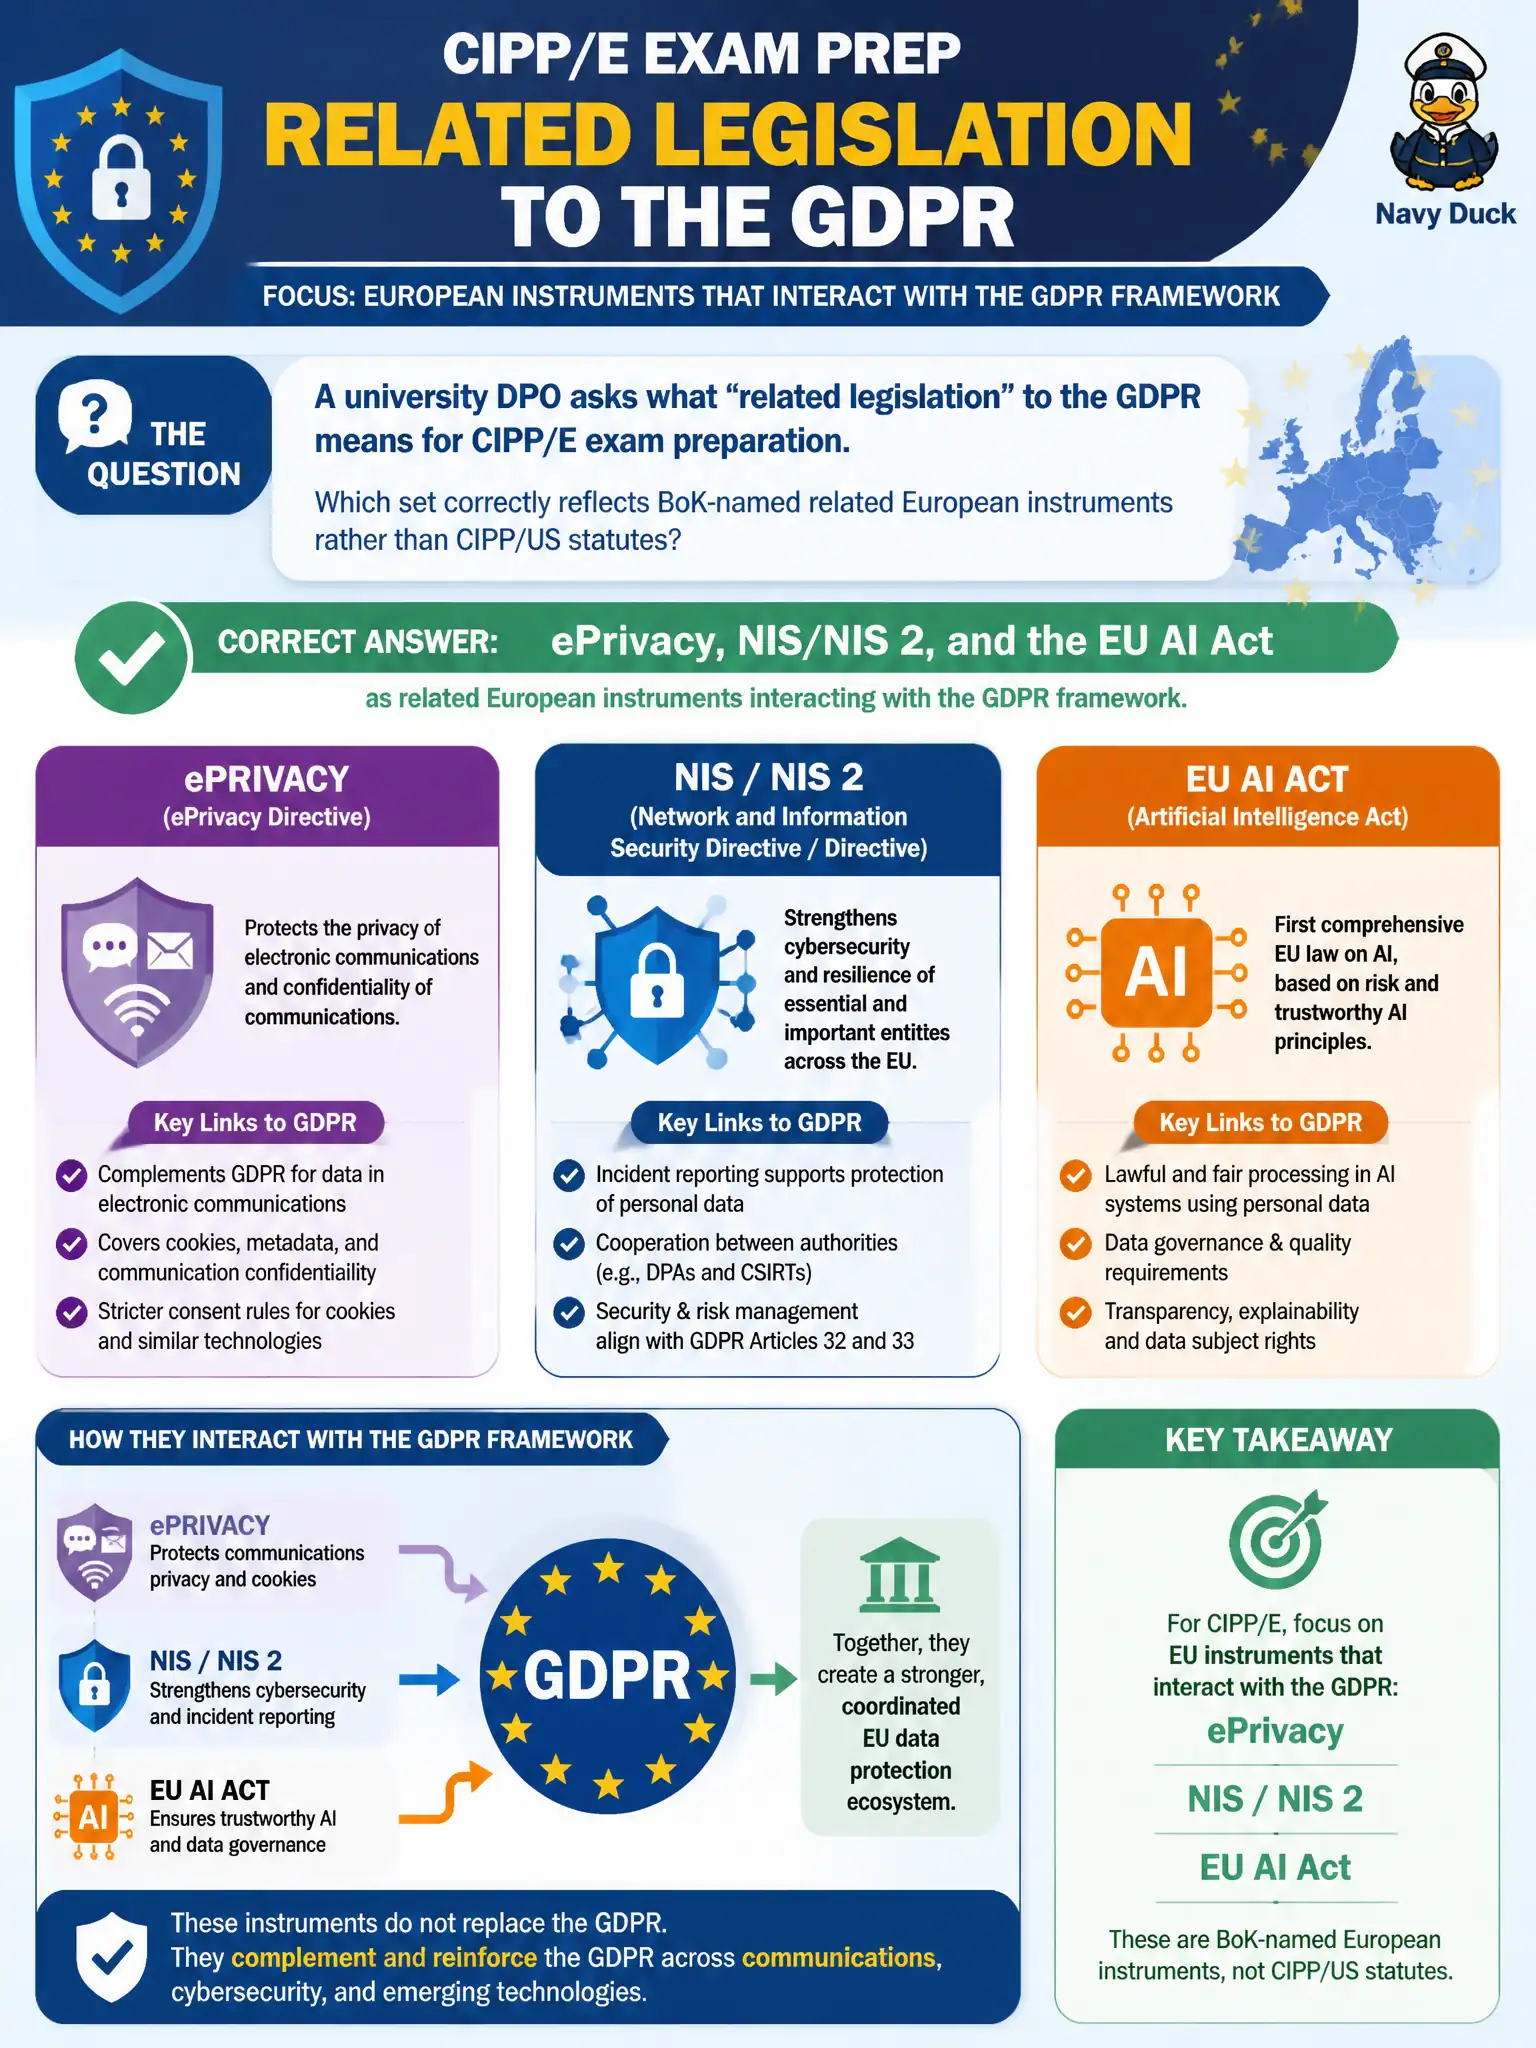
A university DPO asks what “related legislation” to the GDPR means for CIPP/E exam preparation. Which set correctly reflects BoK-named related European instruments rather than CIPP/US statutes?
Select an answer to reveal the explanation.
Short Explanation
Stay on the European shelf. Related legislation in a CIPP/E sense means things like ePrivacy, NIS/NIS 2, and the EU AI Act sitting next to the GDPR—not California CCPA, HIPAA, or FCRA from the US privacy track. Standards like ISO 27001 can help security practice, but they are not that legislative set.
Full Explanation
For CIPP/E exam preparation, “related legislation” to the GDPR means BoK-named European instruments such as ePrivacy, NIS/NIS 2, and the EU AI Act that interact with the GDPR framework—not CIPP/US statutes. University DPOs should drill that European package and resist transplanting US lists. CCPA, CPRA, and HIPAA are not the core GDPR-related European package. FCRA, GLBA, and FTC Section 5 are not mandatory Annexes to Regulation (EU) 2016/679. ISO 27001 Annex A controls are a management standard, not a substitute for those EU legislative instruments. Exam caveat: related-legislation distractors often smuggle CIPP/US statutes—reject them for CIPP/E. Operational check: rebuild the DPO training reading list so related-EU-law modules cite ePrivacy, NIS 2, and the AI Act, and move US statutes to a comparative appendix clearly labelled out of CIPP/E scope. For municipal teams, keep a one-page decision note that states the governing instrument, why competing labels fail, and what evidence would change the conclusion. Document the decision trail so auditors can see how the civic team matched facts to the correct legal category rather than to a slogan. Revisit the conclusion when facts, recipients, or processing purposes change, and record who approved the updated analysis.