
A city CISO wonders whether NIS/NIS 2 belong in a European data-protection exam conversation. Which placement is correct for CIPP/E Domain I?
Select an answer to reveal the explanation.
Short Explanation
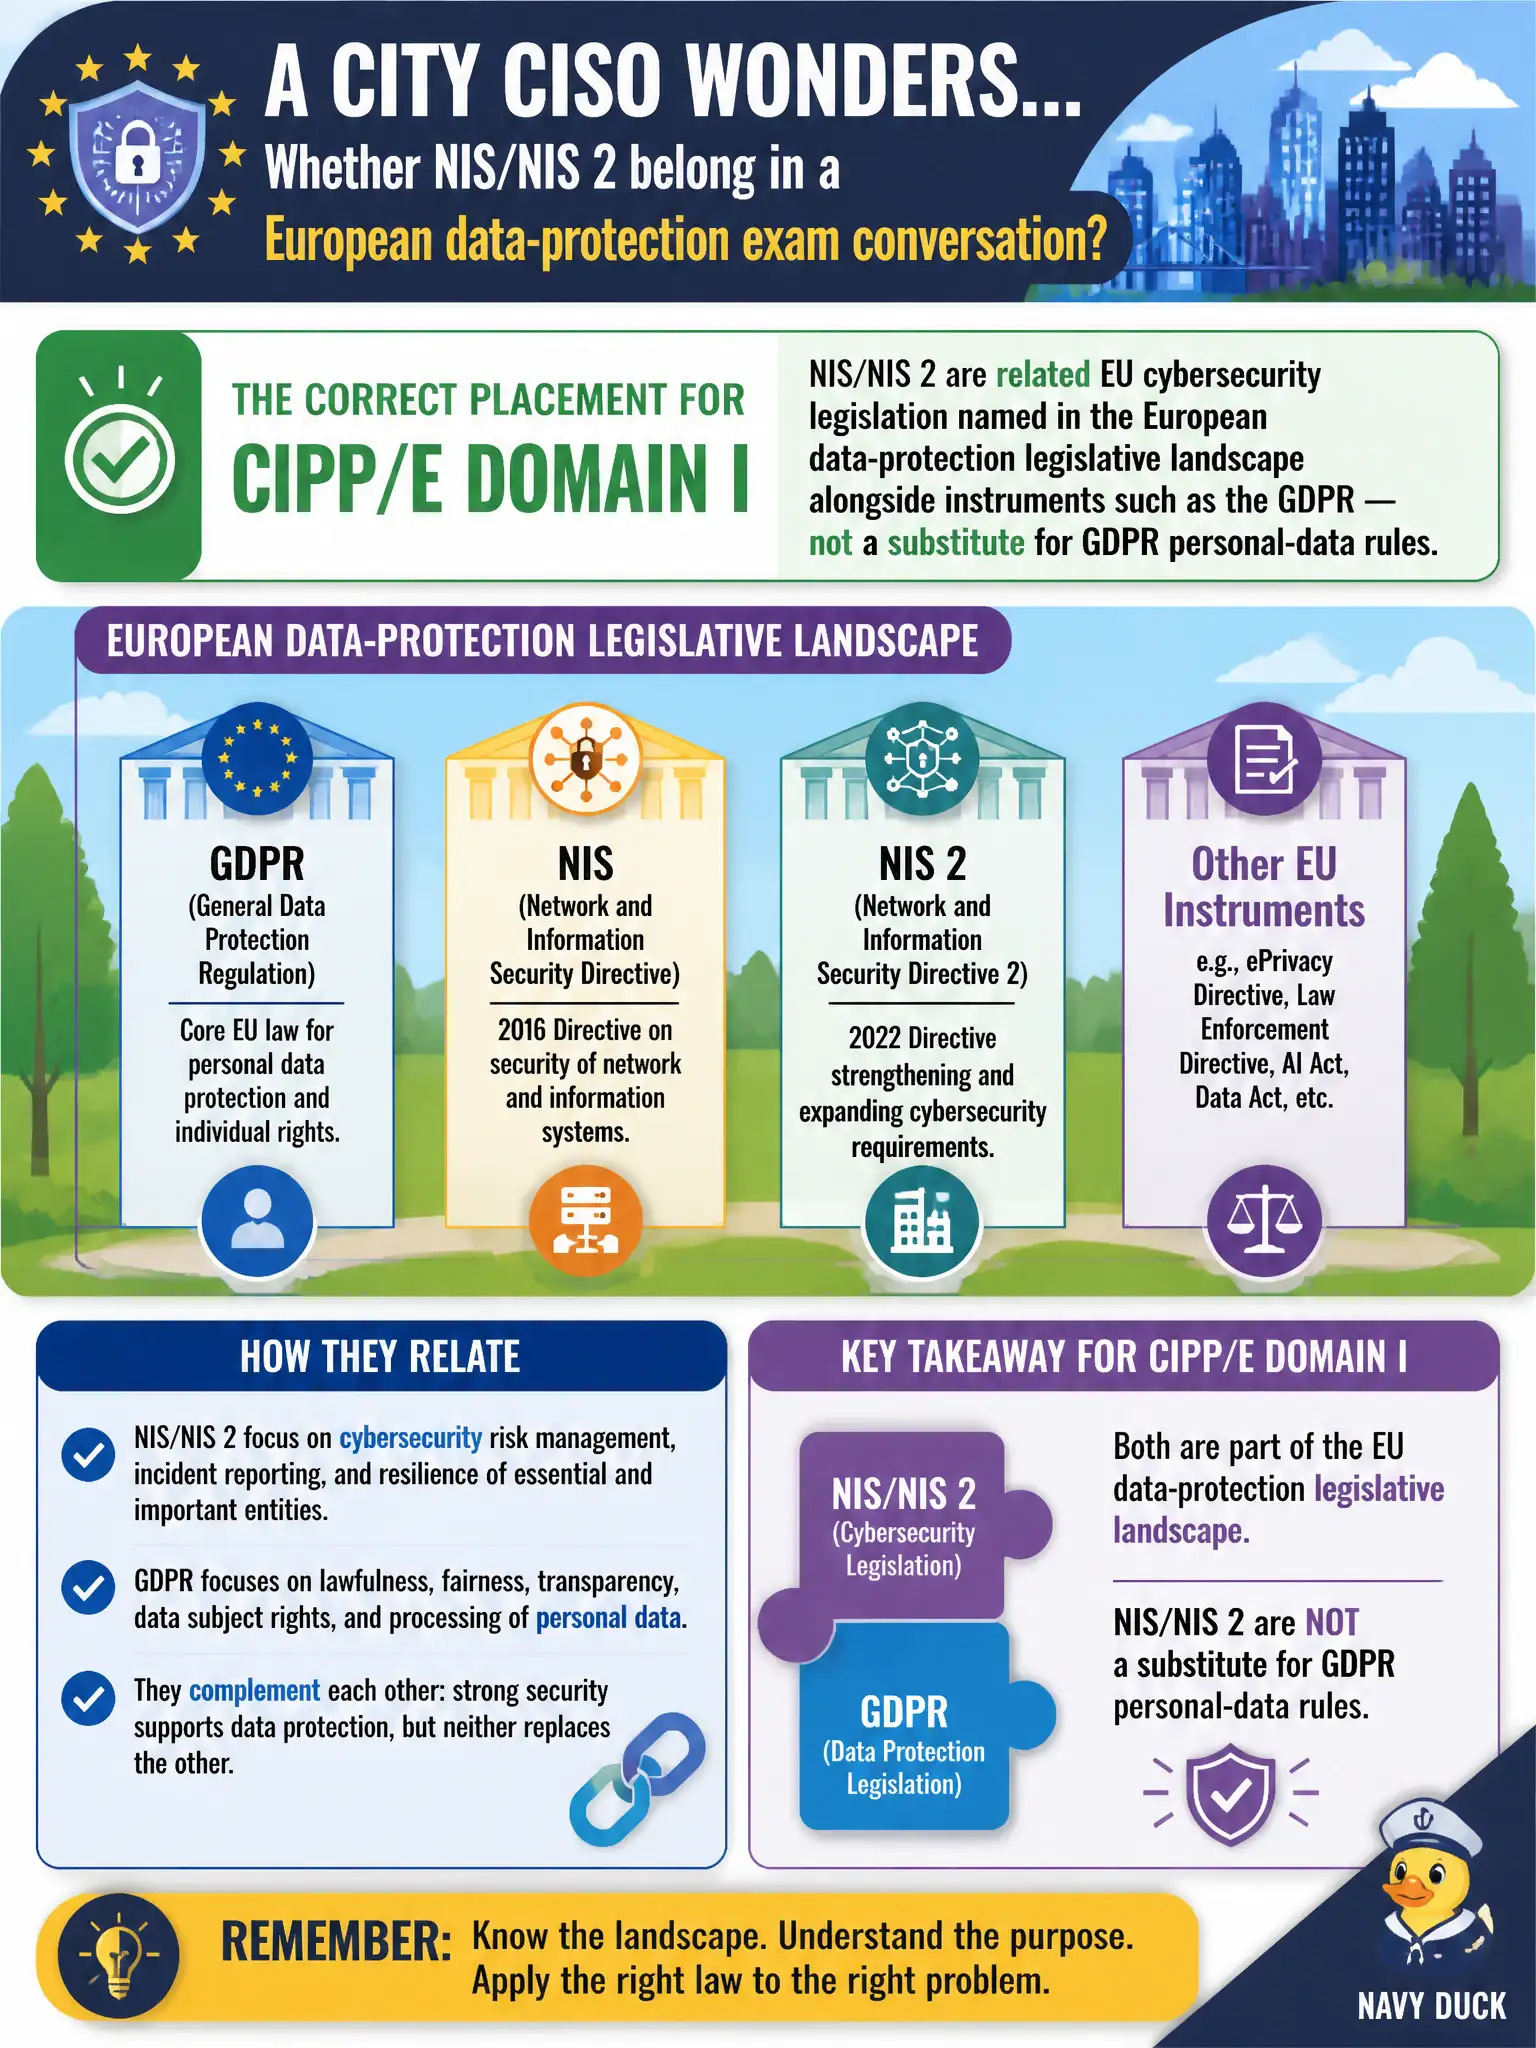
NIS and NIS 2 are the cybersecurity cousins on the same European legislative street as the GDPR — related, not identical. A privacy exam still mentions them so you know the neighbourhood. Do not swap them in as a GDPR replacement.
Full Explanation
NIS and NIS 2 are related EU cybersecurity legislation named in the European data-protection legislative landscape alongside instruments such as the GDPR; they address cybersecurity risk management and incident obligations for covered entities and are not a substitute for GDPR personal-data rules. A city CISO studying CIPP/E Domain I should place them on the related-legislation shelf: security and resilience duties can intersect breach and security themes, yet personal-data protection still turns on the GDPR. They are not purely US federal hacking statutes. They did not replace the GDPR for all personal-data breaches in 2016. They do not apply only to paper telegrams. Exam caveat: expect “related but not replacing” as the scoring pattern whenever NIS/NIS 2 appears next to GDPR. Operational check: for a municipal essential-entity incident, run parallel playbooks—NIS 2-style cyber incident duties where the entity is in scope, and GDPR personal-data breach assessment if personal data is compromised—without assuming one notice satisfies both regimes automatically. For municipal teams, keep a one-page decision note that states the governing instrument, why competing labels fail, and what evidence would change the conclusion.