
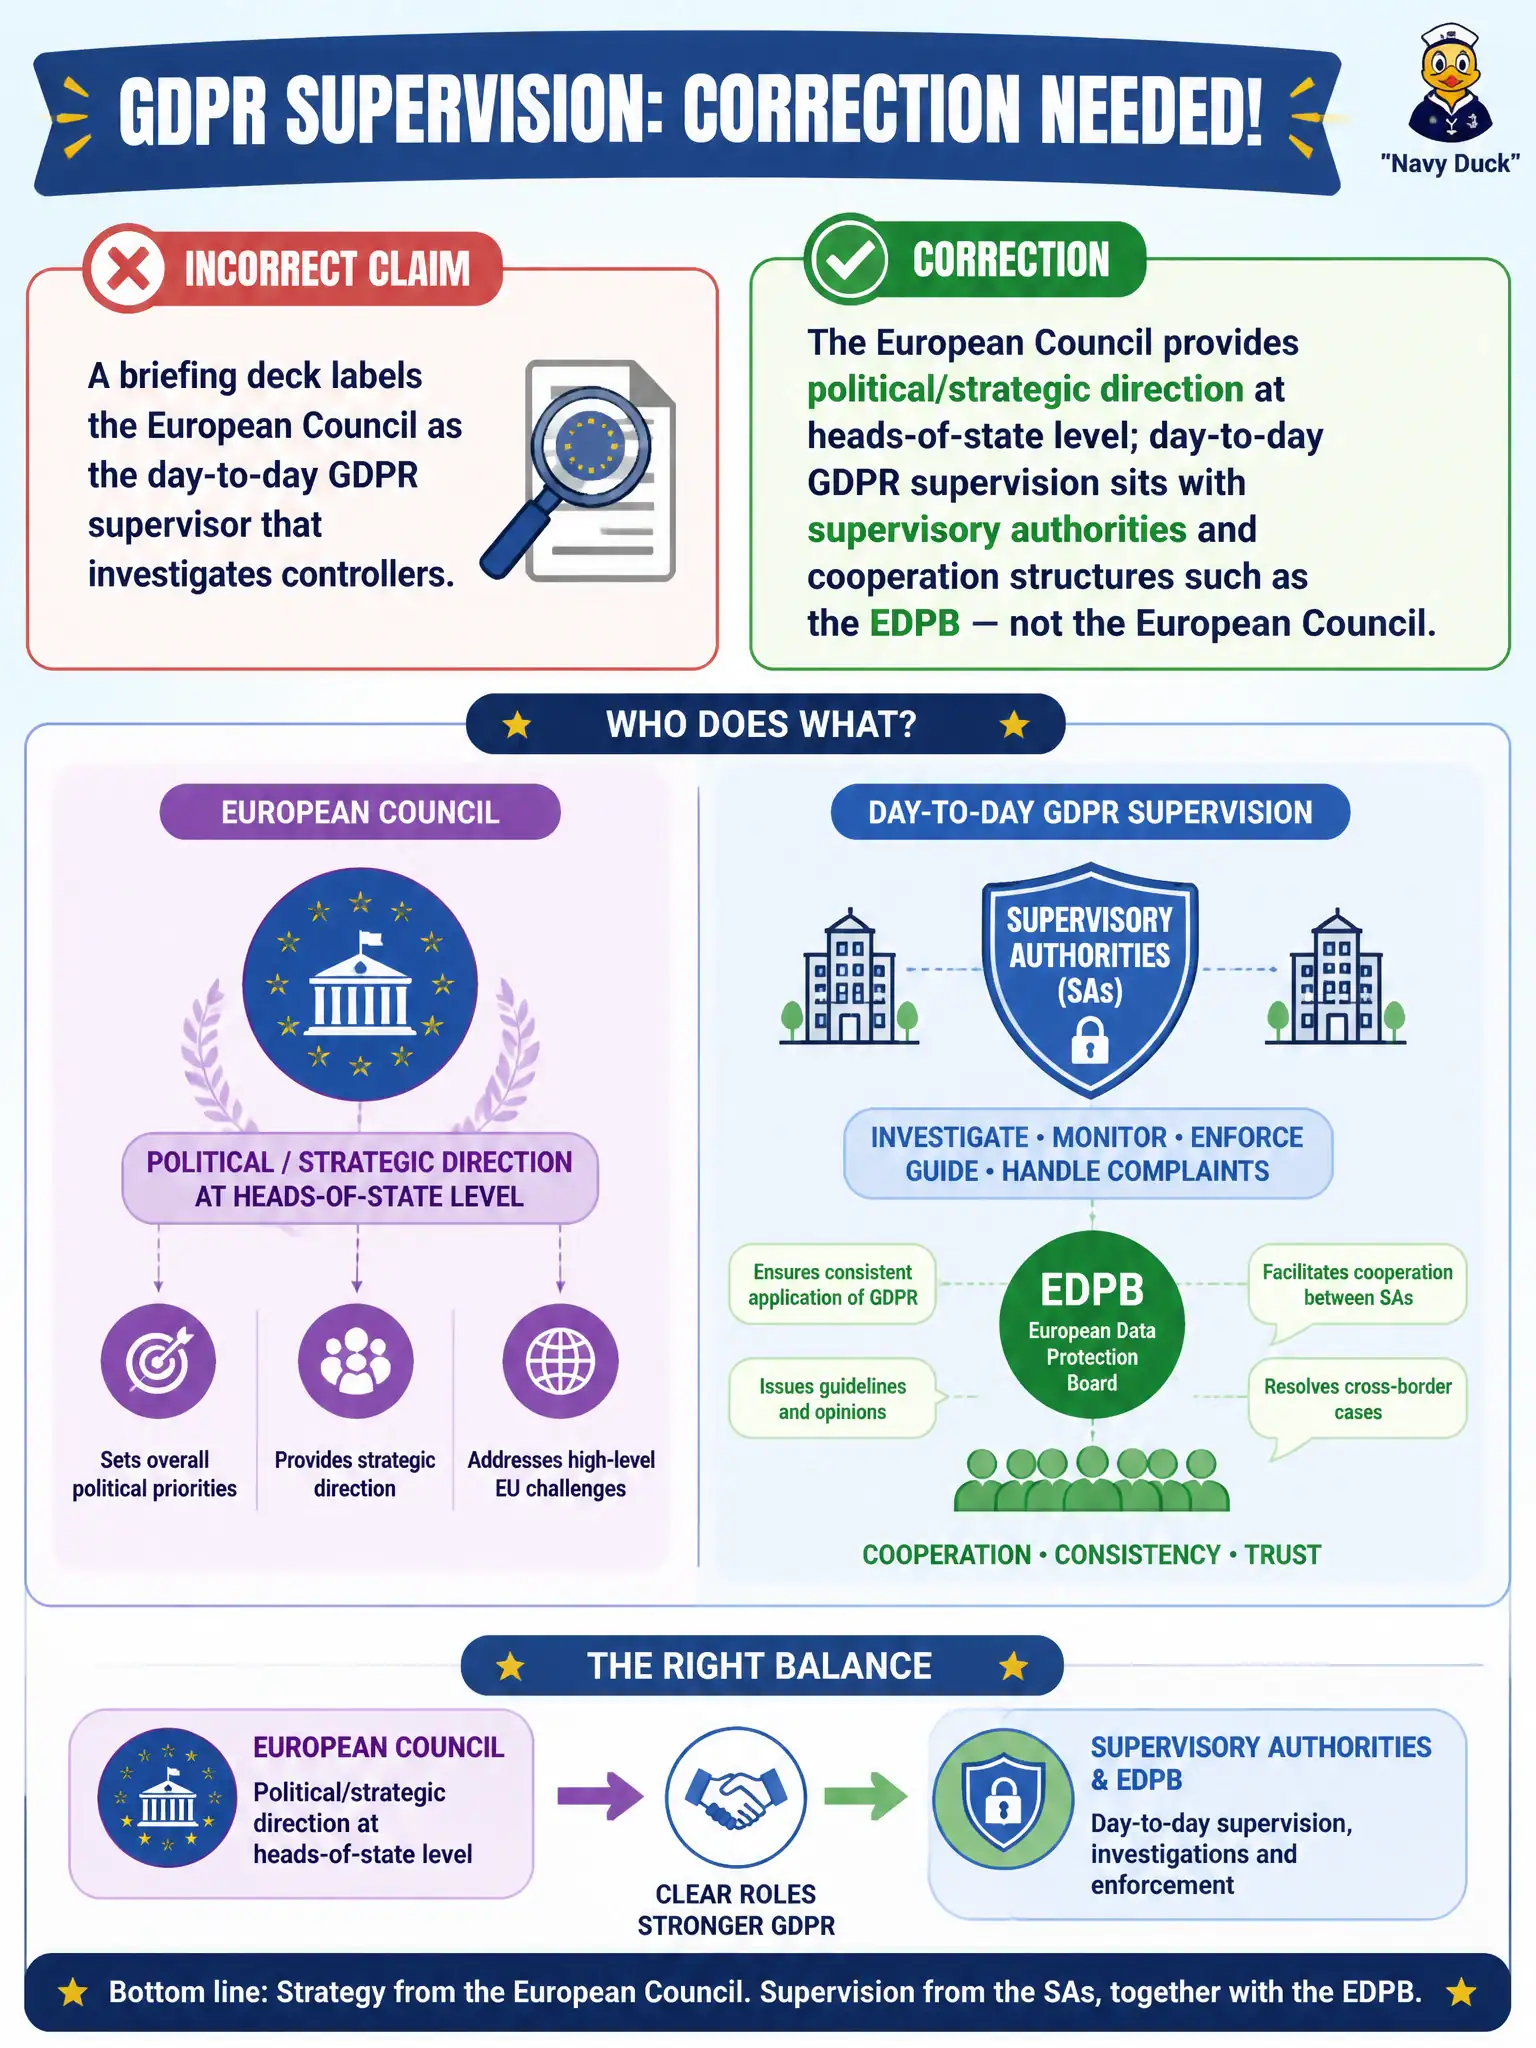
A briefing deck labels the European Council as the day-to-day GDPR supervisor that investigates controllers. What correction is needed?
Select an answer to reveal the explanation.
Short Explanation
The European Council is the big-picture political summit table, not the privacy inspector knocking on a controller’s door. Day-to-day GDPR supervision lives with national supervisory authorities and EU cooperation bodies like the EDPB. Wrong layer, wrong job title.
Full Explanation
The European Council provides political and strategic direction at heads-of-state-or-government level; it is not the day-to-day GDPR supervisor that investigates controllers. Briefing decks that label it as operational enforcement confuse summit-level politics with independent supervisory authorities and cooperation structures such as the EDPB (and the EDPS for EU institutions). The European Council does not issue all breach notifications for every controller. It does not replace national supervisory authorities for routine audits. It is not identical to the EDPS and does not fine EU institutions daily as a substitute supervisor. Operational GDPR supervision remains with independent SAs applying investigative and corrective powers under the Regulation’s enforcement chapters. Exam caveat: European Council is not the Council of the EU, not the EDPB, and not the EDPS—role separation is the tested skill. Operational check: rewrite any slide that says European Council supervises GDPR to SAs enforce, EDPB consistency, European Council equals political direction, and verify your incident-response runbook lists the competent SA contact, not a European Council mailbox. For municipal teams, keep a one-page decision note that states the governing instrument, why competing labels fail, and what evidence would change the conclusion.