
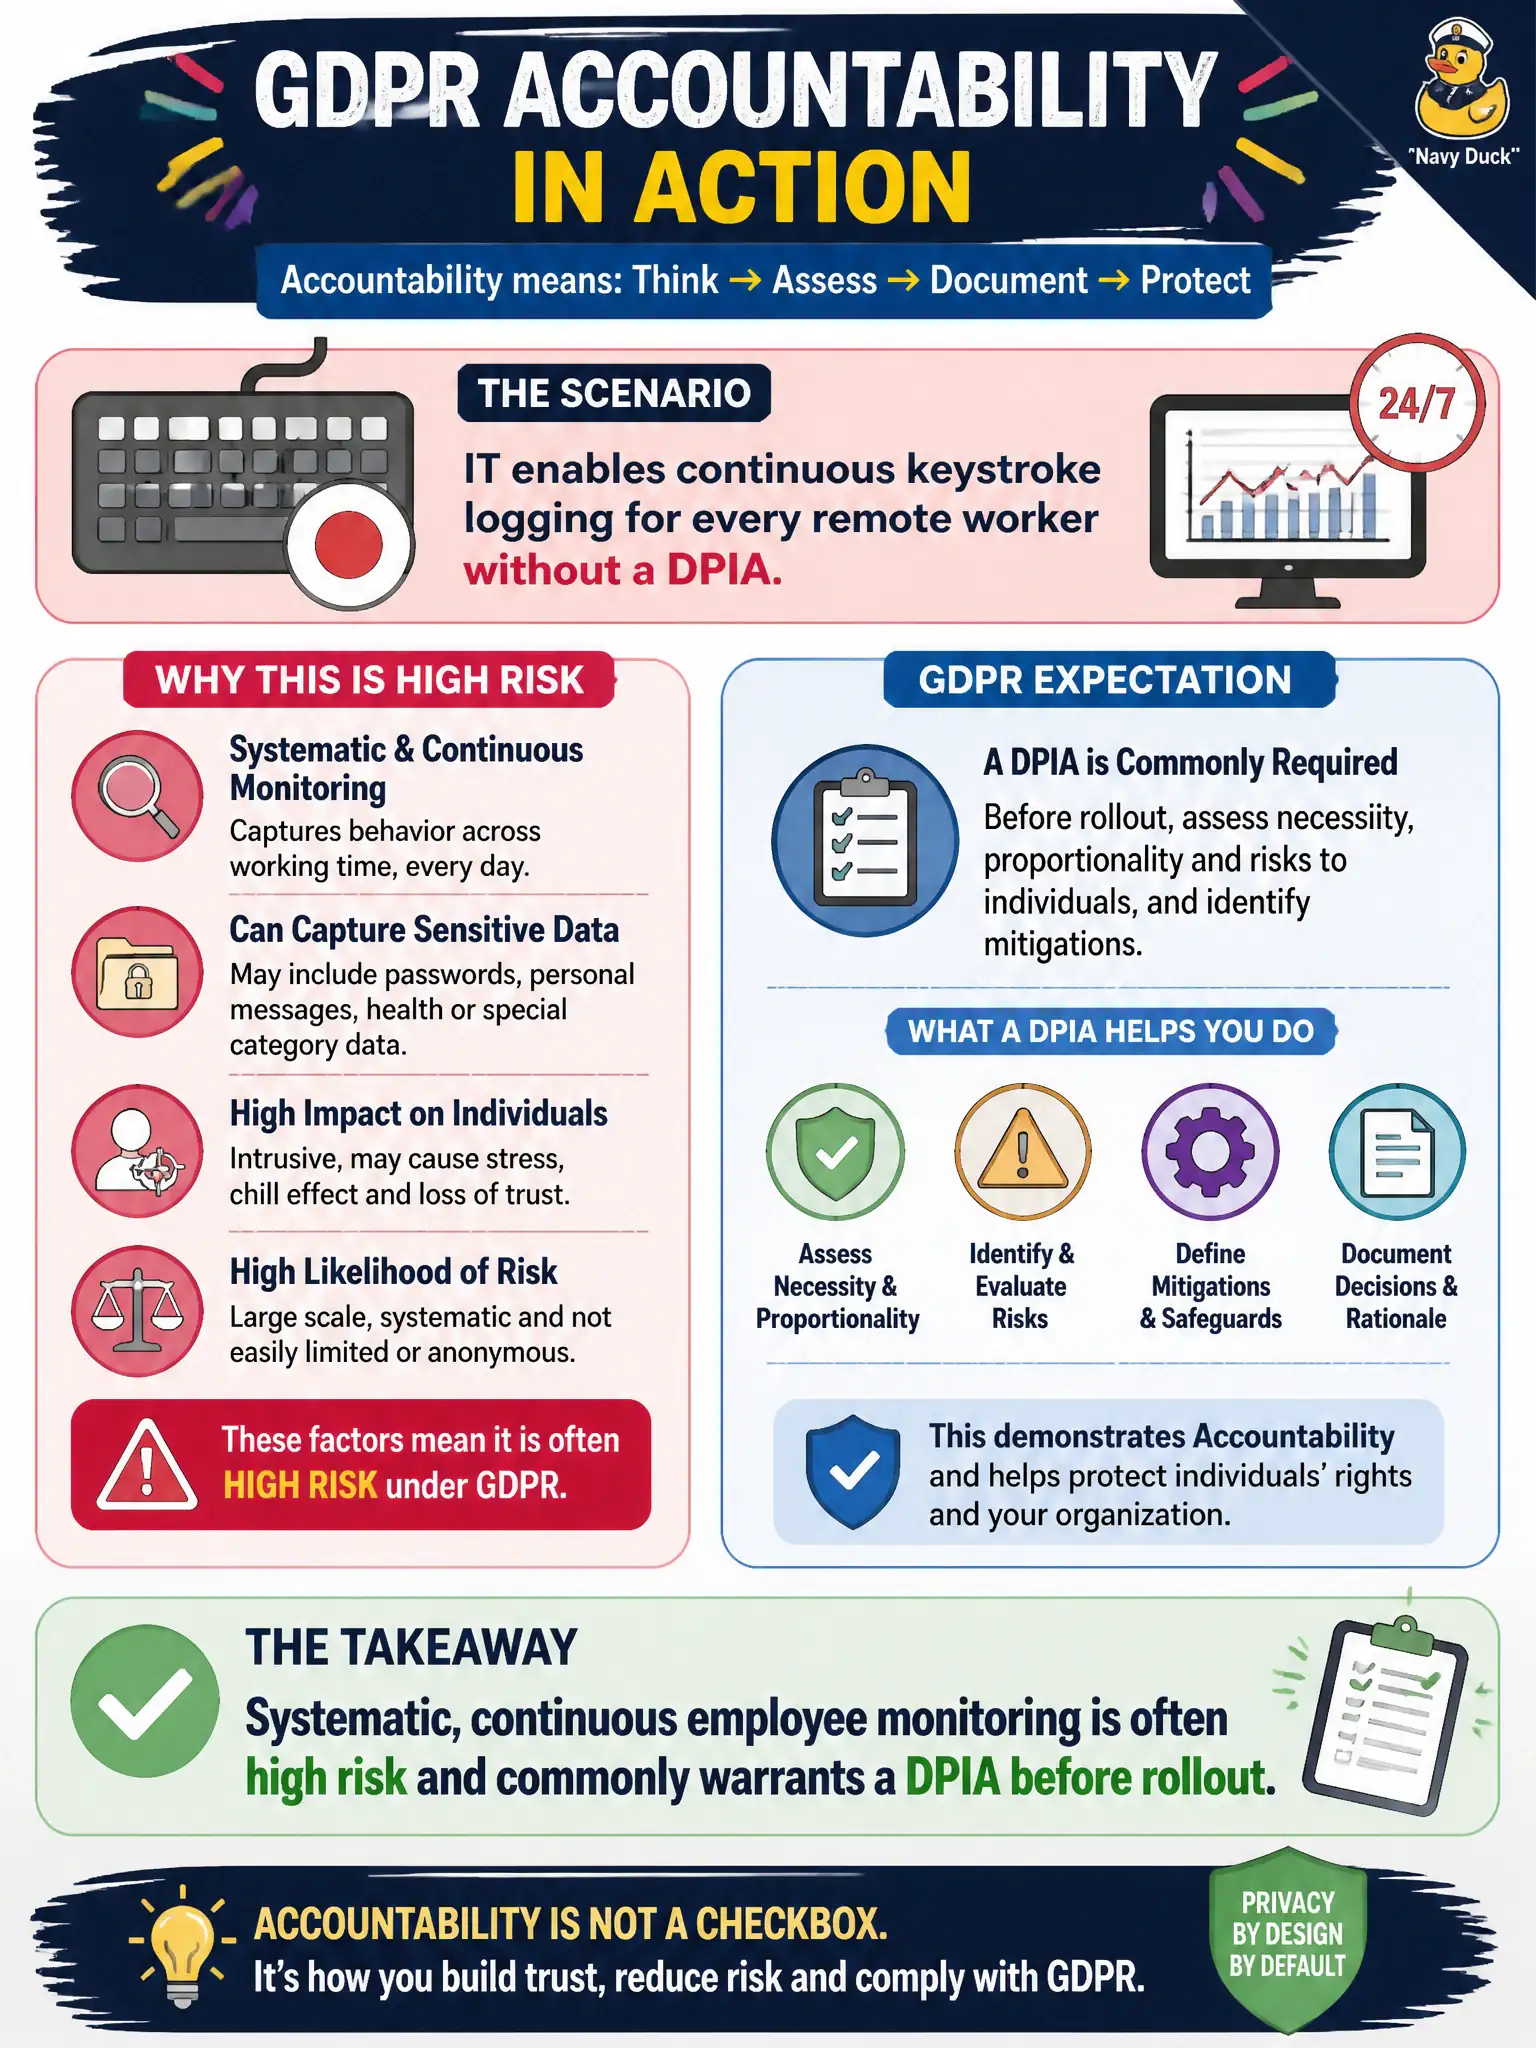
IT enables continuous keystroke logging for every remote worker without a DPIA. Which statement best reflects GDPR accountability expectations?
Select an answer to reveal the explanation.
Short Explanation
Logging every keystroke for the whole remote workforce is not a casual IT tweak—it’s high-intrusion monitoring. Do the risk homework (often a DPIA) before you flip the switch. Skipping that is accountability theatre.
Full Explanation
IT enabling continuous keystroke logging for every remote worker without a DPIA best reflects that systematic, continuous employee monitoring is often high risk and commonly warrants a DPIA before rollout. Logging every keystroke is among the most intrusive workplace surveillance patterns and demands documented risk analysis before citizens-as-workers are placed under constant capture. Saying keystroke logging is low risk because remote workers ‘expect surveillance’ fails—expectation myths do not erase Article 35 triggers. Claiming DPIAs are optional marketing documents never applicable to employment tools fails the Regulation’s high-risk assessment duty. Saying a DPIA is required only after an SA fine has already been issued fails timing—DPIAs are prior accountability tools, not post-fine paperwork. Exam caveat: not every minor IT log is a DPIA candidate, but continuous keystroke capture of a workforce is a paradigm high-risk example alongside systematic monitoring criteria. Operational check: stop or pause logging pending DPIA, assess necessity and less intrusive alternatives, involve the DPO, implement mitigations or cancel the programme, and retain the DPIA with go/no-go evidence.