
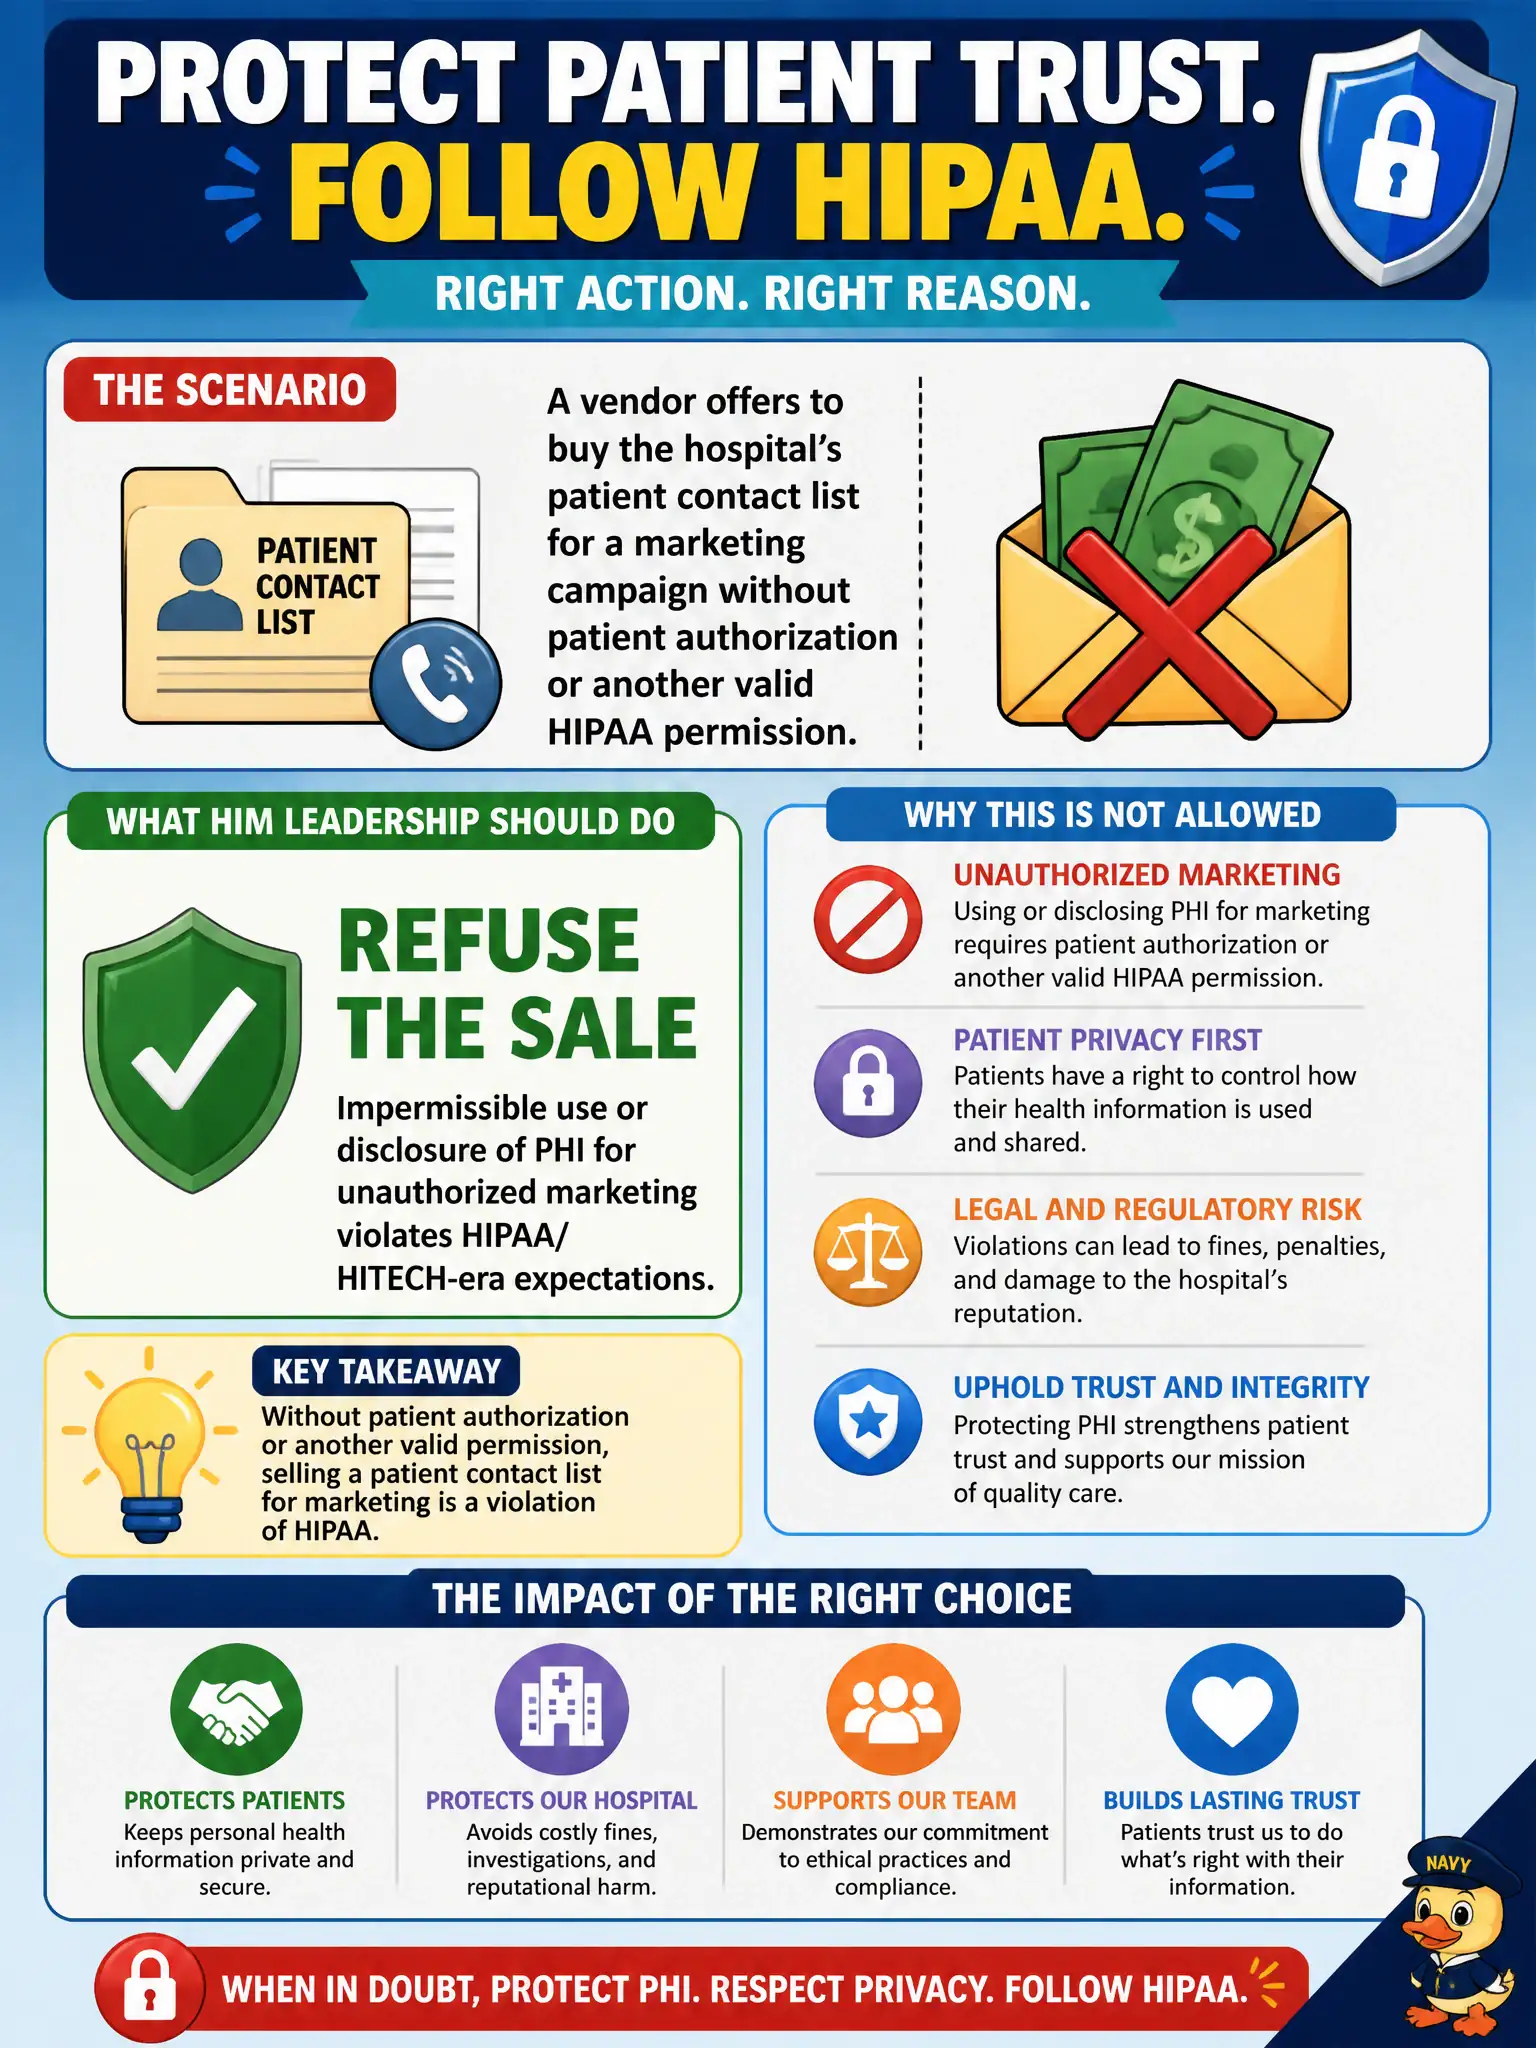
A vendor offers to buy the hospital’s patient contact list for a marketing campaign without patient authorization or another valid HIPAA permission. What should HIM leadership do?
Select an answer to reveal the explanation.
Short Explanation
Patient lists aren’t inventory for the marketing clearance rack. No authorization, no valid permission—no sale. That’s a hard stop, not a pricing discussion.
Full Explanation
If a vendor offers to buy a civic hospital's patient contact list for a marketing campaign without patient authorization or another valid HIPAA permission, HIM leadership must refuse the sale; impermissible use or disclosure of PHI for unauthorized marketing violates HIPAA/HITECH-era expectations. Public hospitals are stewards of resident data, not brokers of contact lists. Selling the list if the price exceeds the last EHR upgrade treats PHI as inventory. Providing limited demographics only because marketing always qualifies as healthcare operations misstates when marketing requires authorization. Allowing the sale if patients are not celebrities invents a VIP enforcement myth—privacy protects everyone. Exam caveat: marketing disclosures generally need authorization or a narrow permitted pathway; price never creates permission. Operational check: decline the offer in writing, consult privacy counsel, review any BAAs for prohibited sale language, and retrain staff that patient lists are not revenue products. Treat encoders, groupers, and CAC as assistants inside civic HIM: useful for speed, never a substitute for documentation review, Official Guidelines, or PHI safeguards. Re-read the authenticated record before finalizing whenever tools, payers, or dashboards push a result the documentation does not support.