
A stormwater bureau must renew Edge certificates before expiry. What operational risk does letting Edge certificates expire typically create?
Select an answer to reveal the explanation.
Short Explanation
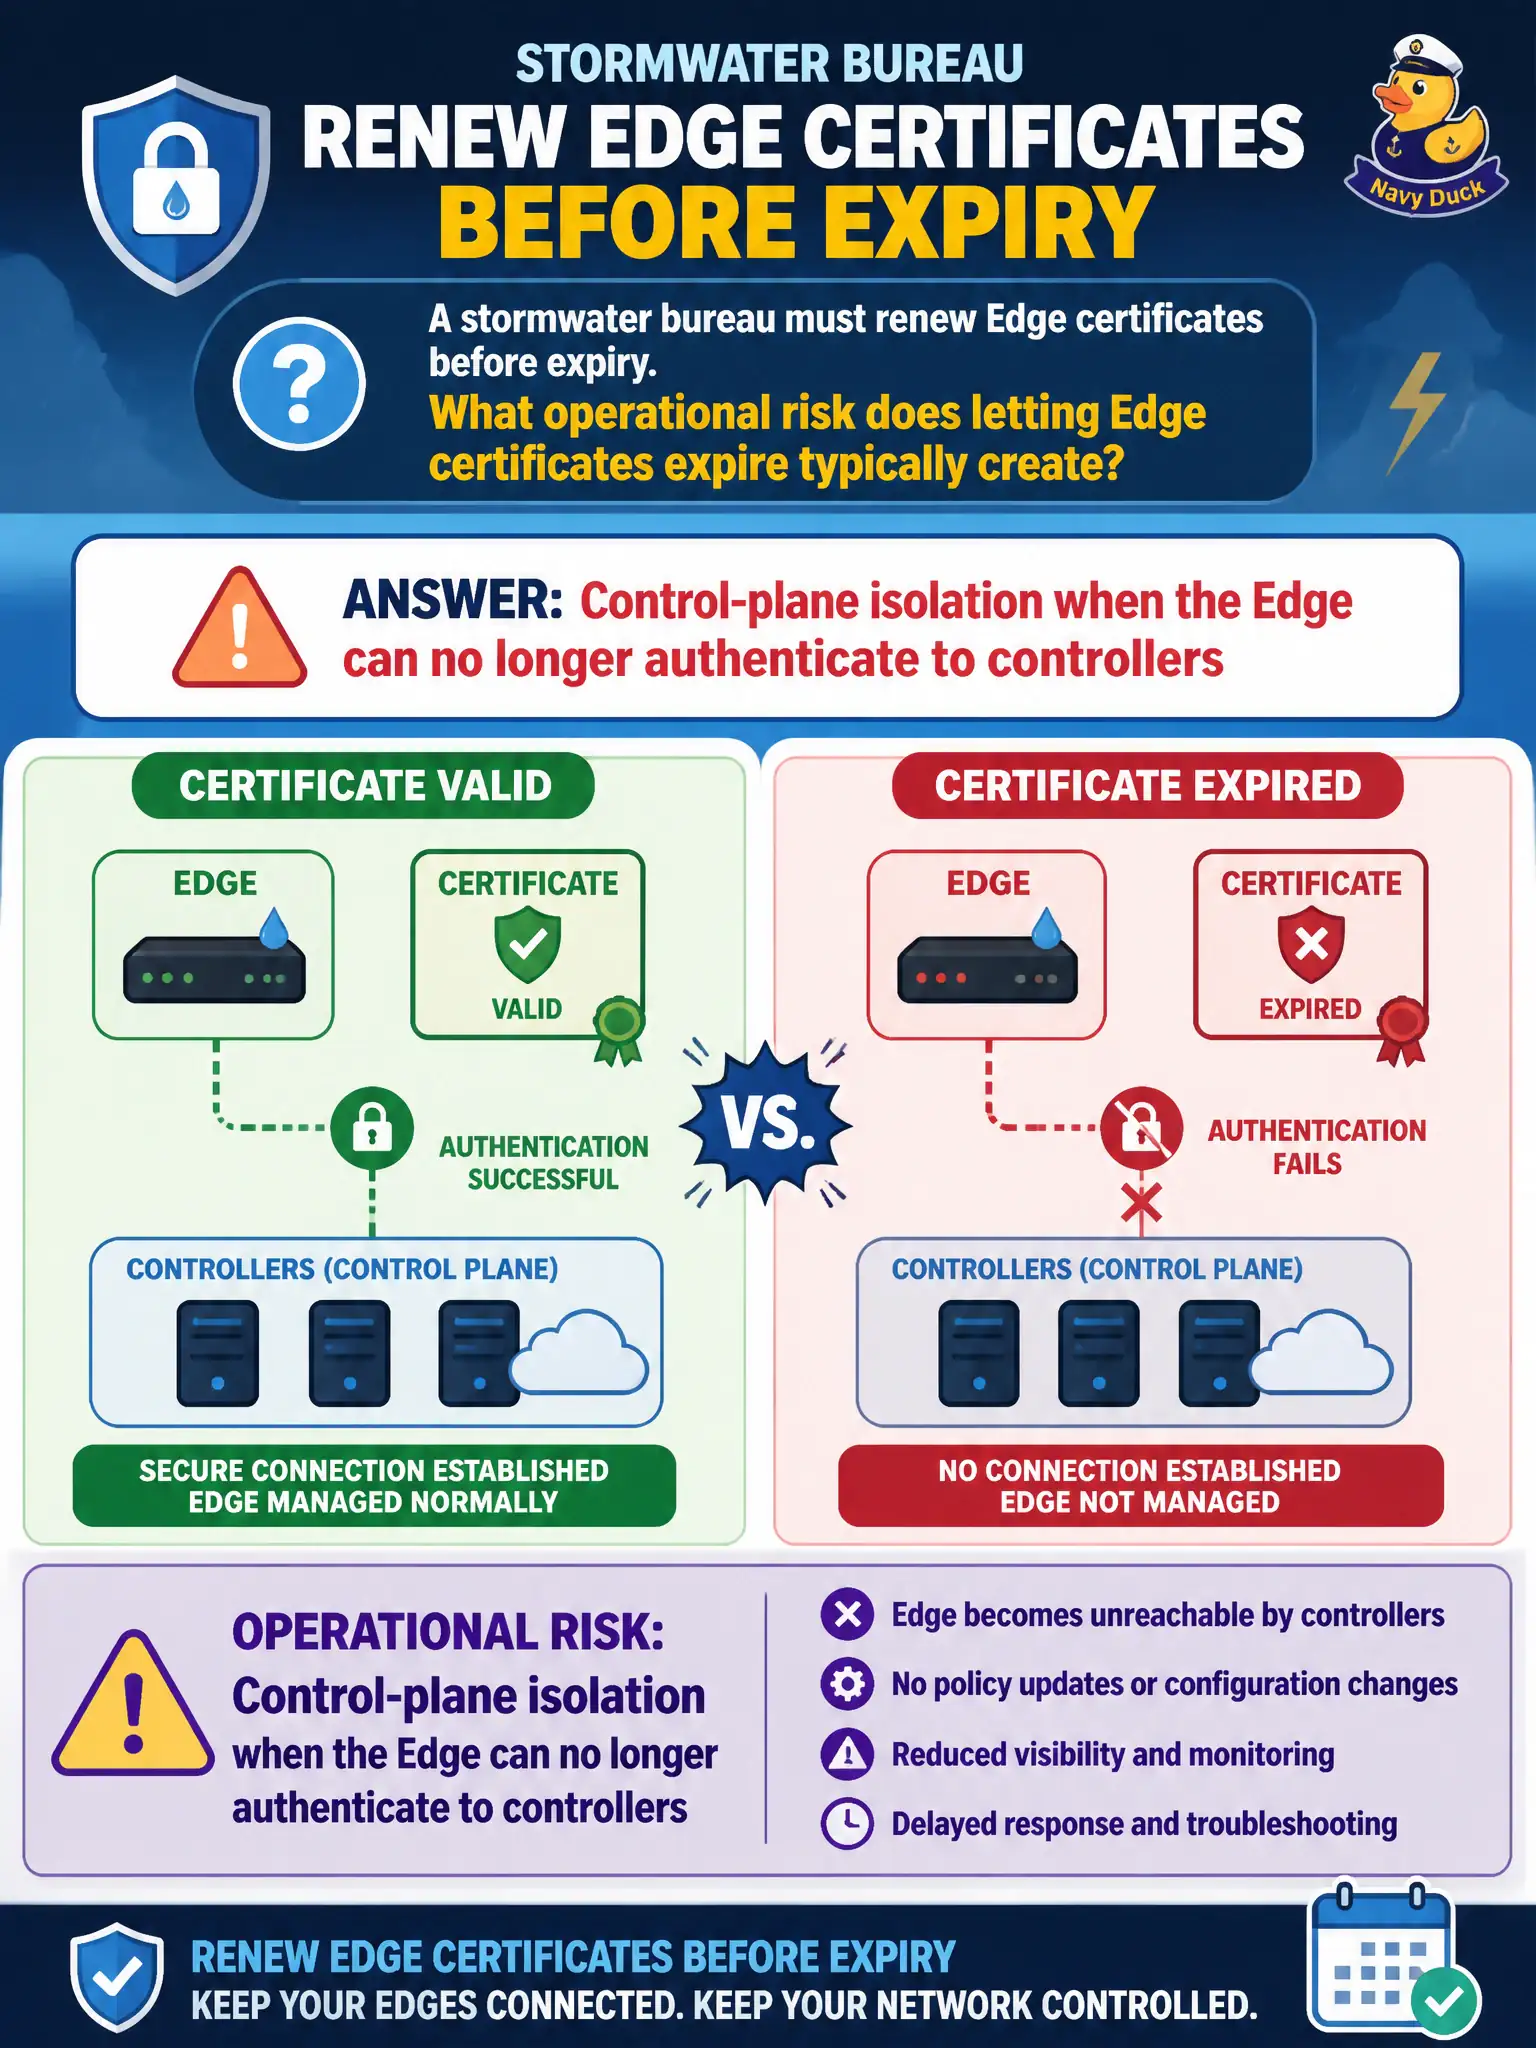
Expired Edge certs aren’t a yellow sticky note—they’re a locked door to the controllers. When authentication fails, the Edge can fall off the control plane even if the underlay circuit still lights up. Renew before the birthday passes.
Full Explanation
SD-WAN Edges authenticate to the controller fabric with certificates grounded in the organization’s PKI trust model. If a stormwater bureau lets an Edge certificate expire, control connections can fail and the device becomes isolated from policy and route distribution even though underlay IP reachability may still look healthy. Certificate expiry is therefore a control-plane outage risk that can strand a civic site, not a cosmetic dashboard footnote.
Treating expiry as cosmetic-only warnings with no control or data impact understates the failure mode operators actually see. Automatic downgrade of all service VPNs into one best-effort VRF is not the certificate-expiry behavior. Permanent deletion of localized CLI templates from vManage is not the typical result of an Edge certificate passing its not-after date.
Exam caveat: expired identity breaks authenticated control sessions—treat certificate lifecycle as mandatory operations work, not optional hygiene after go-live.
Operational check: inventory Edge certificate expiration dates, renew before expiry with validated chains, confirm renewed control connections and OMP exchange, and alert on upcoming expirations for every stormwater Edge in vManage.