
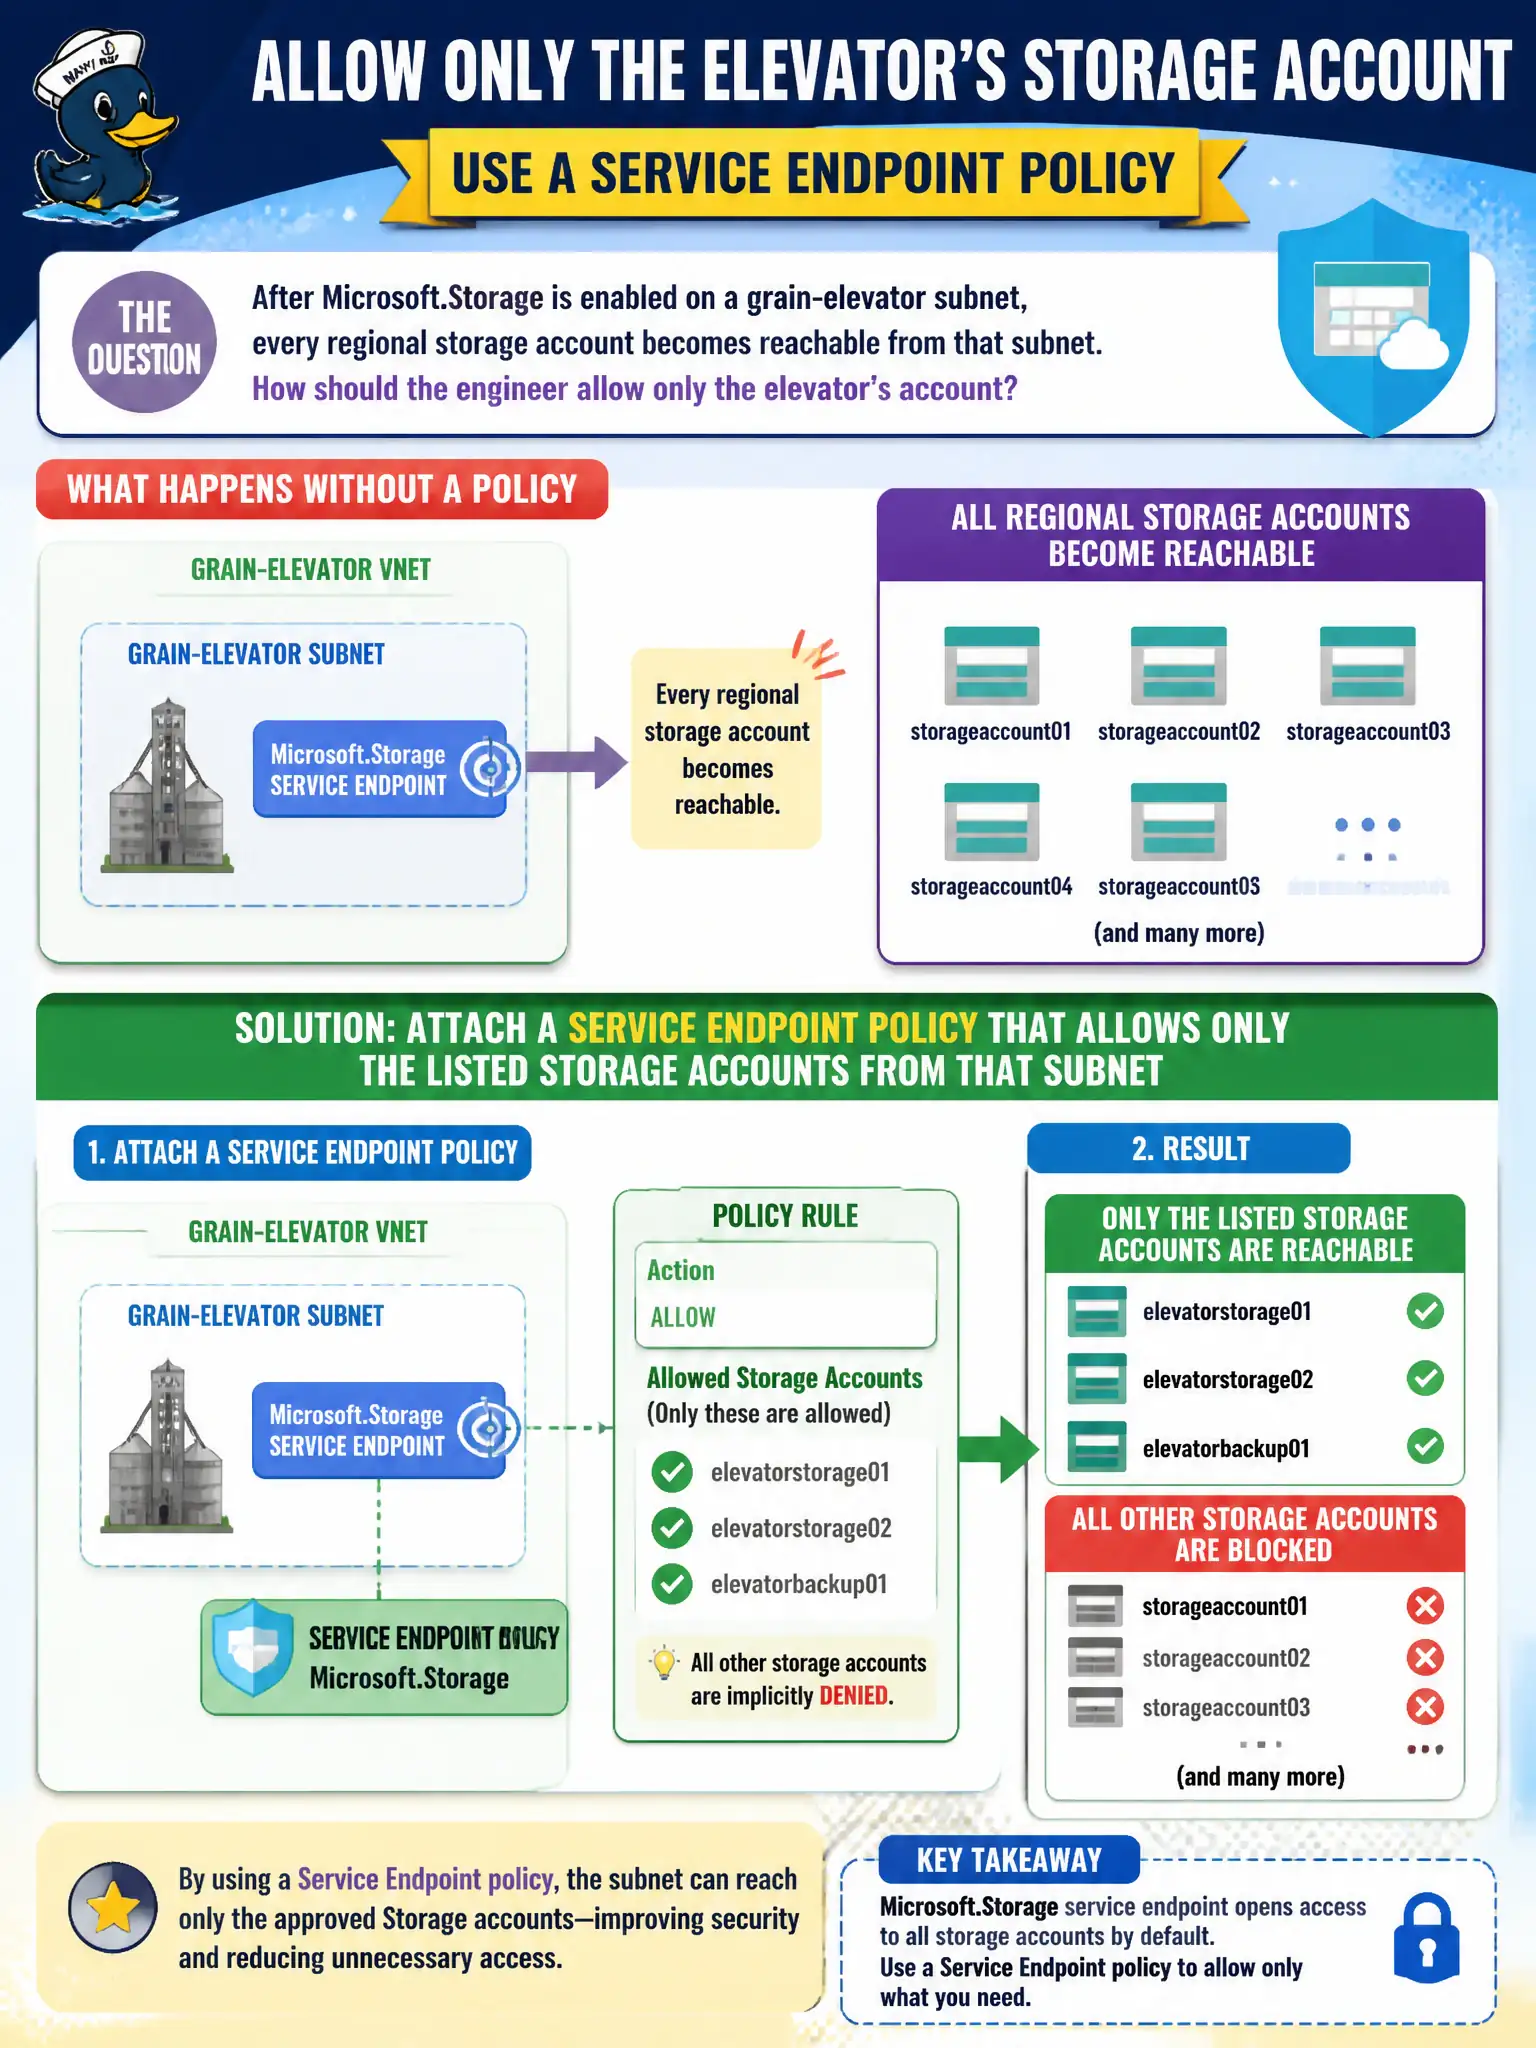
After Microsoft.Storage is enabled on a grain-elevator subnet, every regional storage account becomes reachable from that subnet. How should the engineer allow only the elevator’s account?
Select an answer to reveal the explanation.
Short Explanation
Service Endpoint without a guest list is an open house for every storage account in the region. Hang a Service Endpoint policy that names only the elevator’s account.
Full Explanation
Service endpoint policies for Azure Storage limit which storage accounts a subnet with Microsoft.Storage can reach, preventing “any regional storage account” access after the service endpoint is enabled. Attach a Service Endpoint policy that allows only the grain elevator’s listed Storage accounts from that subnet.
Creating a Private Link service on an ILB in front of Blob fails as the control for limiting Service Endpoint reachability to listed accounts. Assigning a Policy initiative that deletes all other storage accounts is destructive overkill. Opening the storage firewall to all networks so least privilege is only at identity layer fails network least privilege.
Exam caveat: Service Endpoint policies refine Service Endpoints; they are not Private Link. Operational check: create a policy allowing only the elevator account, associate it to the subnet, verify allowed account works, verify a different regional account fails from that subnet. In municipal Azure estates, document the decision in the change record, validate with a nonproduction rehearsal, and confirm monitoring still pages the on-call operator when the control fails closed during an incident drill. In municipal Azure estates, document the decision in the change record, validate with a nonproduction rehearsal, and confirm monitoring still pages the on-call operator when the control fails closed during an incident drill.