
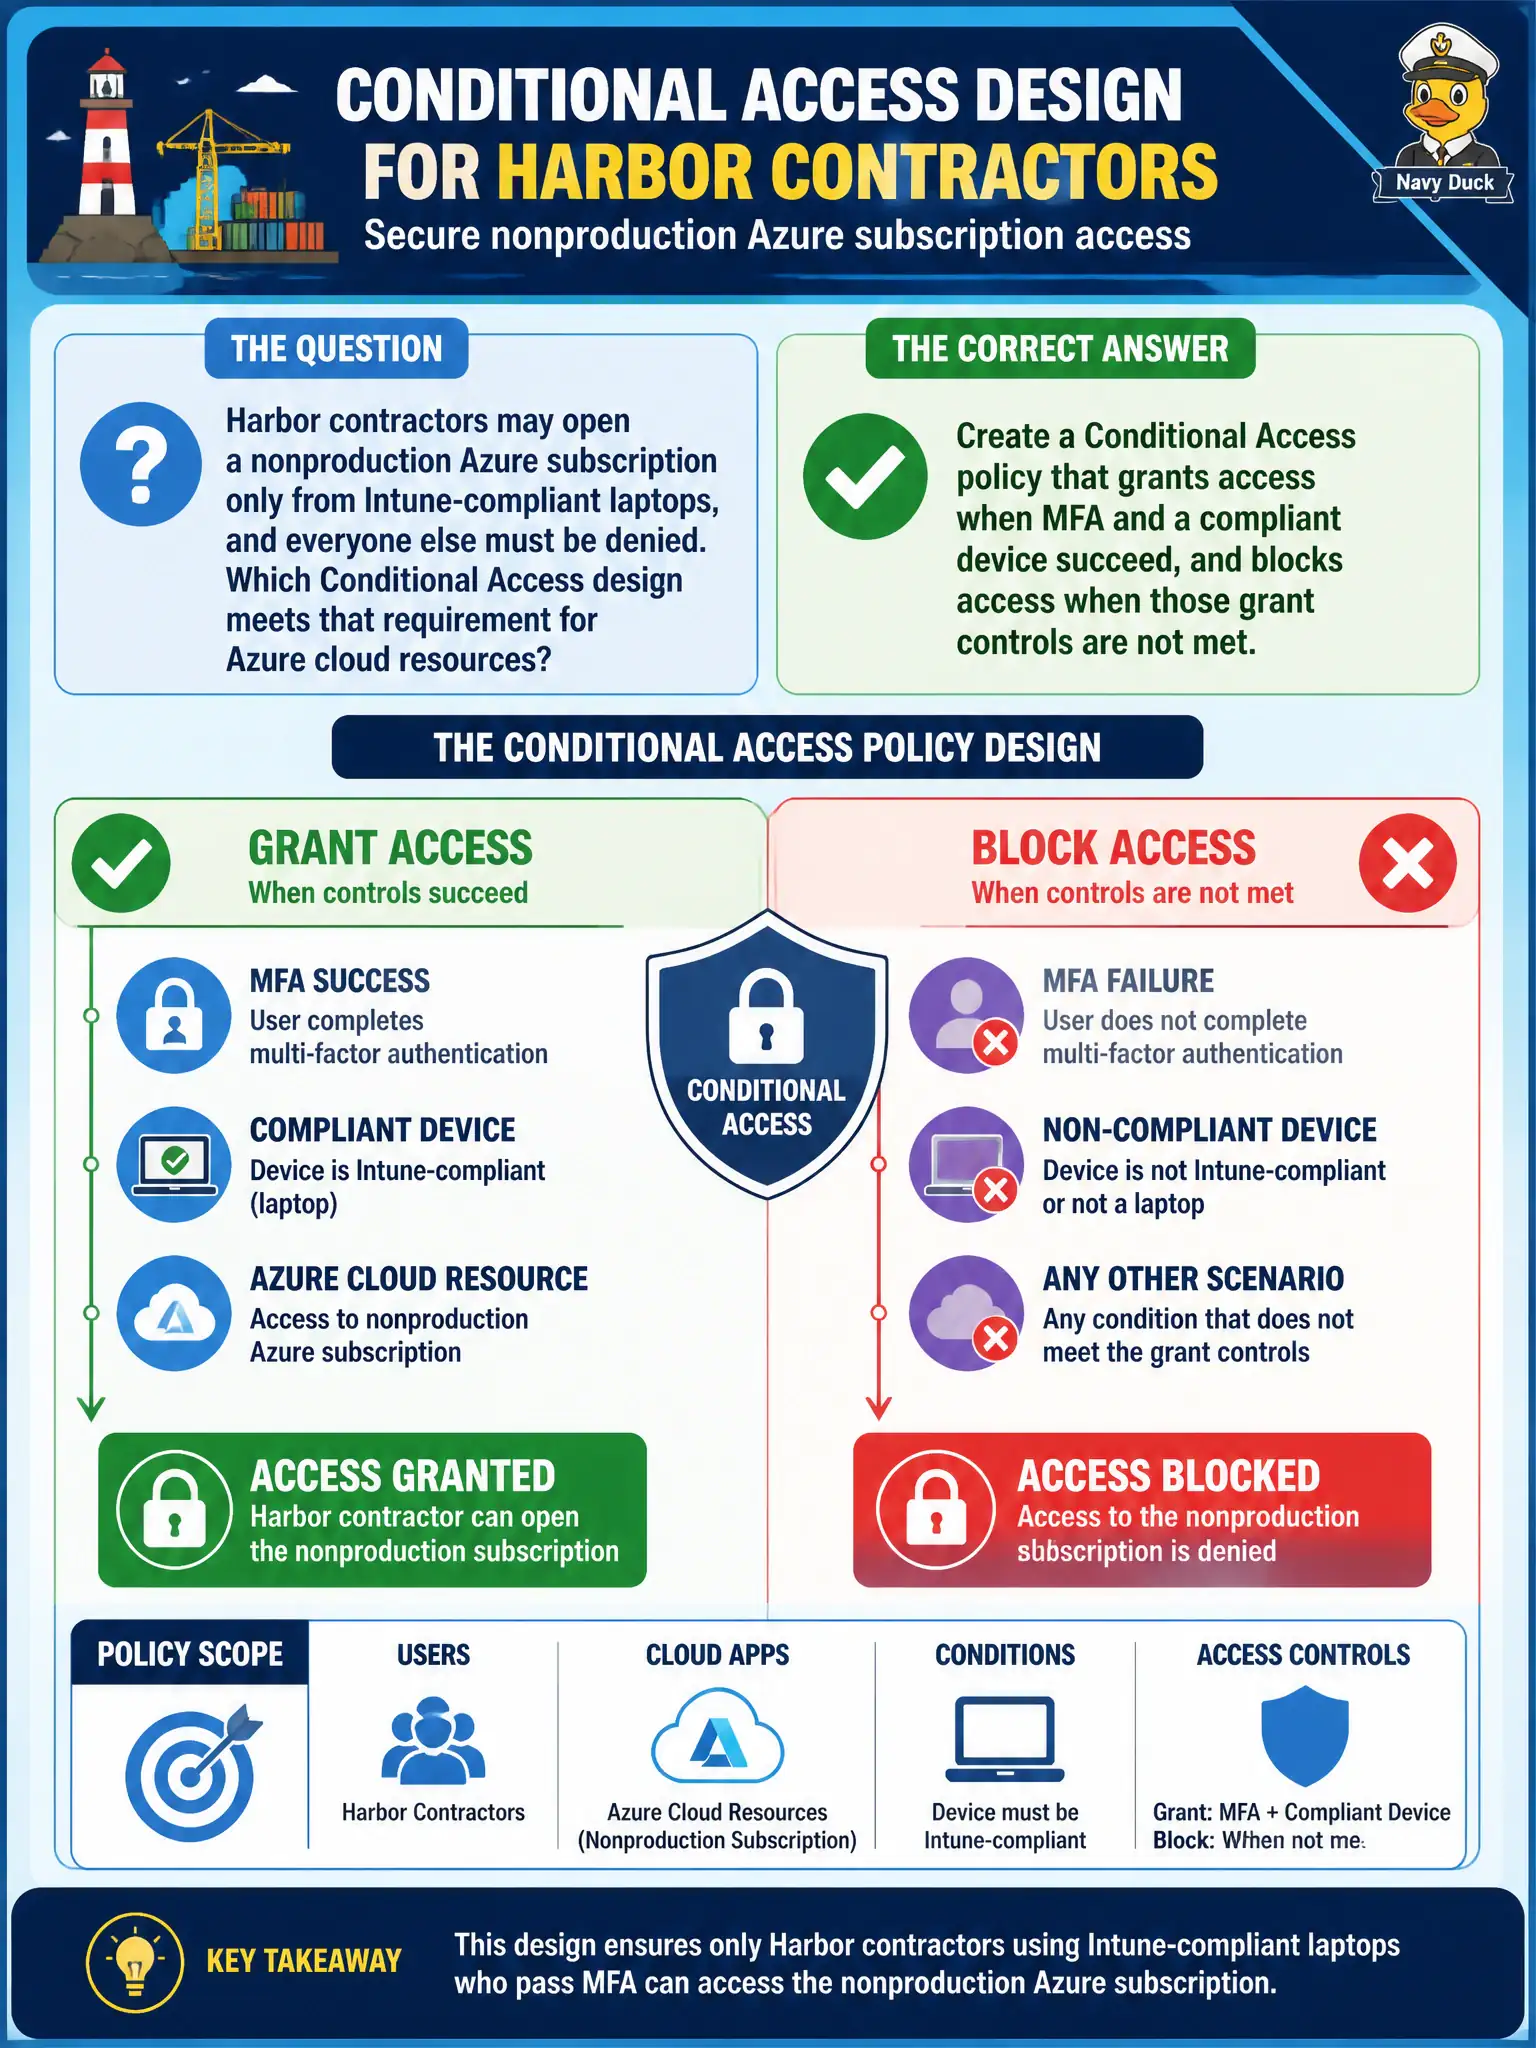
Harbor contractors may open a nonproduction Azure subscription only from Intune-compliant laptops, and everyone else must be denied. Which Conditional Access design meets that requirement for Azure cloud resources?
Select an answer to reveal the explanation.
Short Explanation
Think of Conditional Access as the harbor gate: grant means “show your badge and a compliant laptop,” and block means “turn around.” Stack require MFA and require compliant device as grants for the contractors, then block everyone who cannot meet those grants—do not try to fake that with an NSG on their Wi-Fi.
Full Explanation
Conditional Access policies for Azure cloud resources combine conditions with grant controls such as require MFA and require compliant device, and they can block when those grants are not satisfied. For harbor contractors who may open a nonproduction subscription only from Intune-compliant laptops—while everyone else is denied—the correct design is a Conditional Access policy that grants access when MFA and compliant device succeed and blocks access when those grant controls are not met, targeted appropriately at Azure management and the contractor users/groups.
Putting an NSG on the contractors’ Wi-Fi subnet fails by concept: NSGs filter Azure virtual-network traffic to NICs/subnets; they do not enforce Entra device compliance or MFA for portal sign-ins and cannot replace Conditional Access grant controls. Using only session controls such as app enforced restrictions without grant or block controls fails because session controls refine an allowed session; they do not by themselves implement the allow-only-when-compliant-or-else-block requirement. Enabling Defender for Cloud Apps session monitoring alone fails similarly: monitoring without Conditional Access grant/block enforcement does not deny noncompliant access to Azure cloud resources.
Exam caveat: grant controls decide whether access is allowed; session controls shape the session after a grant path succeeds—do not confuse the two on AZ-500. Operational check: create the policy for contractors and Azure management, require MFA + compliant device, test with a compliant laptop (success) and a noncompliant device (block), and confirm non-contractors remain denied.