
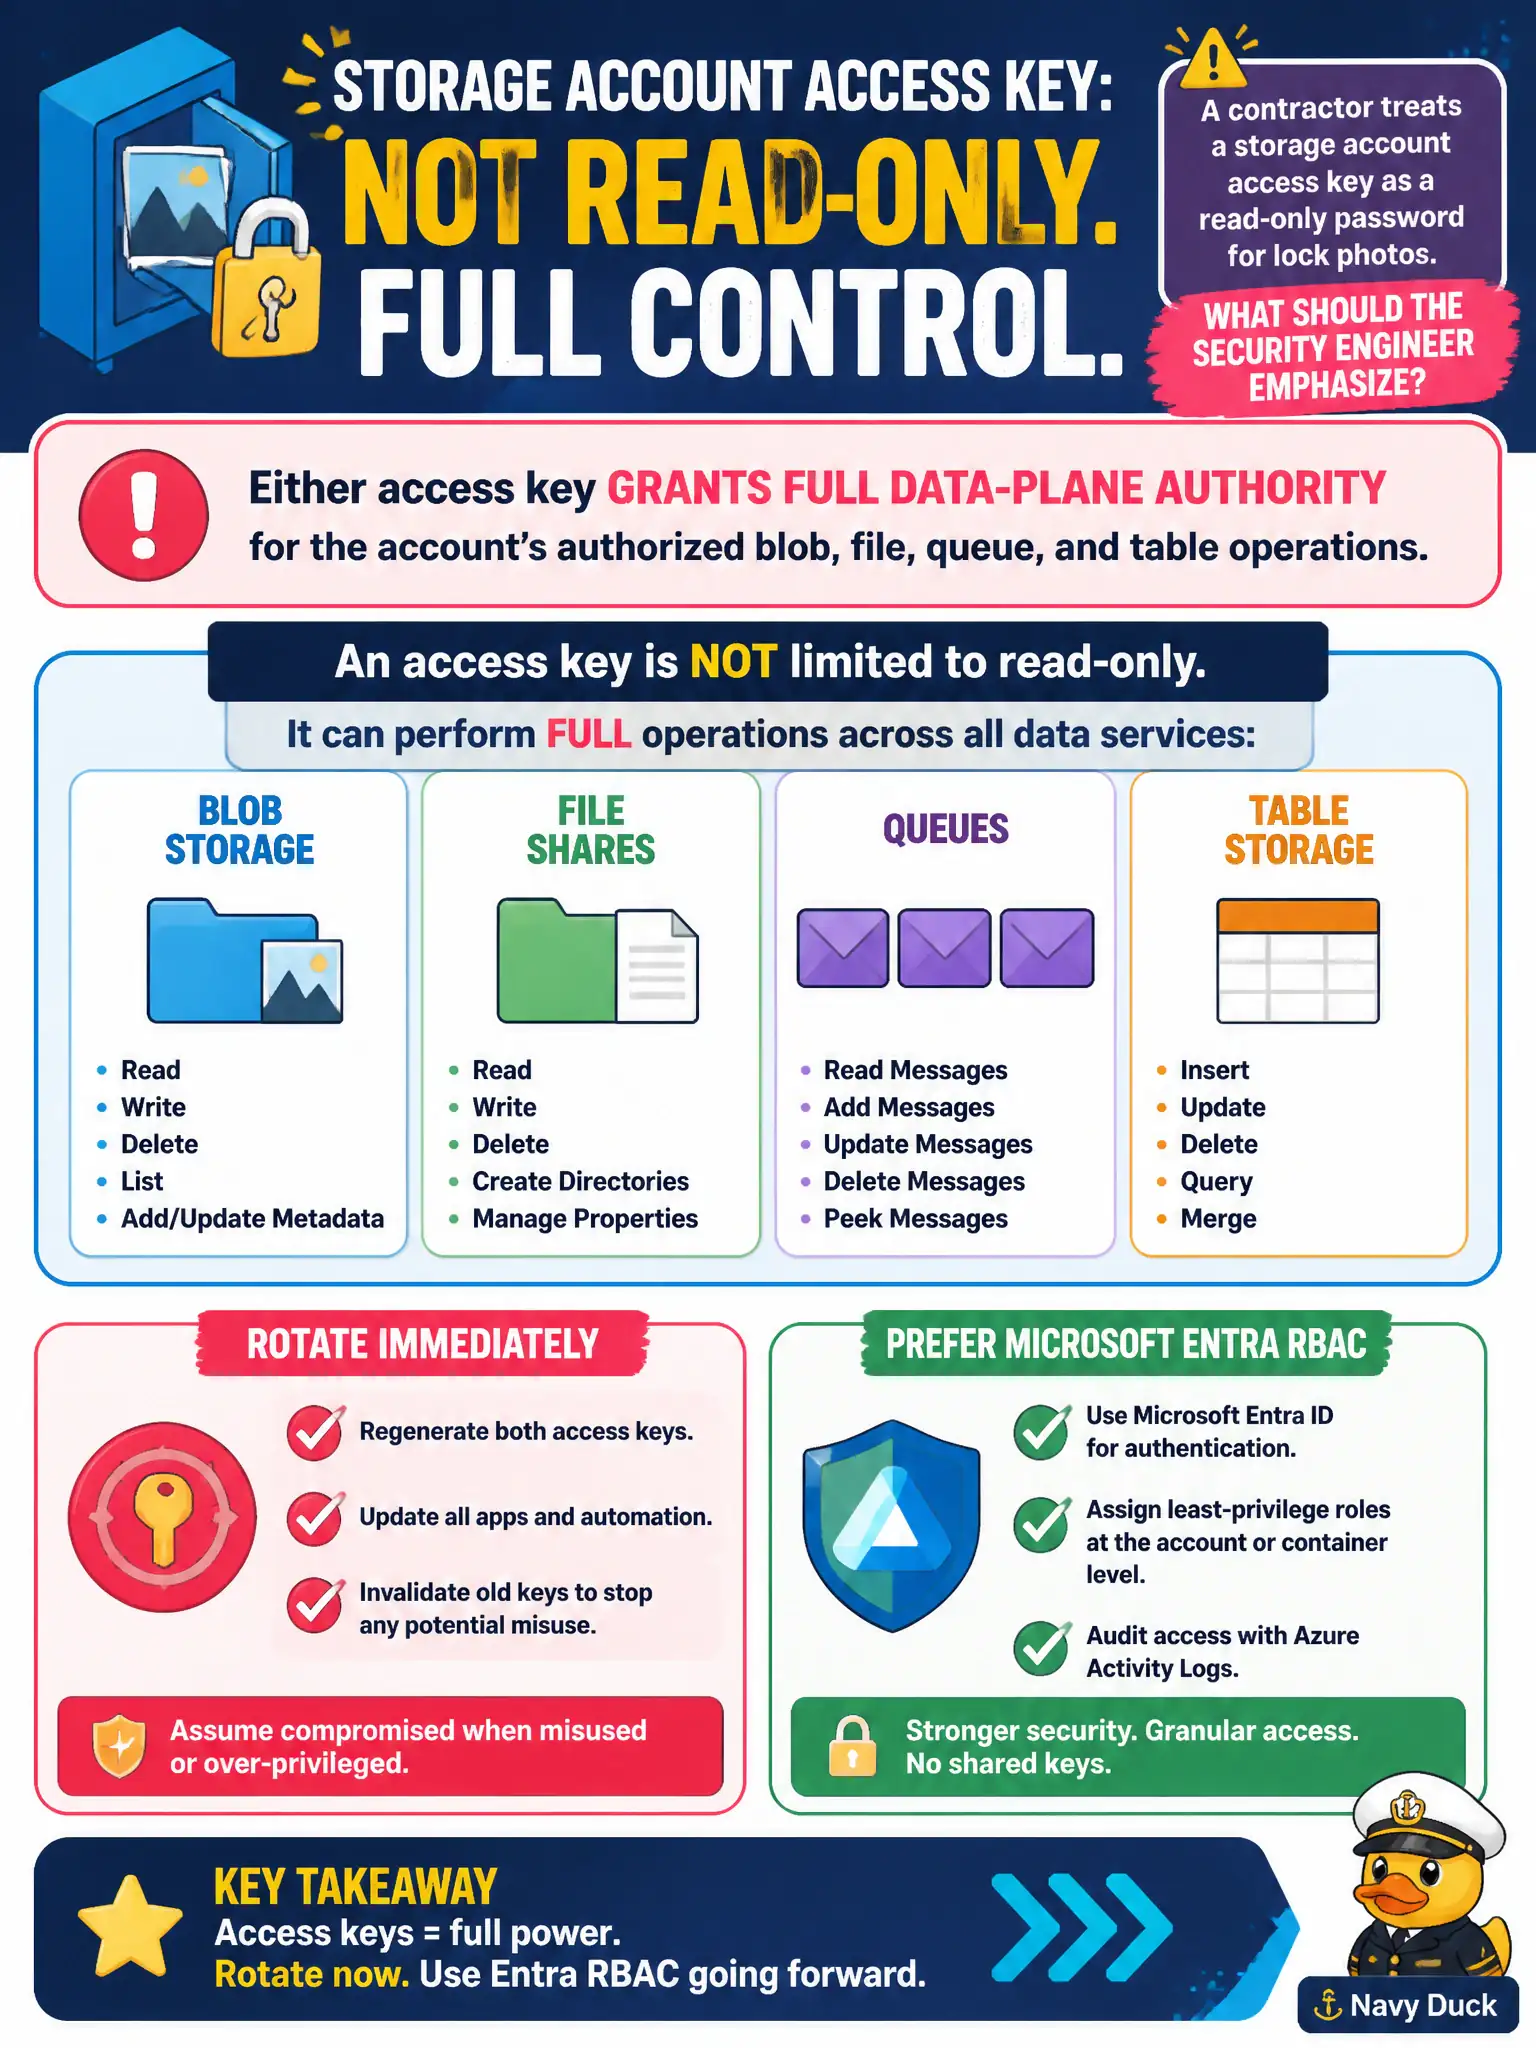
A contractor treats a storage account access key as a read-only password for lock photos. What should the security engineer emphasize?
Select an answer to reveal the explanation.
Short Explanation
That “read-only password” is really the master till key—either key runs the data plane. Rotate it now and move folks to Entra roles.
Full Explanation
A contractor who treats a storage account access key as a read-only password for lock photos must be corrected: either access key grants full data-plane authority for the account’s authorized blob, file, queue, and table operations. It is not a read-only credential and is not limited to opening the Azure portal blade. After exposure or misuse, regenerate immediately and prefer Microsoft Entra RBAC with data-plane roles for ongoing human and application access. In a municipal photo archive, mistaking the master till key for a viewer badge is a high-severity misunderstanding.
Claiming an access key can only open the Azure portal blade and cannot call data-plane APIs fails by concept: keys authenticate data-plane API calls across supported storage services. Asserting that key1 is read-only and key2 is read-write fails because the two keys are interchangeable peer keys with equivalent power, not a read/write split. Claiming access keys automatically expire after one hour like a user-delegation SAS fails: account keys are long-lived until regenerated and do not inherit SAS lifetime semantics.
Exam caveat: key1 and key2 are peers with broad data-plane power; user-delegation SAS and Entra RBAC are the least-privilege alternatives the exam contrasts with raw keys. Operational check: regenerate the disclosed key using the two-key rotation pattern, revoke any stored copies, assign Storage Blob Data Reader or Contributor as appropriate instead of redistributing keys, and update contractor onboarding so lock-photo access is identity-based.