
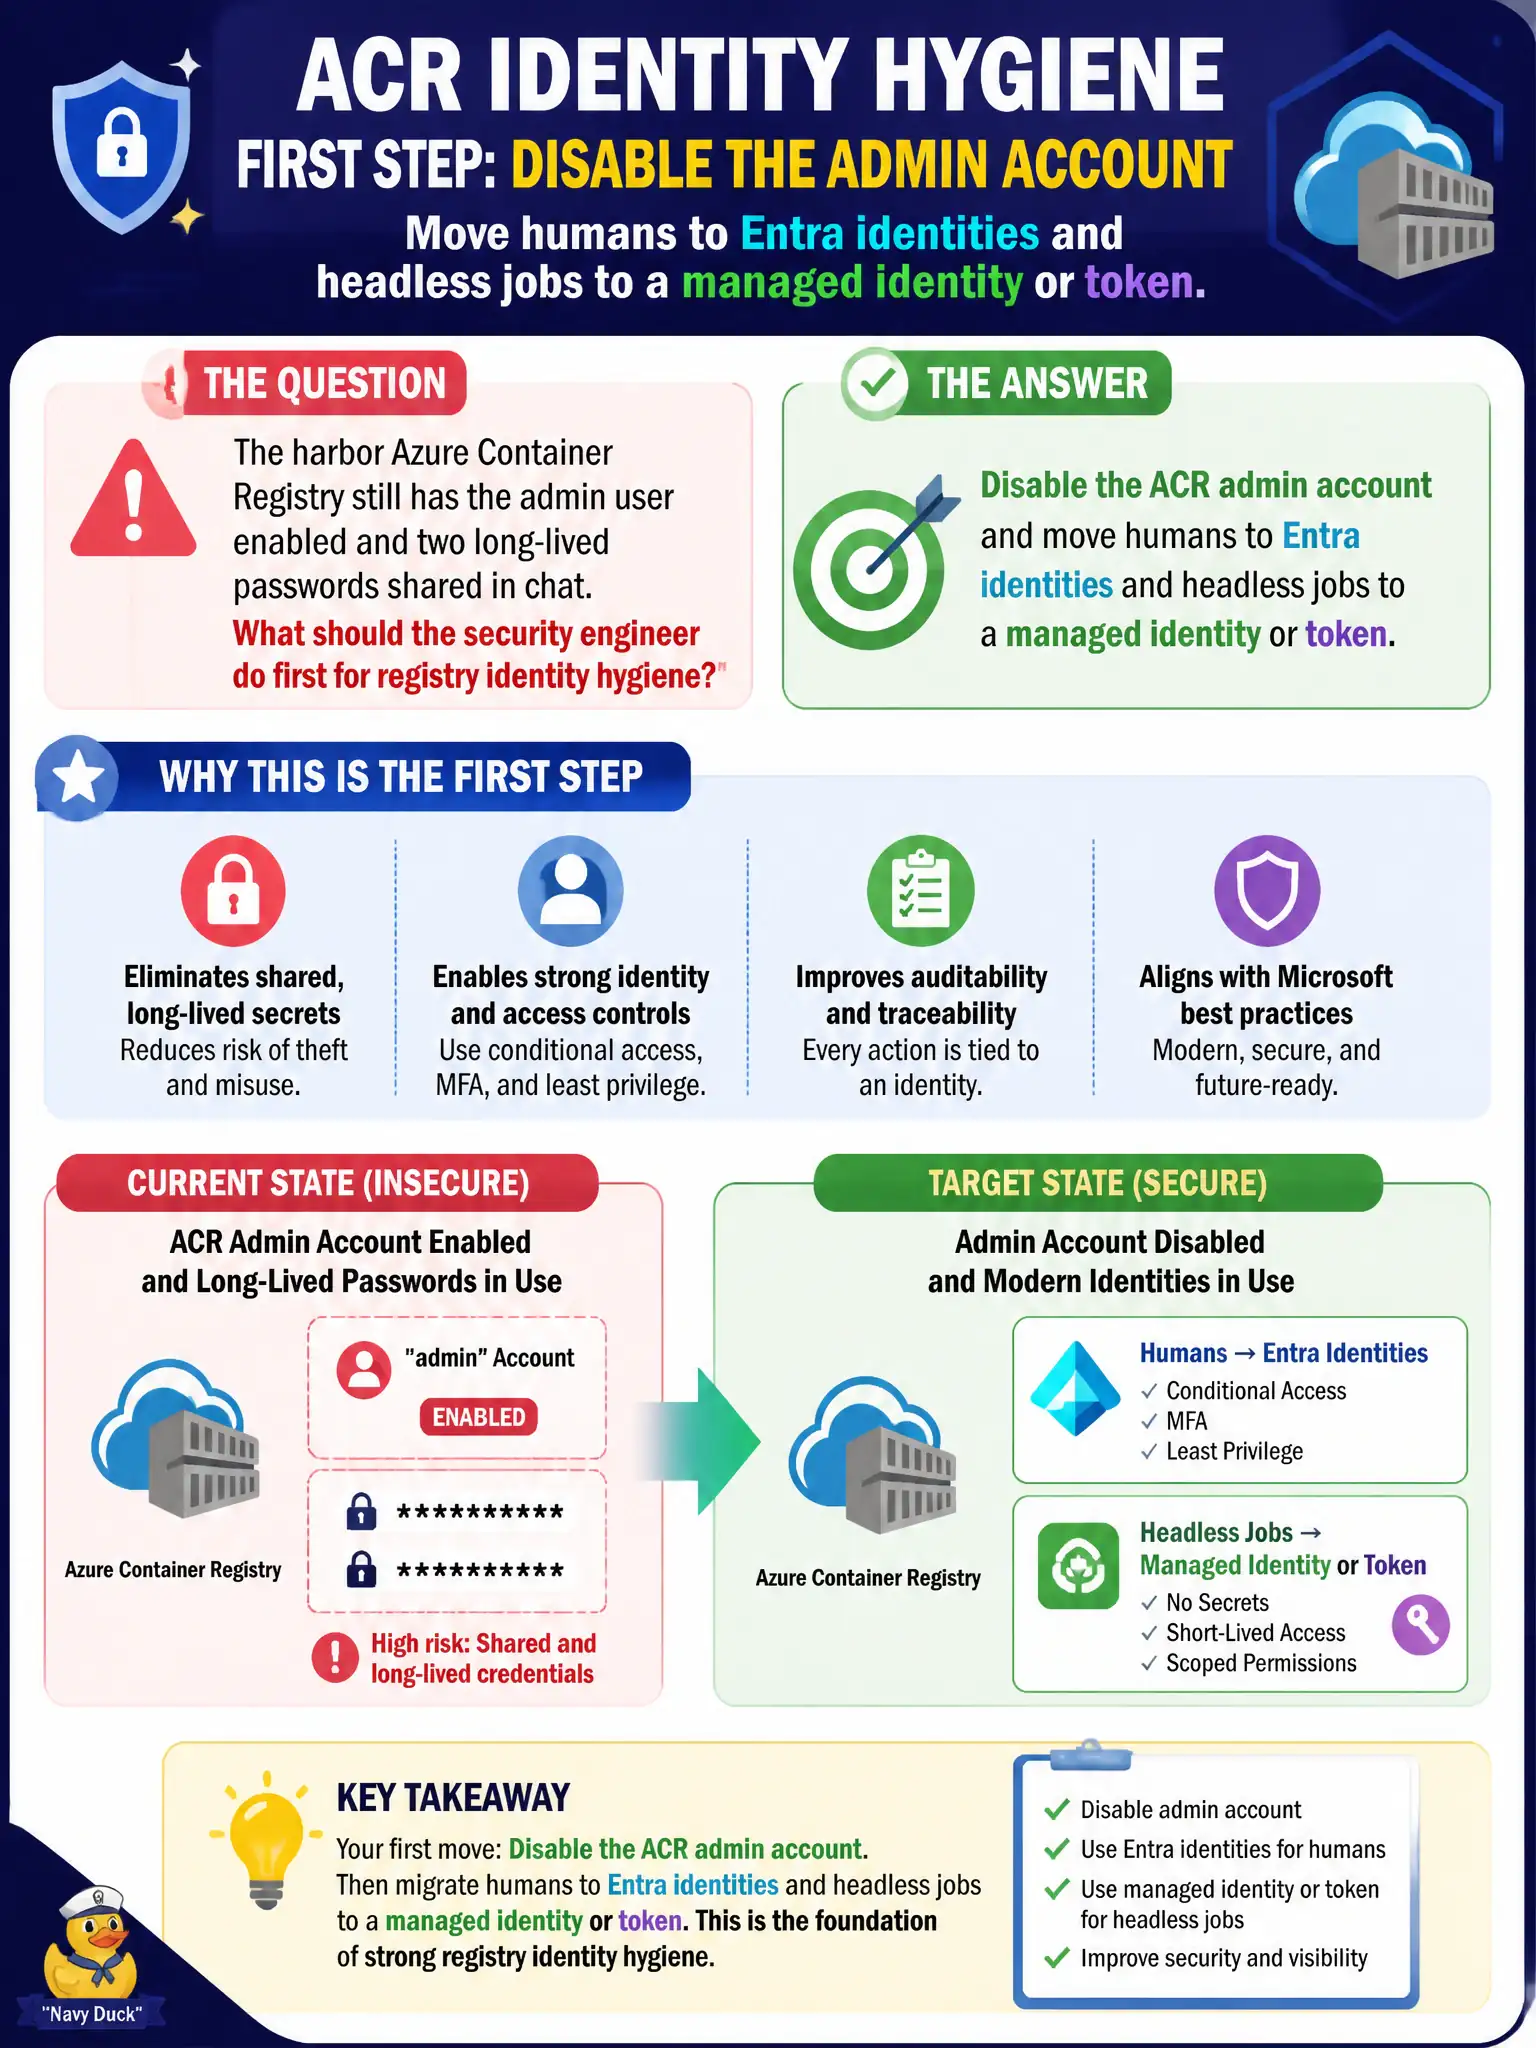
The harbor Azure Container Registry still has the admin user enabled and two long-lived passwords shared in chat. What should the security engineer do first for registry identity hygiene?
Select an answer to reveal the explanation.
Short Explanation
Two admin passwords in chat means the harbor registry still has the back-door account on. Disable ACR admin; people use Entra, pipelines use managed identity or tokens.
Full Explanation
Disable the ACR admin account first for registry identity hygiene when the harbor registry still has admin enabled and two long-lived passwords shared in chat. Humans should authenticate with Microsoft Entra identities; headless jobs and cluster pulls should use a managed identity or token. Turning off admin removes the shared back-door passwords that chat leaks have already made untenable for production.
Rotating Key Vault encryption keys used by unrelated storage accounts does nothing to the ACR admin user and fails the hygiene goal for the harbor registry. Keeping the admin user enabled as the supported production identity for all human and pipeline pulls is exactly the anti-pattern the question is eliminating. Storing both admin passwords in source control with a calendar reminder worsens secret sprawl instead of disabling the account.
Exam caveat: disable admin only after Entra users and managed identities or tokens are proven for pull and portal access, or you can break pipelines mid-cutover. Operational check: migrate one pipeline to managed identity with pull rights, migrate human access to Entra, disable ACR admin, and confirm authorized pulls and portal access still succeed while the former admin passwords no longer authenticate.