
AKS cannot pull tugboat images because someone pasted the Azure Container Registry admin password into a Kubernetes secret. How should the security engineer fix registry access?
Select an answer to reveal the explanation.
Short Explanation
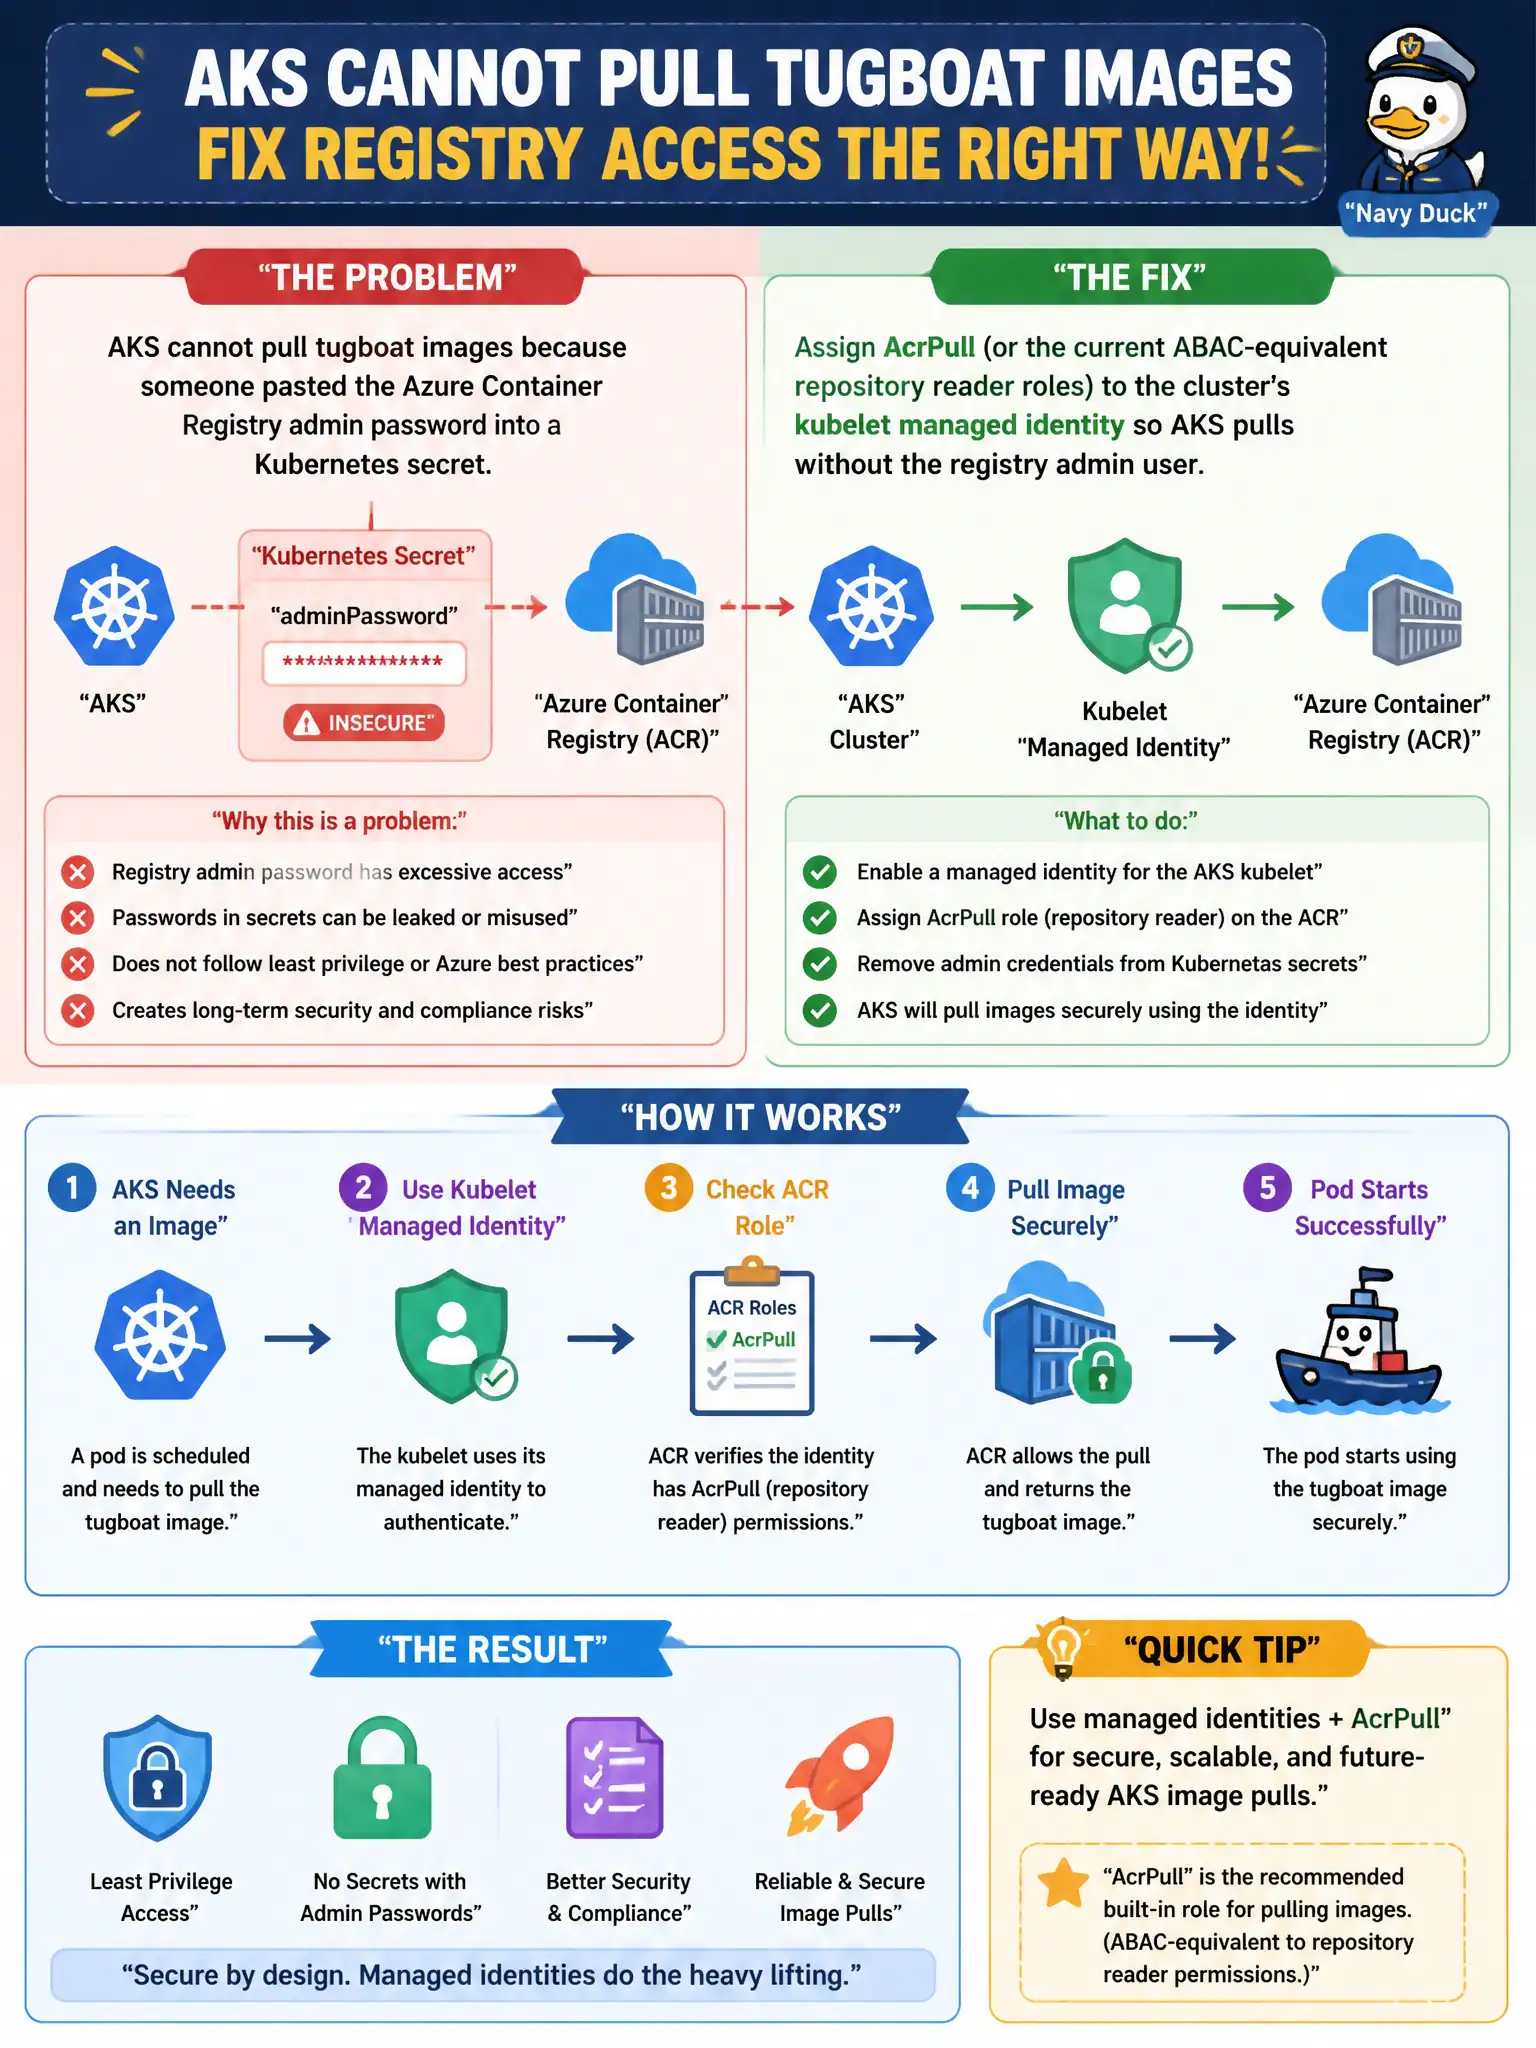
Paste-the-admin-password into a Secret is how tugboat images get stuck. Give the kubelet managed identity AcrPull (or today’s reader roles) and leave the ACR admin user out of production pulls.
Full Explanation
Assign AcrPull (or the current ABAC-equivalent repository reader roles) to the cluster’s kubelet managed identity so AKS can pull tugboat images without embedding the Azure Container Registry admin password in a Kubernetes secret. Identity-based pull removes the shared admin password from the cluster and aligns with least-privilege registry access.
Keeping the ACR admin password in the secret and rotating it each sprint still uses the powerful admin user as the production pull credential. Exposing the registry with anonymous pull on a public endpoint removes authentication entirely and is not an acceptable fix. Creating a Private Endpoint alone without any pull role on an identity fails by concept: private networking hides the data path but does not grant kubelet permission to authenticate and pull; you still need an identity with pull rights.
Exam caveat: AcrPull on the kubelet (or acr-pull style) identity is the classic pattern; newer ABAC repository roles may appear—grant pull-capable roles to the identity that actually pulls, not to random human Owners. Operational check: remove the admin-password secret from the cluster, confirm the kubelet identity has pull rights, restart a pull, and verify images import successfully without ACR admin credentials.