
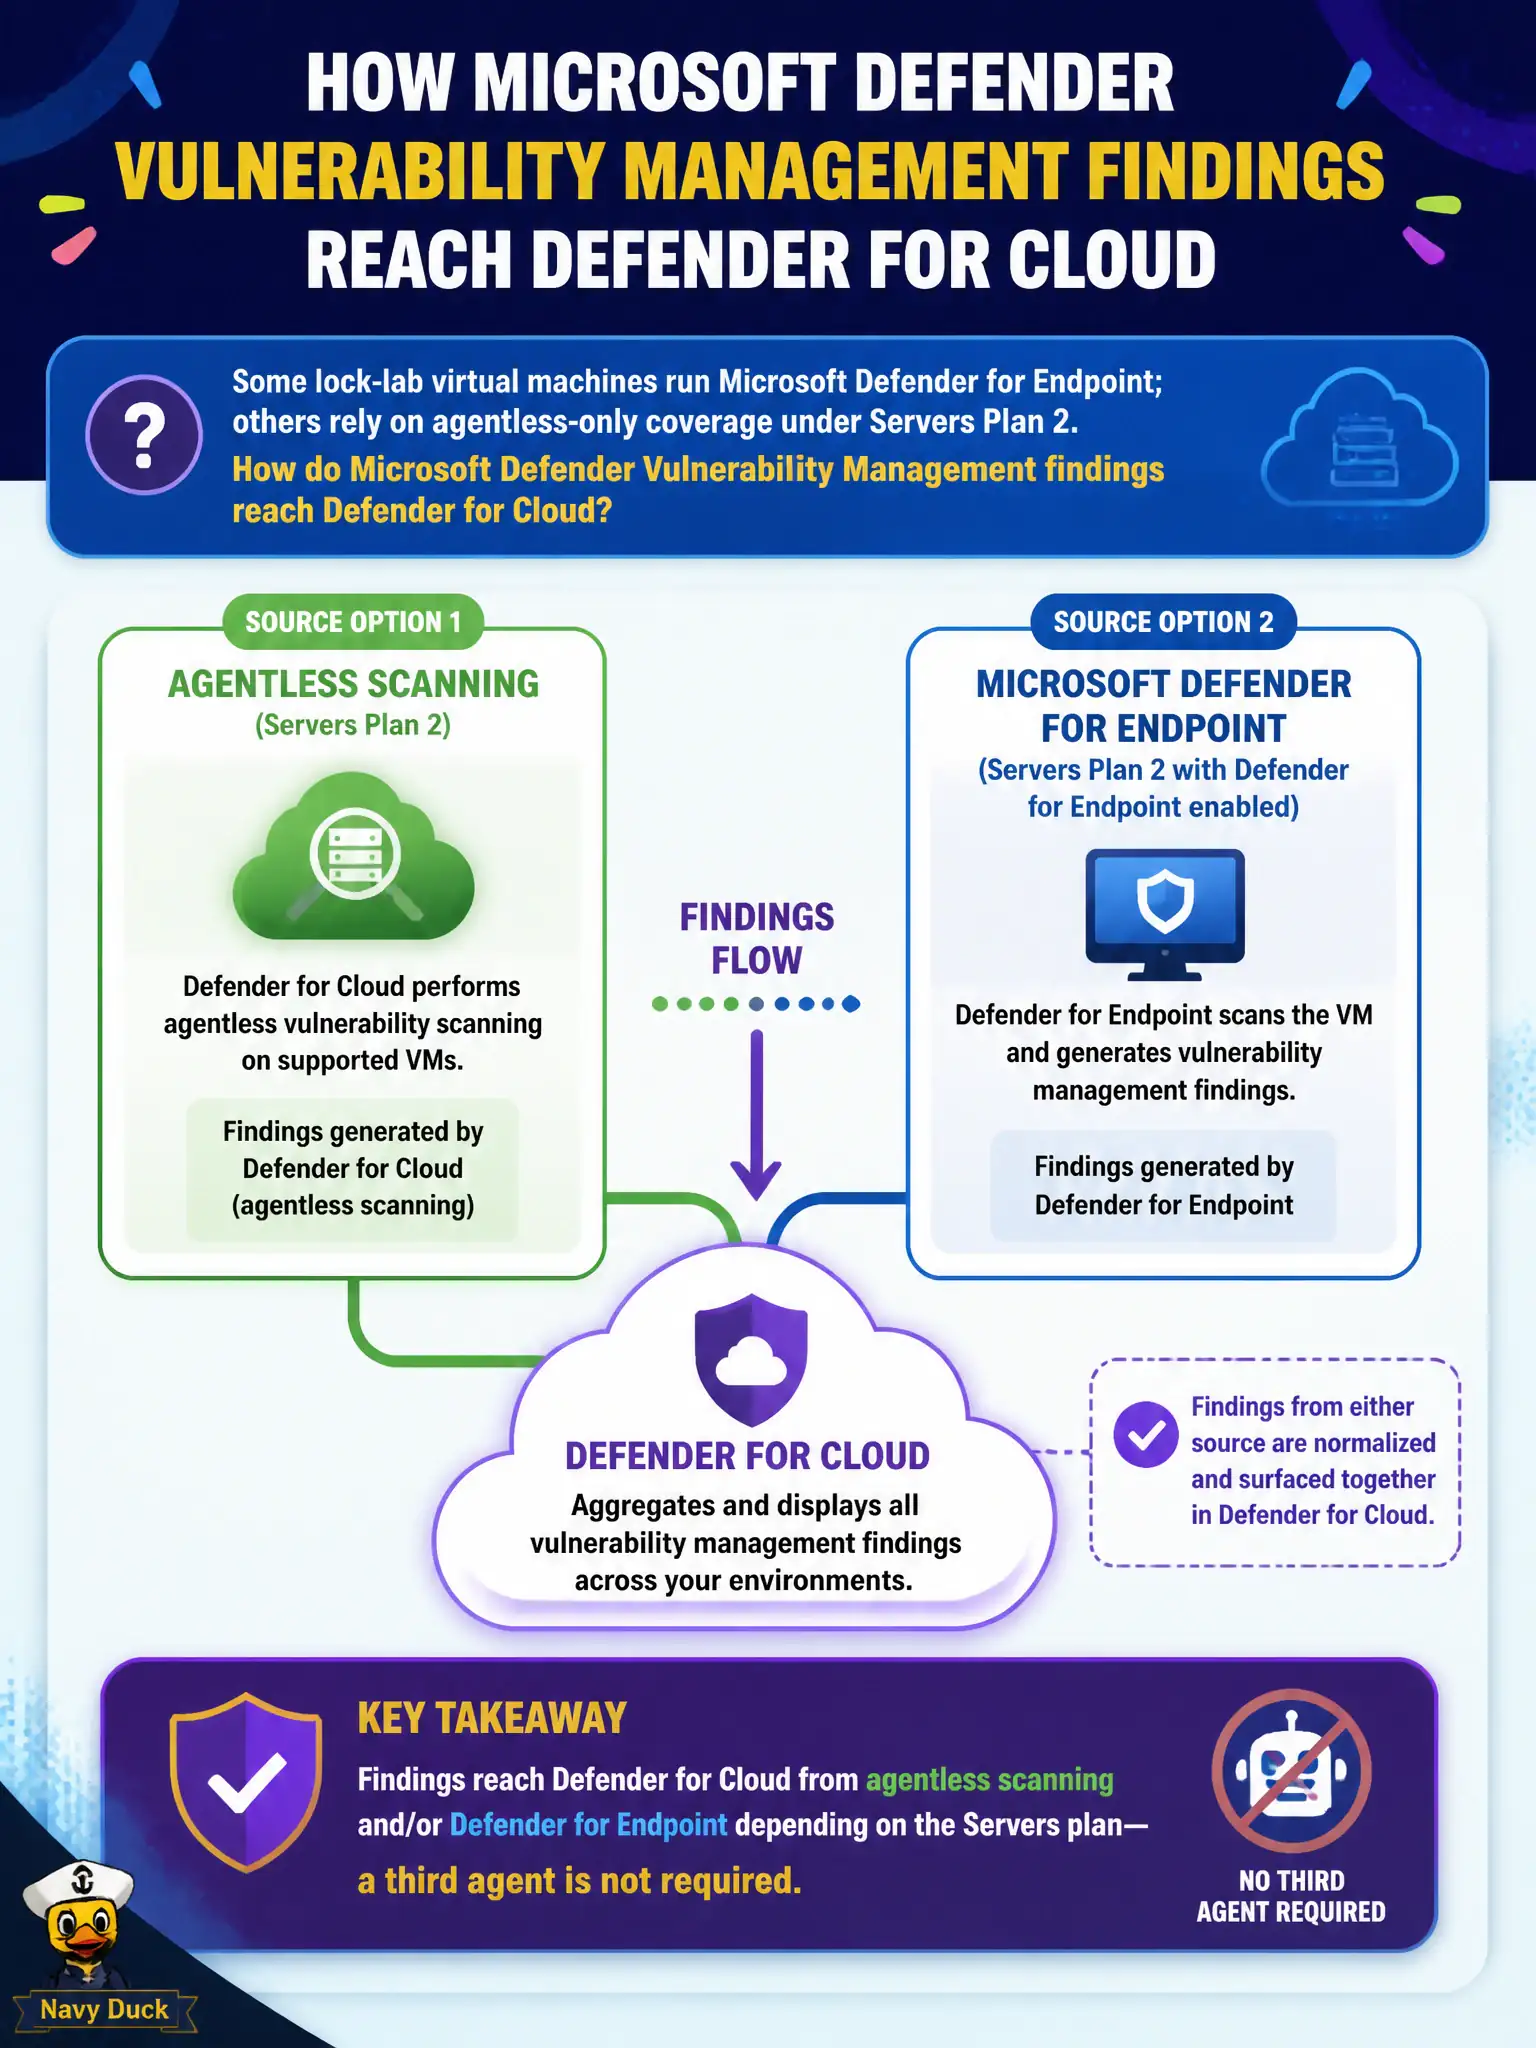
Some lock-lab virtual machines run Microsoft Defender for Endpoint; others rely on agentless-only coverage under Servers Plan 2. How do Microsoft Defender Vulnerability Management findings reach Defender for Cloud?
Select an answer to reveal the explanation.
Short Explanation
MDVM can ride agentless snapshots, Defender for Endpoint, or both—depending on the Servers plan. Nobody is forcing a third mystery agent onto every lock-lab VM.
Full Explanation
On estates where some lock-lab virtual machines run Microsoft Defender for Endpoint and others rely on agentless-only coverage under Servers Plan 2, Microsoft Defender Vulnerability Management findings reach Defender for Cloud from agentless scanning and/or Defender for Endpoint depending on the Servers plan. A separate third assessment agent is not required for that MDVM path.
Requiring installation of a mandatory third assessment agent on every virtual machine invents an extra agent AZ-500 does not mandate for MDVM via agentless or MDE. Claiming findings arrive only from Microsoft Defender for Office 365 mailbox scanning of VM names confuses email protection with machine vulnerability assessment. Expecting Security Copilot to invent CVE lists without Servers Plan features skips the actual assessment pipelines.
Exam caveat: mixed estates are normal; do not force MDE onto every plant VM if Plan 2 agentless coverage is the approved path—just understand which pipeline feeds each machine’s findings.
Operational check: for one MDE-onboarded VM and one agentless-only Plan 2 VM, confirm both show MDVM-related findings in Defender for Cloud and document which assessment path each machine uses.